
A logistics Catalyst SD-WAN edge has both an internet color and an MPLS color up. The cloud gateway is reachable on both, but the company wants the Azure prefix to prefer the internet TLOC. Which policy does that without removing MPLS?
Select an answer to reveal the explanation.
Short Explanation
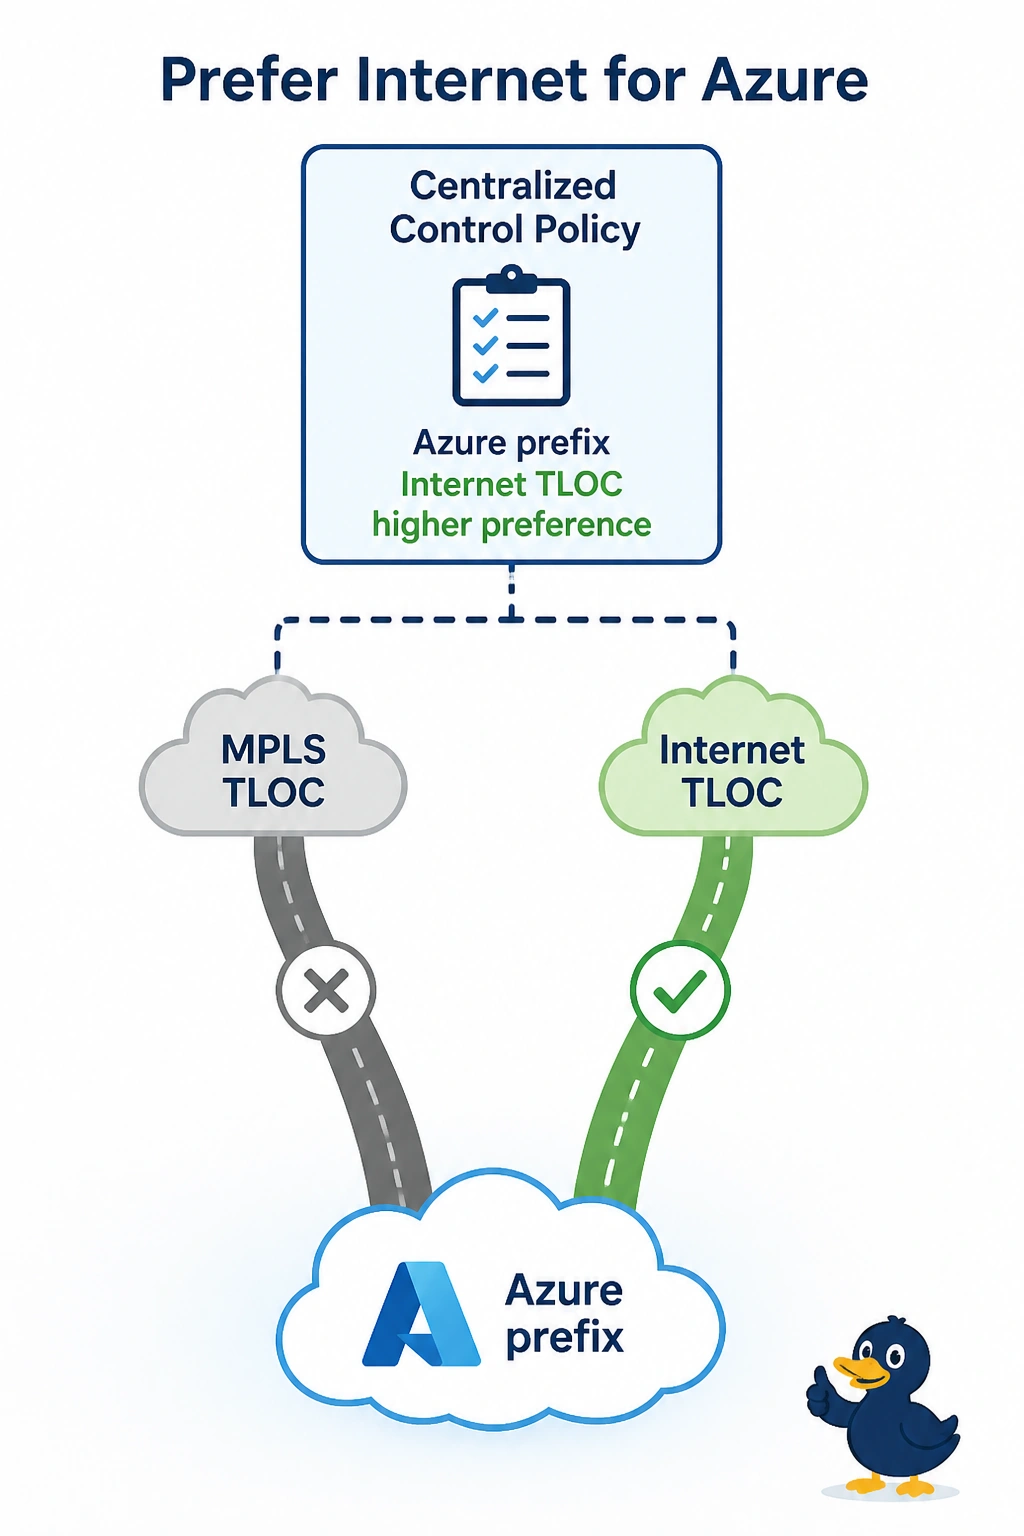
You want the internet door listed as the favorite, and you still want the MPLS door on the building. Set a higher TLOC preference for the internet path in control policy. Do not delete MPLS, and do not turn a routing preference into a firewall deny.
Full Explanation
Centralized control policy can set OMP TLOC preference so the Azure prefix is preferred over the internet path while the MPLS TLOC remains a usable alternate. That matches a preference that must not remove MPLS. A zone-based firewall that denies the prefix when it is learned from MPLS throws the backup away and does not change OMP preference. It also treats a route as a packet drop, which is the wrong tool. An application-aware routing policy that drops traffic unless internet loss is zero is a strict SLA. It can blackhole the application when the internet path is imperfect, and it does not leave MPLS installed as the preferred backup the company asked for. Cloud OnRamp for SaaS does not set TLOC preference for a private Azure prefix. It steers enabled public SaaS applications. Exam caveat: preference is compared only among routes the edge is allowed to keep. A later filter that rejects the MPLS TLOC would violate the request to keep it. Operational check: show sdwan omp routes for the Azure prefix should list the internet TLOC with the better preference and still list the MPLS TLOC as an alternate.