
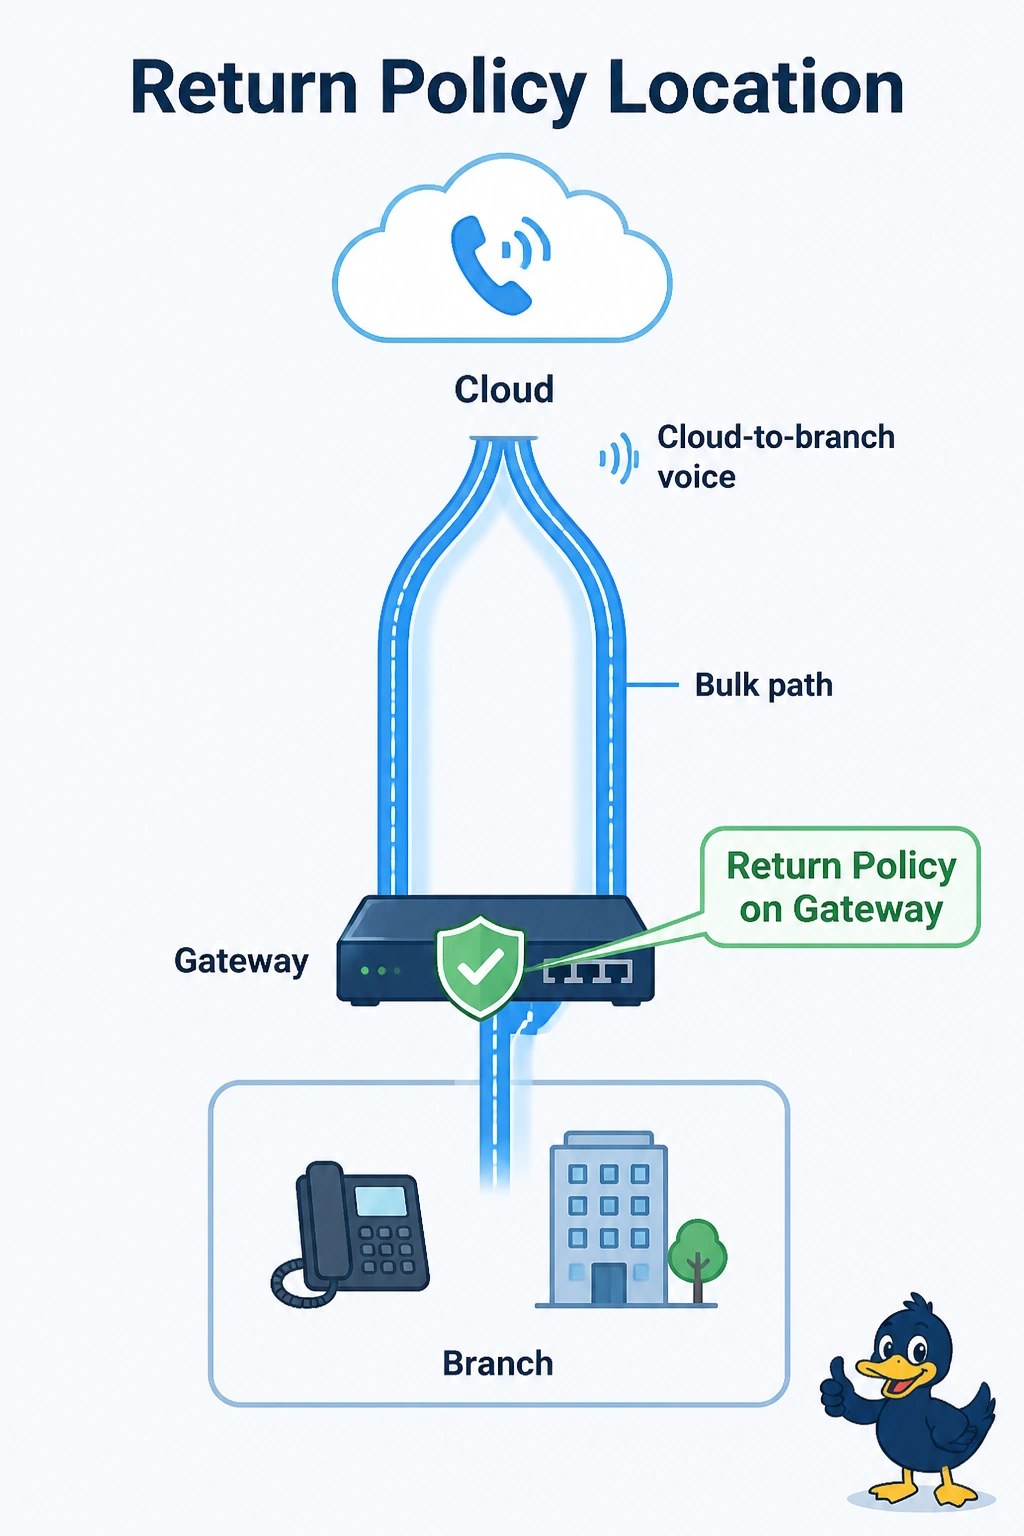
Branch-to-cloud voice follows the voice SLA. Cloud-to-branch voice uses the bulk path. The SLA is applied only on the branch. The gateway has no matching policy. Where is the return policy missing?
Select an answer to reveal the explanation.
Short Explanation
The trip out follows the voice rule, and the trip back is forwarded by a device that has no copy of that rule. You apply the voice policy on the gateway that sends cloud-to-branch voice. The branch policy cannot steer traffic it does not forward.
Full Explanation
Application-aware routing acts on the device that forwards the flow onto the overlay. The branch policy matches branch-to-cloud voice. Cloud-to-branch voice is forwarded by the gateway, which has no matching policy, so that direction follows the bulk path. Apply the voice SLA on the gateway. Adding another copy only on the branch does not see the return flow. A zone-based firewall does not set an SLA. The controller certificate does not carry an application list. Exam caveat: the gateway policy has to match the same voice traffic, in the direction the gateway forwards. A policy aimed at a different VPN on the gateway still leaves this return on the bulk path. Operational check: a cloud-to-branch call should take the voice path after the gateway policy is applied, and the branch-to-cloud call should stay on it.