
Two IPsec tunnels to AWS are up. The preferred route points at tunnel 1, whose decrypt counter stays at zero while encrypt increases. Tunnel 2's encrypt and decrypt counters both move. Users fail. What should the route prefer?
Select an answer to reveal the explanation.
Short Explanation
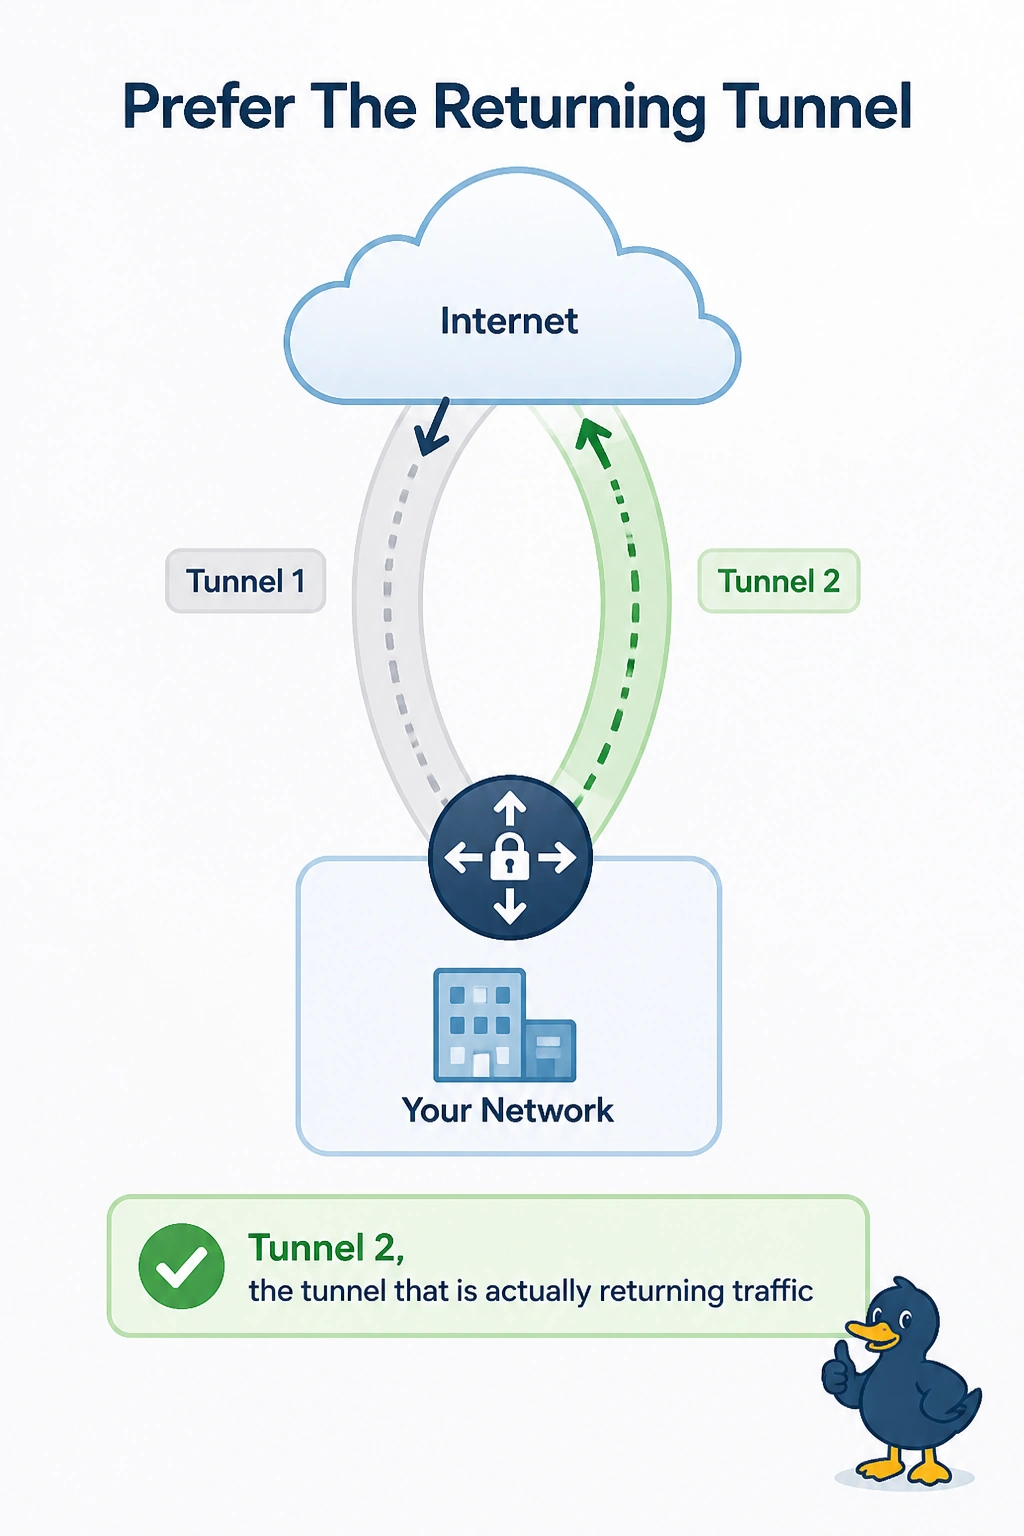
You keep sending the mail down a tunnel that never sends anything back. You prefer tunnel 2, where encrypt and decrypt both move. A decrypt counter stuck at zero means the return is not on that SA.
Full Explanation
Encrypt without decrypt means packets leave on that SA and the replies do not come back on it. Tunnel 1 is the preferred route and shows that pattern, so users fail. Tunnel 2 shows both counters moving, which means it is the path actually returning traffic. Prefer tunnel 2. A zero decrypt counter is not a healthy return. The virtual private gateway does not have an OSPF path that owns these counters. The IKE lifetime does not tell you which tunnel is returning packets. The counters do. Exam caveat: prefer the tunnel whose counters both move. A campus route aimed at the silent tunnel keeps the failure even while that tunnel's IKE stays up. Operational check: the VPC route should point at tunnel 2, and a new ping should increment both of that tunnel's counters.