
A clinic tunnel to an AWS virtual private gateway shows rising encrypt and decrypt counters. Ping to a VPC instance works. The instance's application port still fails, and its security group does not allow that port from the clinic prefix. What is the fault?
Select an answer to reveal the explanation.
Short Explanation
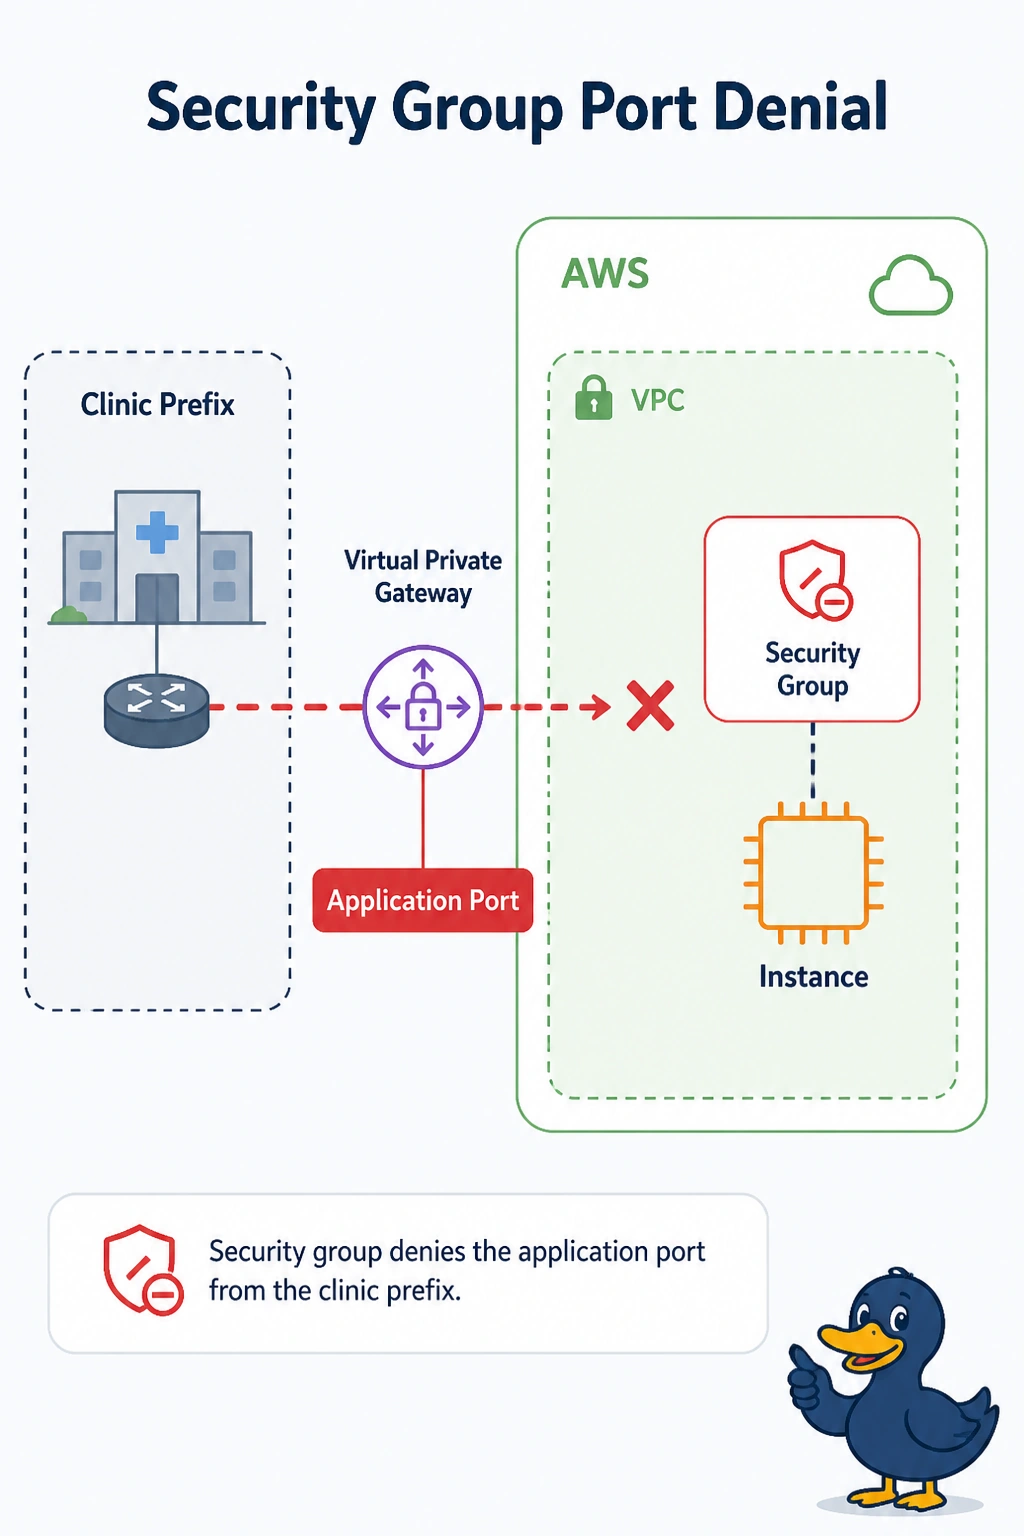
You can see the tunnel carrying traffic in both directions, and ping to the instance succeeds. The security group denies the application port from the clinic prefix, so check that rule; a down IPsec SA would not carry the ping or increase both counters.
Full Explanation
Rising encrypt and decrypt counters show that traffic is passing through the IPsec tunnel in both directions, and a successful ping confirms that the instance is reachable over the VPN. The application connection fails because the instance security group does not allow that port from the clinic prefix. Security groups filter traffic to the instance, so this rule accounts for the port-specific failure while allowing ping. A down IPsec SA would not carry the successful ping or produce rising traffic counters in both directions. A BGP withdrawal of the clinic prefix would undermine the route needed for communication with the clinic, which is inconsistent with the working ping and increasing decrypt counter. OSPF filtering is not the cause: a virtual private gateway does not run OSPF to filter application ports. Exam caveat: a successful ping confirms reachability for that protocol, not permission for every application port; check the relevant rule for the specific port. Practical check: add an inbound security group rule allowing the application port from the clinic prefix, then retry the connection and confirm the tunnel counters continue to rise.