
A Catalyst SD-WAN edge could ping its controllers and then lost every control connection at the certificate expiry shown on the device. OMP went empty. The internet circuit is still up. What expired?
Select an answer to reveal the explanation.
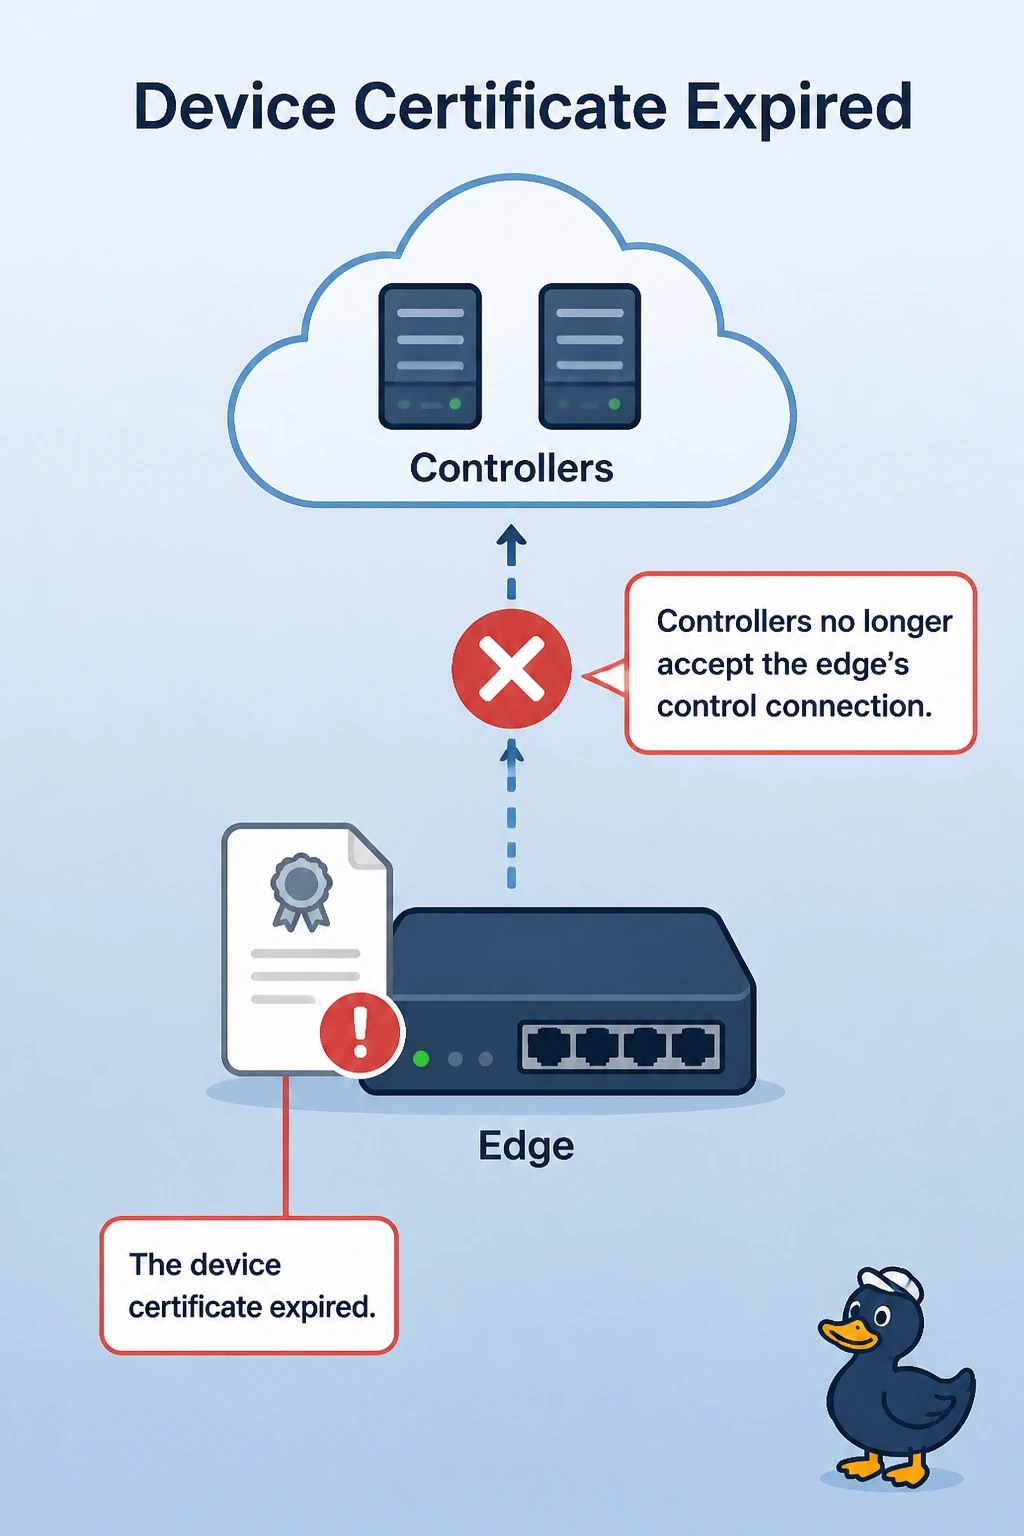
Short Explanation
The path to the controllers is still there, but the badge that gets you in has expired. Your device certificate expired at the time shown on the device, so the controllers reject the control connections even though ping still works. An AWS virtual private gateway’s IKE pre-shared key is not the badge the controllers check.
Full Explanation
Catalyst SD-WAN control connections authenticate with the device certificate. When that certificate expires, the controllers reject the edge even though the underlay can still ping them. OMP empties because the sessions that carry it are gone. Renewing or reinstalling the certificate can restore the control connections. An IKE pre-shared key on an AWS virtual private gateway belongs to a native IPsec tunnel; it is not the authenticator for SD-WAN control, and OMP does not ride that gateway. A BGP hold timer toward Azure is not the certificate lifetime and does not determine whether the controllers accept the edge. The SaaS probe list does not keep control connections up: those probes need the overlay and do not create it. Exam caveat: a device clock set far enough wrong can make a valid certificate appear expired, so check the clock if the certificate’s expiry date is still in the future. Practical check: confirm the certificate validity covers today, then use “show sdwan control connections” to verify recovery and check that OMP routes repopulate.