
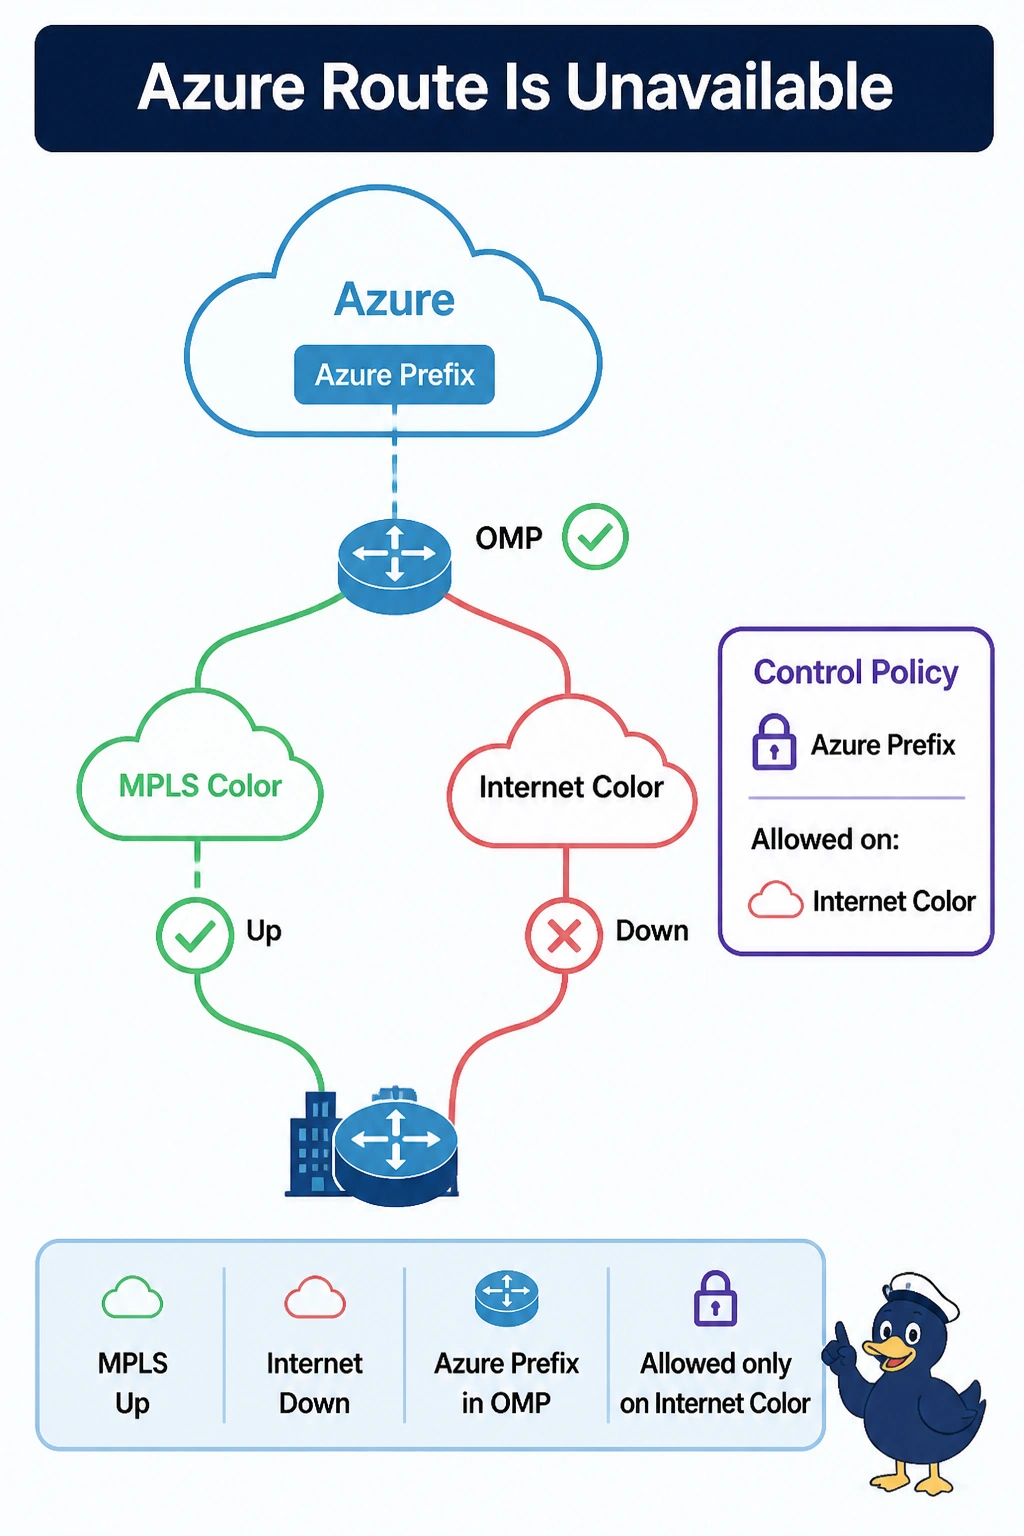
A branch has MPLS up and its internet color down. A centralized control policy restricts the Azure prefix to the internet color only. The prefix is in OMP and traffic to Azure fails. Why?
Select an answer to reveal the explanation.
Short Explanation
You locked the shipment to a door that is boarded up, and a perfectly good door is right beside it. You restricted the Azure prefix to the internet color, and that color is down, so the route cannot forward. MPLS is up and was never allowed to carry it.
Full Explanation
Centralized control policy can restrict a prefix to a TLOC color. This policy allows the Azure prefix only on the internet color. That color is down, so the OMP route is present and still unusable. MPLS is up and was excluded by the restriction. A zone-based firewall would show drops after a working route was installed. The MPLS color was not allowed to install a working Azure route. Application-aware routing strict mode does not withdraw an OMP route because MPLS loss is zero. Zero loss would be a healthy path, and strict is a forwarding action, not an OMP filter. A failed SIG credential affects internet-inspection tunnels. It does not remove an Azure prefix that is still visible in OMP and tied to a color. Exam caveat: restricting to a color is useful when that color is the intended path and a backup color should not be used. Here the only allowed color is down, so the restriction is the outage. Operational check: show sdwan omp routes for the Azure prefix should show the internet color with the TLOC down, and after the policy also permits MPLS the same prefix should forward.