
A plant IOS XE router has an up IPsec SA to one AWS tunnel. The encrypt counter increases when hosts send traffic, and the decrypt counter stays at zero. The VPC route for the plant points at the other tunnel, which is down. What does that explain?
Select an answer to reveal the explanation.
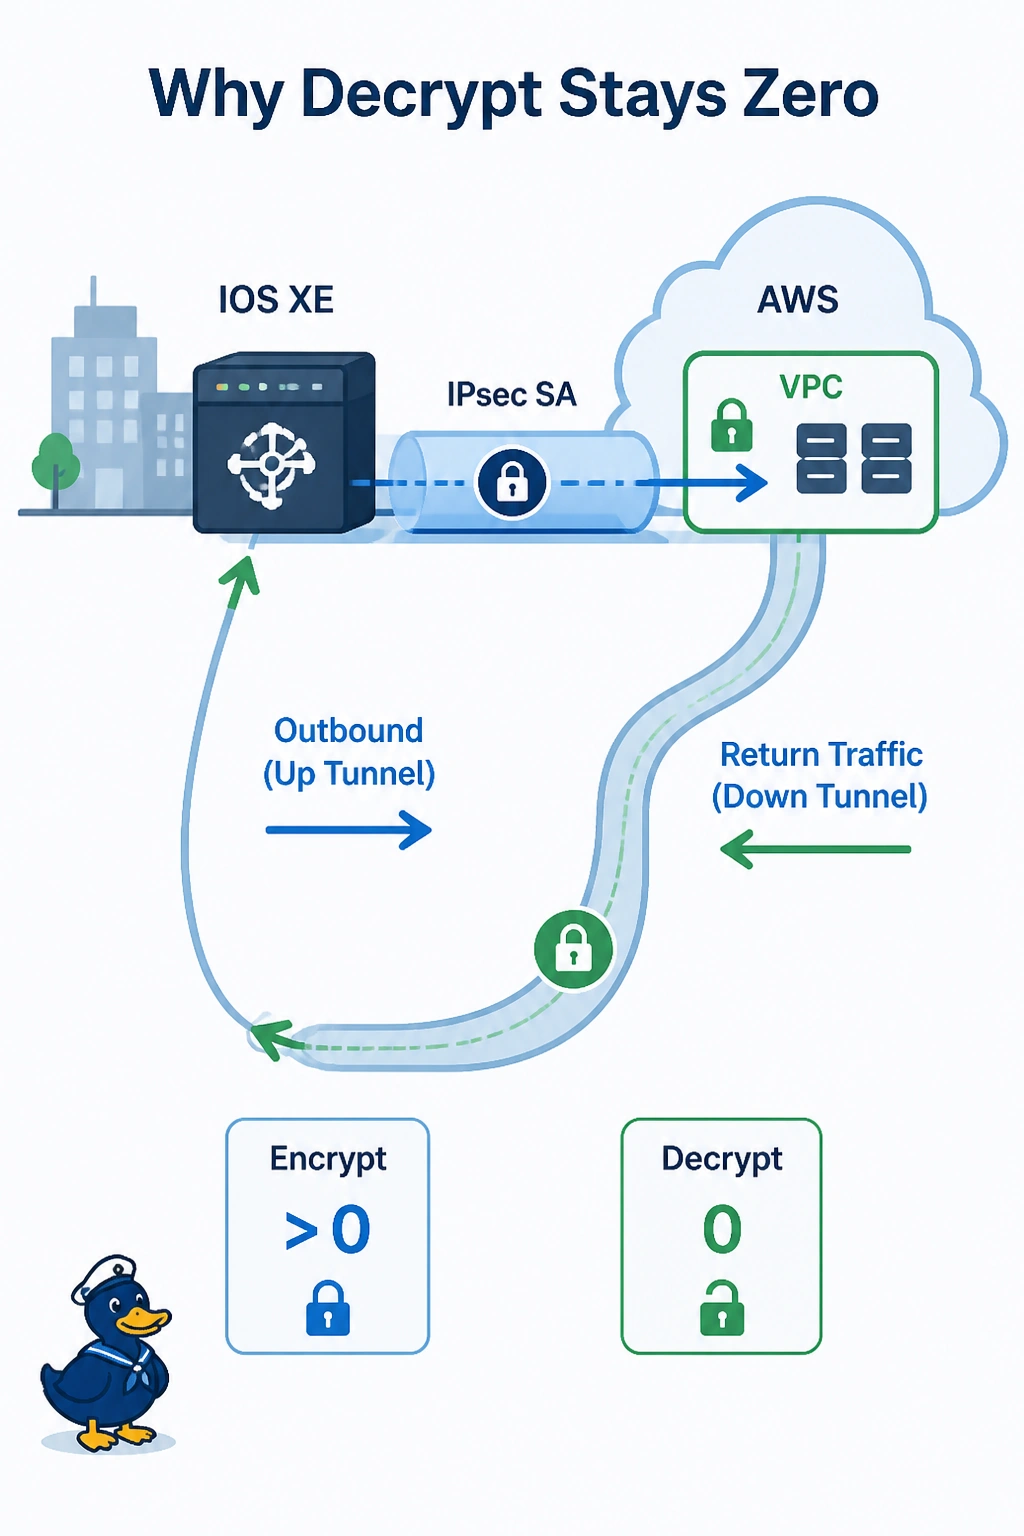
Short Explanation
You keep throwing letters into a mailbox that never sends one back. You are encrypting toward a healthy SA, and AWS is trying to answer on the other tunnel, which is down, so the decrypt counter stays at zero. A wrong pre-shared key would not have built this SA.
Full Explanation
Encrypt counters prove the plant is sending packets into this security association. Decrypt counters stay at zero when the matching return packets never arrive on it. The VPC route for the plant prefix points at the other tunnel, and that tunnel is down, so AWS forwards the replies into a dead path. Move the VPC route, or the BGP preference, to the tunnel that is up and the decrypt counter can rise. A wrong pre-shared key would have prevented the SA. This SA is up, so authentication already succeeded. The virtual private gateway does not run OSPF and does not hash packets into an SA that way. TCP MSS clamping changes segment size. It does not zero out decrypt counters while encrypt counters move, and it would affect both directions of a flow that actually returns. Exam caveat: AWS can prefer either tunnel of the connection. Check the route on the AWS side, not only the router, when one direction is missing. Operational check: after the VPC route targets the up tunnel, the decrypt counter on that SA should increment and a two-way trace should complete.