
A manufacturer's IOS XE router shows an IKEv2 SA in a ready state to an AWS virtual private gateway, but no IPsec SA forms and no cloud traffic passes. What should the engineer check next?
Select an answer to reveal the explanation.
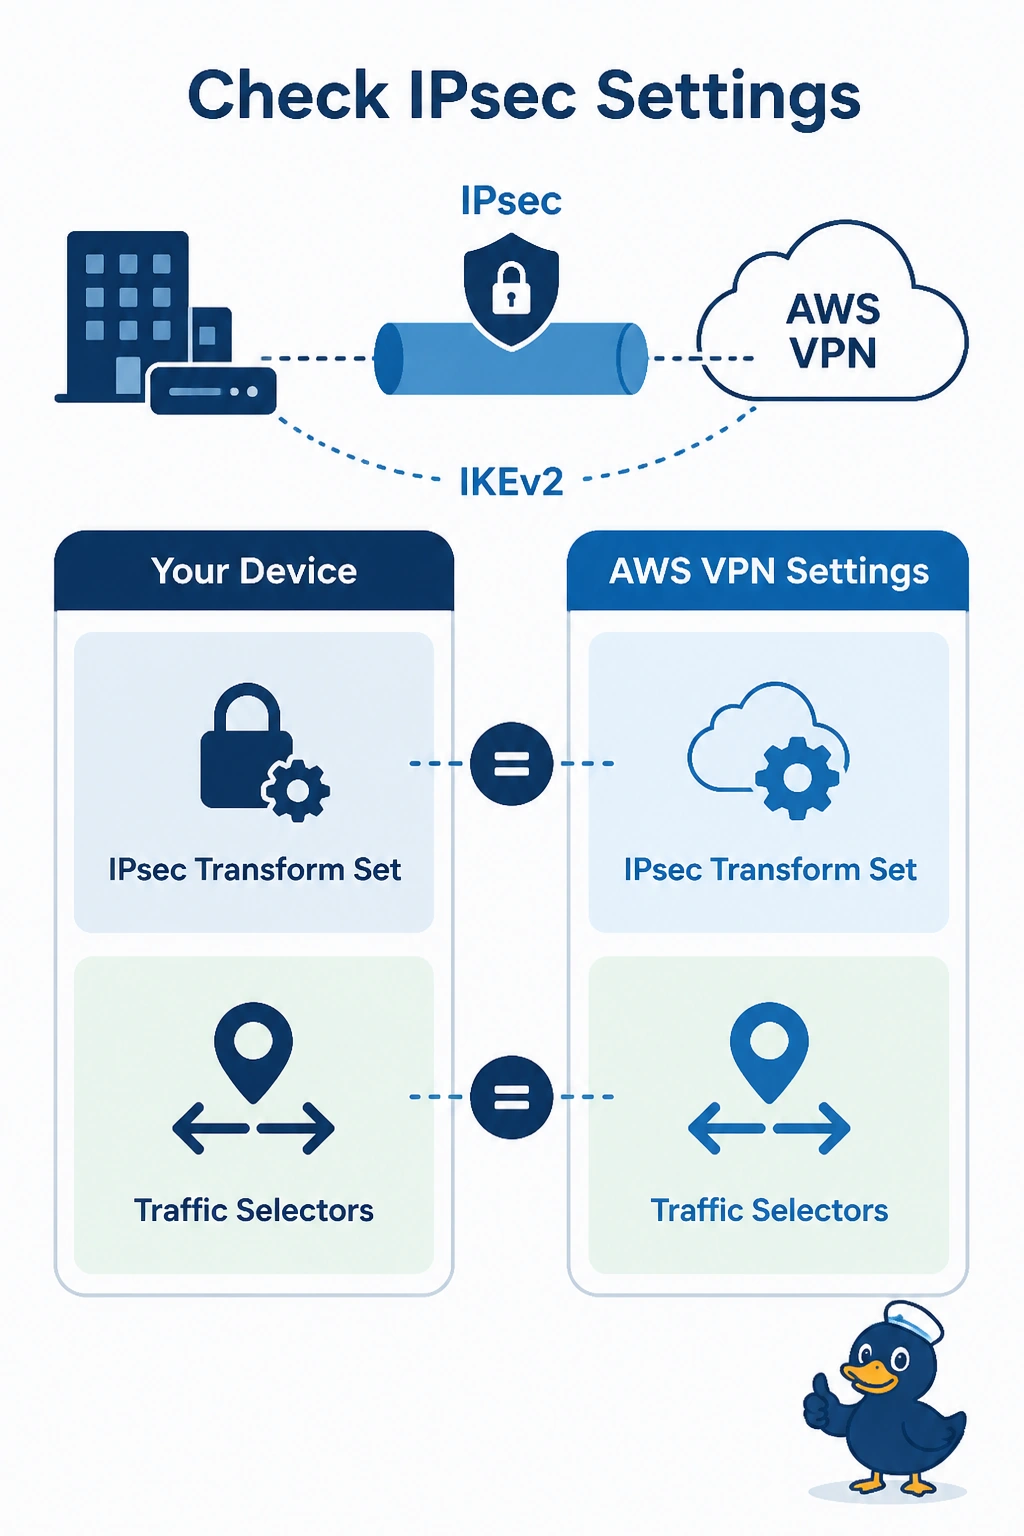
Short Explanation
You have IKE, but the inner IPsec tunnel has not formed yet. Check the transform set and traffic selectors against the AWS VPN settings before changing routing timers. BGP runs inside IPsec, while OSPF and OMP do not negotiate this AWS tunnel.
Full Explanation
An IKEv2 SA in a ready state means phase 1 completed: the peers agreed on the IKE policy and authenticated. Traffic still needs an IPsec security association. When that SA does not form, a common mismatch with a native AWS VPN is the IPsec transform set or the traffic selectors, also called proxy identities. AWS route-based tunnels expect the selectors and proposals configured for the VPN connection, so compare those settings first. The BGP hold timer is not involved yet: BGP runs inside the IPsec tunnel, so it cannot establish before the tunnel or cause the missing IPsec SA. The OSPF dead interval on the campus LAN interface facing the virtual private gateway has nothing to negotiate with that gateway, which does not run OSPF. An SD-WAN OMP graceful-restart timer applies to a Catalyst SD-WAN edge; this is a standalone IOS XE router, so there is no OMP session to adjust. Exam caveat: if the IPsec SA is up but routes are missing, stop checking transforms and investigate BGP or static routing. Practical check: run show crypto ipsec sa on the router and inspect the AWS VPN tunnel details; the encryption, integrity, and selector ranges should match.