
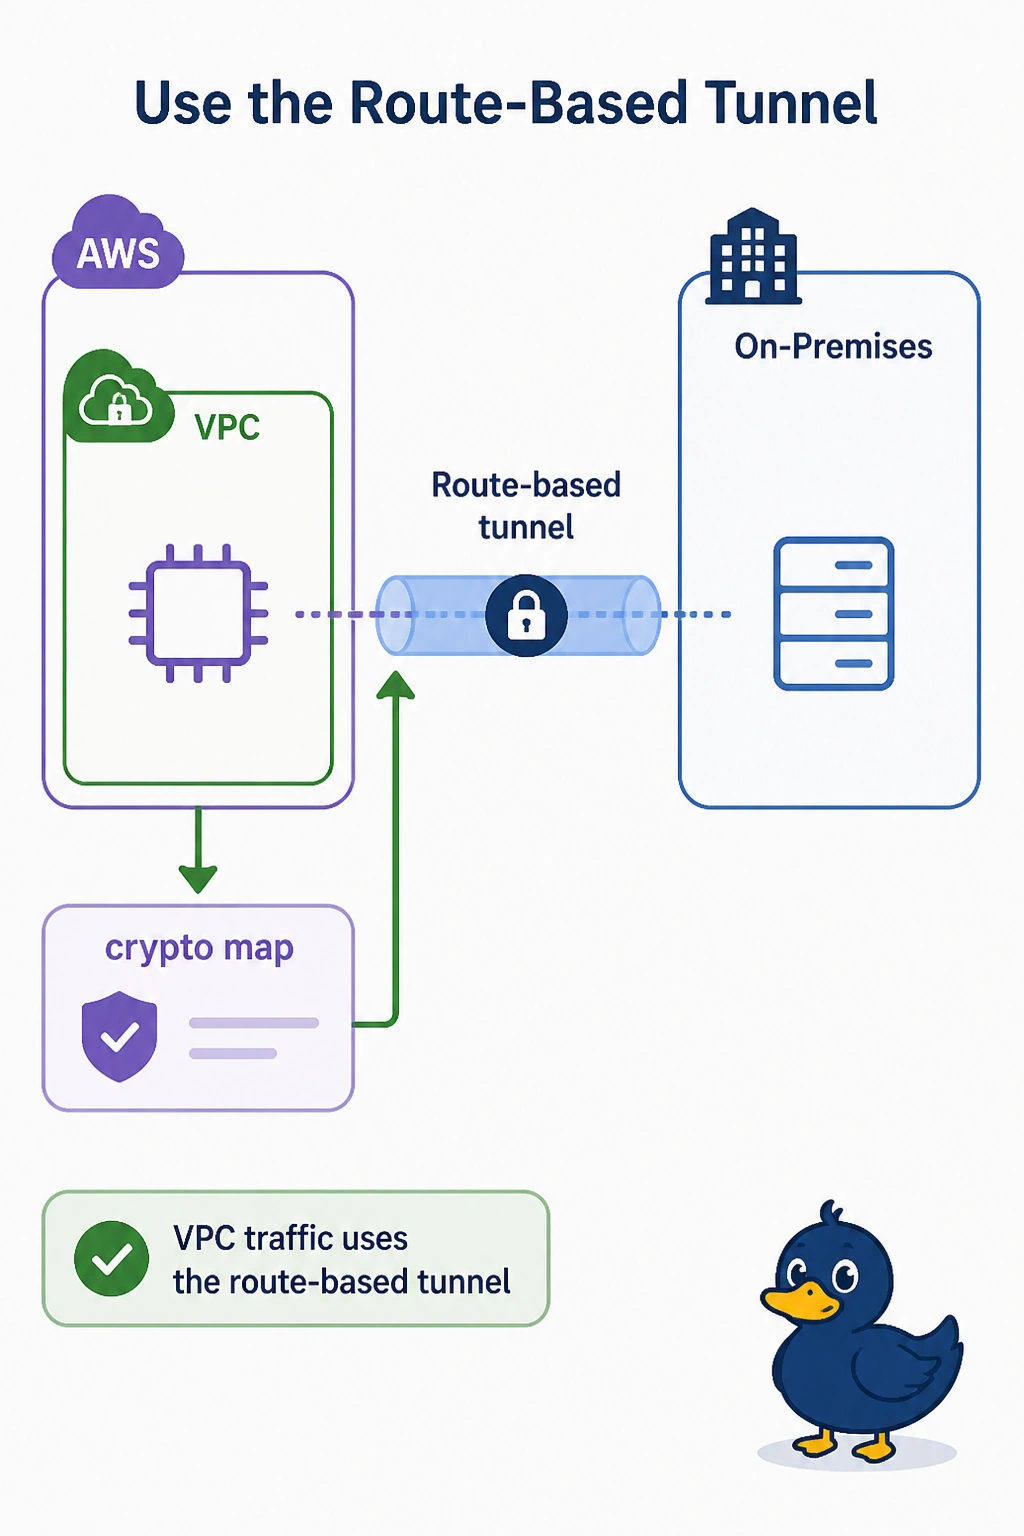
A route-based tunnel to AWS is up and idle. A crypto map on the physical internet interface matches the VPC prefixes, and that map's SA is the one carrying traffic. Users fail when the map's peer is wrong. What should be removed?
Select an answer to reveal the explanation.
Short Explanation
An old map on the outside interface is grabbing the traffic your tunnel was built to carry. You remove the crypto map so the VPC route can use the route-based tunnel. The map's peer is the wrong one, which is why users fail.
Full Explanation
A crypto map on the physical interface can match the VPC prefixes and build its own SA before those packets are routed into the VTI. The route-based tunnel stays up and idle, and users follow the map toward the wrong peer. Remove the crypto map and let the route into the tunnel carry the traffic. A crypto map is not required toward a native AWS VPN. The route-based tunnel is the fit. The virtual private gateway did not build the map, and it does not run OSPF. Removing the tunnel's IPsec profile would leave the tunnel unprotected. It would not stop the map from matching. Exam caveat: after the map is gone, confirm no other map or policy route still matches the VPC prefixes on the outside interface. Operational check: the map should be gone, the tunnel's encaps counter should rise, and the old map SA should not.