
Pings across a cloud IOS XE tunnel work. Application TCP fails. An inbound ACL on the tunnel permits ICMP and denies everything else. The SA is up. What should the ACL permit?
Select an answer to reveal the explanation.
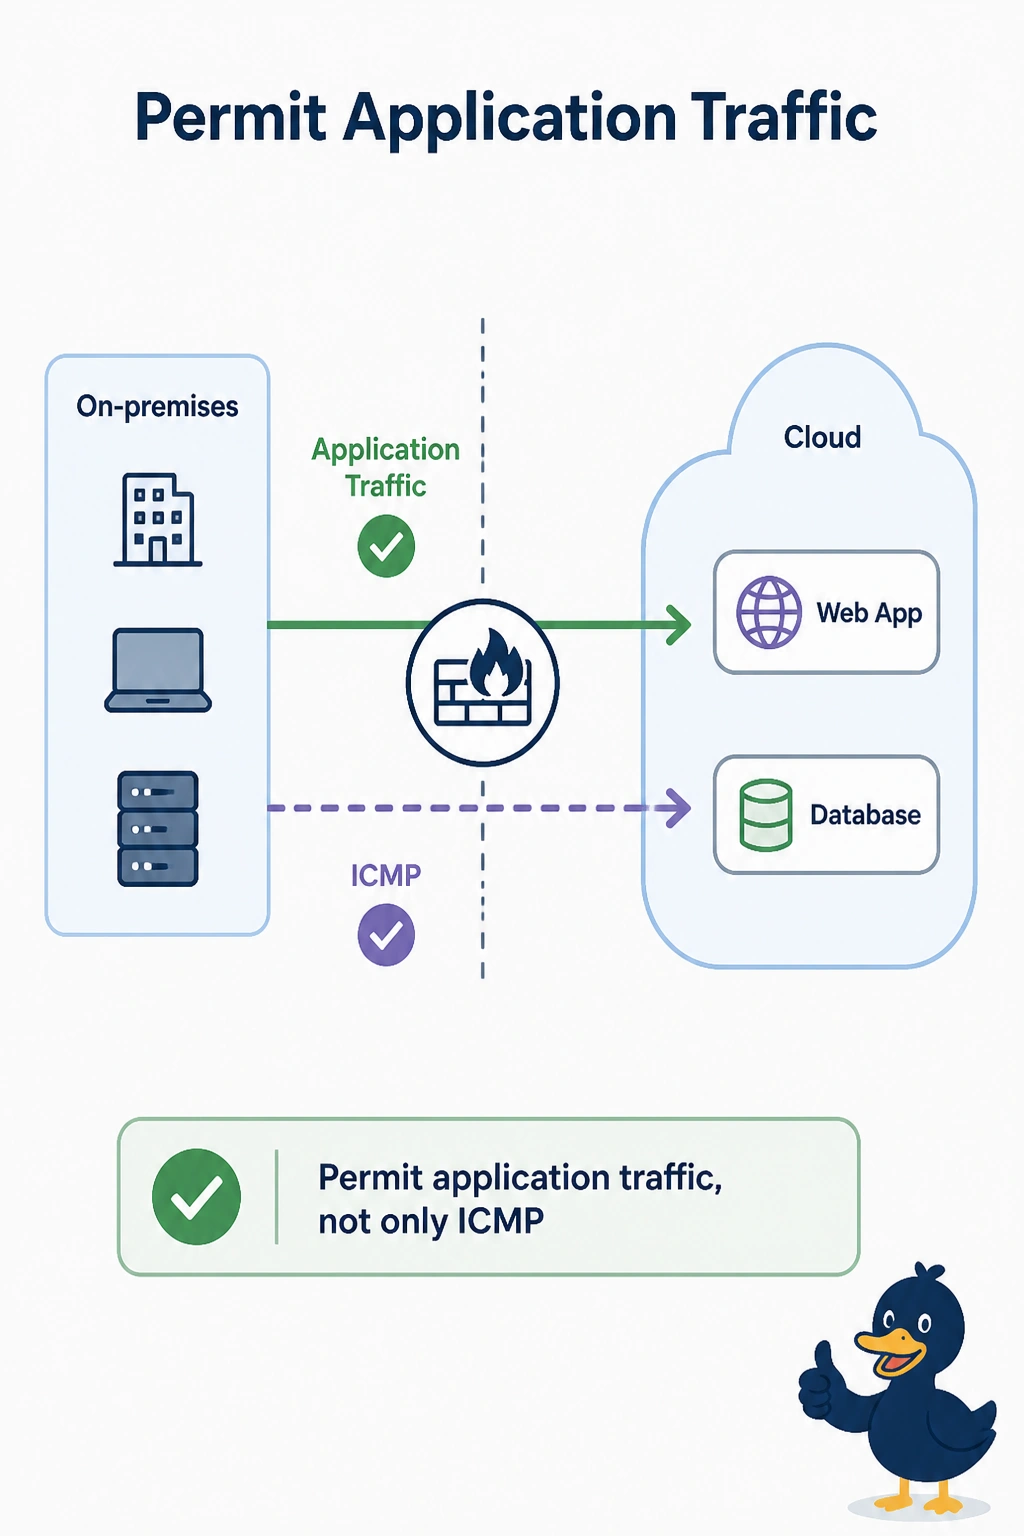
Short Explanation
The tunnel is open and the filter on it only recognizes a ping. You permit the application traffic on that ACL. An IPsec SA does not exempt TCP from an inbound list that denies everything else.
Full Explanation
An inbound ACL on the tunnel is applied to traffic that has already been decrypted. ICMP is permitted, so pings work. Everything else is denied, so application TCP fails while the SA stays up. Add a permit for the application. The SA does not skip the ACL. The virtual private gateway is not in this router-to-router path and does not run OSPF to bypass the list. A shorter IKE lifetime does not punch a hole through a deny. Exam caveat: permit the return traffic too if the ACL is applied in both directions. A permit for the request with the reply still denied looks like a one-way failure. Operational check: the ACL should show hits on the application permit, and a user session should cross the tunnel.