
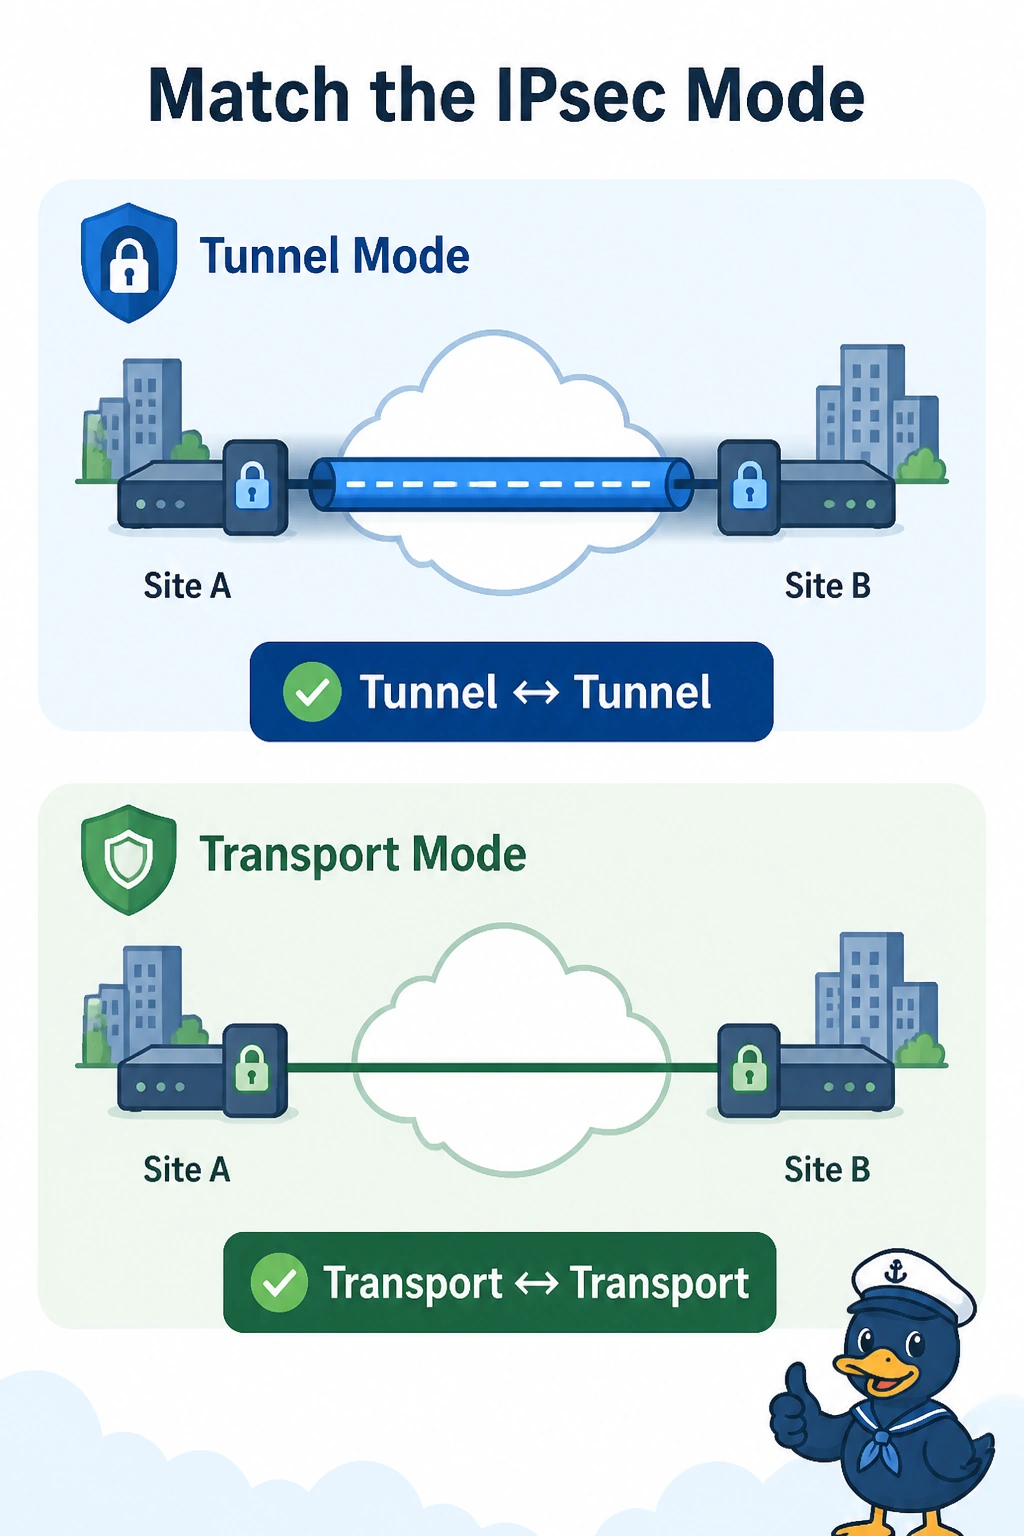
Campus and cloud IOS XE routers fail to form an IPsec SA. One offers transport mode and the other offers tunnel mode. The pre-shared key matches. What must match?
Select an answer to reveal the explanation.
Short Explanation
The password matches and the two sides are wrapping the packet differently. You make the IPsec mode match, tunnel with tunnel or transport with transport. A matching key does not paper over a mode the other router will not accept.
Full Explanation
IPsec negotiates a mode as part of the proposal. Transport on one side and tunnel on the other never produces an SA, even when the pre-shared key is right. Set both to tunnel mode, which is the usual choice when the tunnel carries routed traffic between these routers, or set both to transport if that is truly what both ends support. The BGP ASN does not select the mode. The OSPF hello timer is not a mode number. Anti-replay does not convert one mode into the other. It runs only after an SA exists. Exam caveat: a matching mode with a cipher or group the other router rejects still fails. Compare the rest of the proposal if the SA stays down. Operational check: both profiles should show the same mode, and show crypto ipsec sa should list an SA.