
Campus and cloud IOS XE routers have a GRE tunnel that is up. Tunnel protection is configured on a different, unused tunnel. A capture shows the GRE payload in the clear. What must move?
Select an answer to reveal the explanation.
Short Explanation
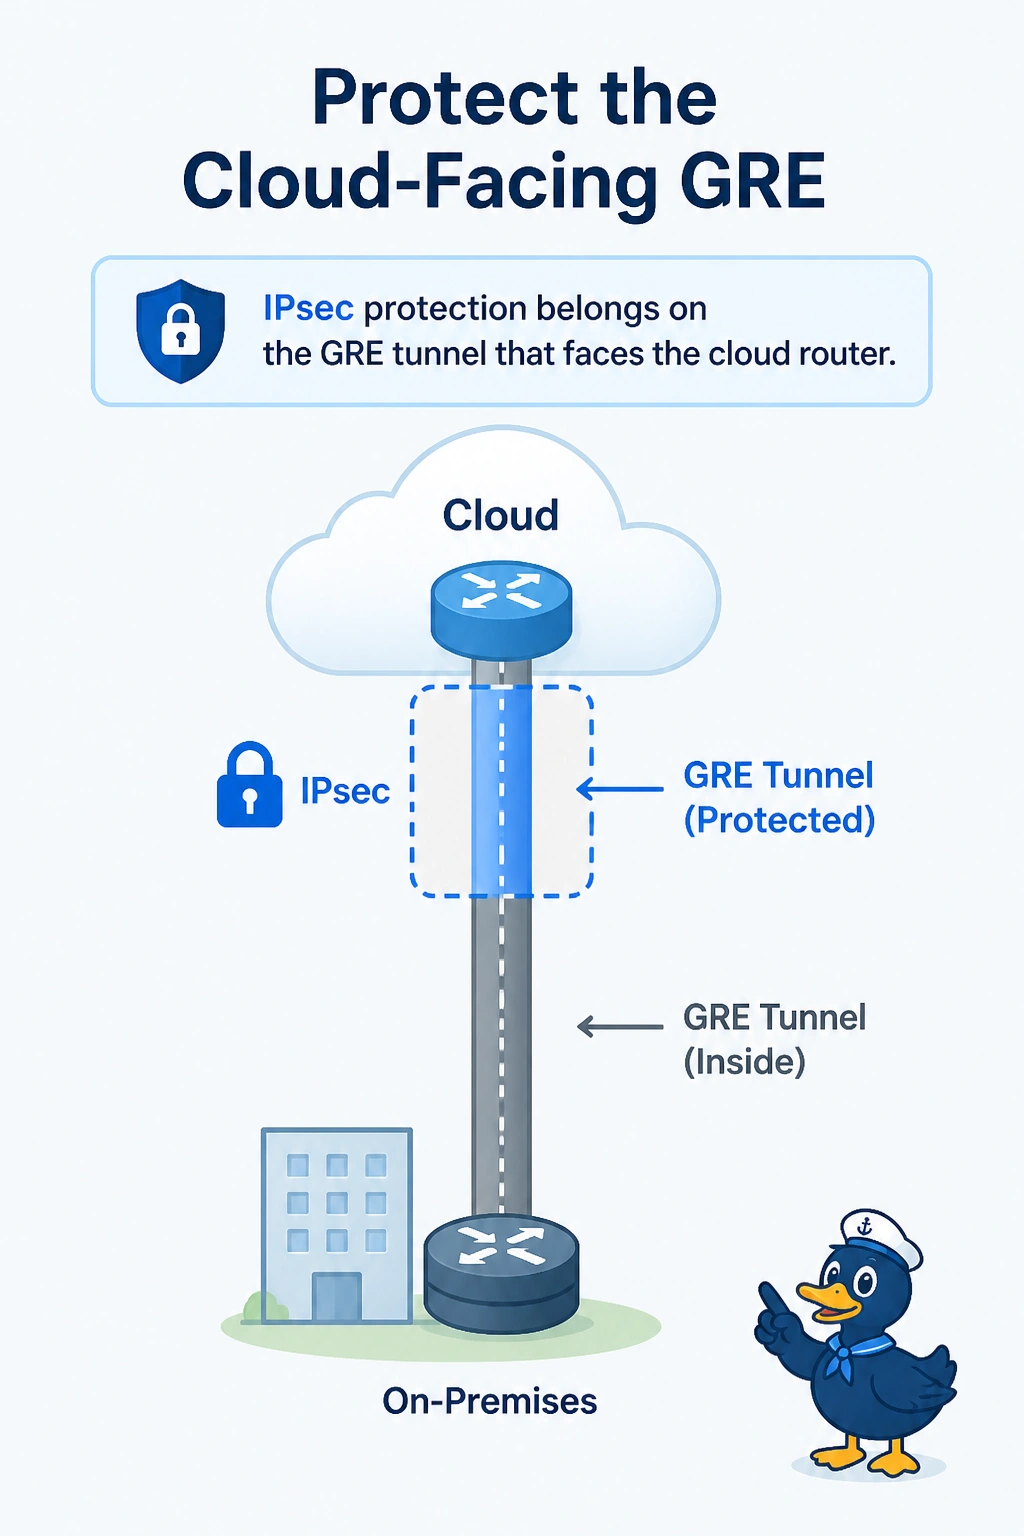
You locked a door the traffic never uses. You move the IPsec protection onto the GRE tunnel that faces the cloud router. OSPF and BGP do not encrypt the payload the capture can already read on the live tunnel.
Full Explanation
Tunnel protection applies to the interface it is configured on. The live GRE tunnel has no protection, so the payload is readable, and the profile sitting on an unused tunnel encrypts nothing that matters. Move the profile to the GRE tunnel that faces the cloud router, and use a matching profile on that peer. Putting the unused tunnel into OSPF only advertises routes out an idle interface. It does not encrypt the GRE packets already on the wire. A BGP ASN on the unused tunnel has the same problem. The capture is not wrong. It shows the unprotected tunnel. Changing the filter to ignore that traffic would hide the failure. Exam caveat: after you move the profile, the far end has to expect IPsec on this GRE tunnel. A peer that still expects cleartext GRE will drop the protected packets. Operational check: a capture outside the tunnel should show ESP or UDP 4500, and the unused tunnel should no longer be the one with the profile.