
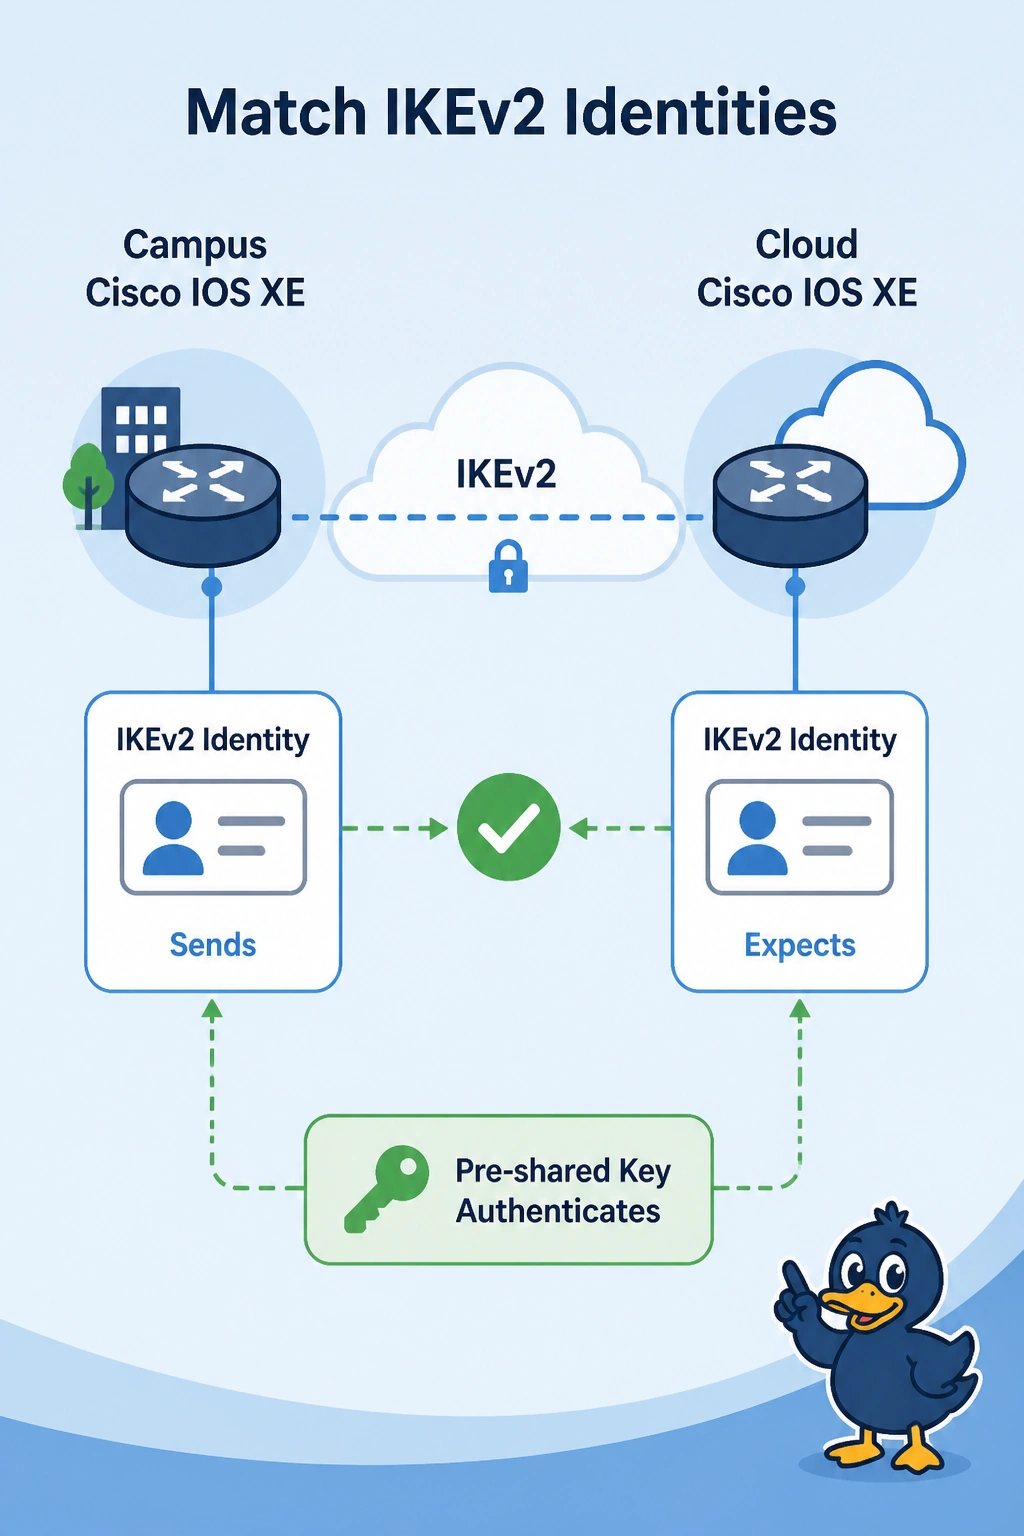
Campus and cloud Cisco IOS XE routers use the same pre-shared key and IKEv2. The campus router presents a hostname. The cloud router expects the campus public address. IKE fails. What must agree?
Select an answer to reveal the explanation.
Short Explanation
The password matches and the name on the badge does not. You make the identity the campus router sends the same identity the cloud router expects. Equal BGP ASNs are not the identity check, and the tunnel numbers do not have to match.
Full Explanation
IKEv2 checks the identity as well as the pre-shared key. A matching key with a hostname on one side and a public address expected on the other fails authentication. Change the campus identity to the public address, or change the cloud router to expect the hostname. One of them has to move. OSPF process IDs are not sent as IKEv2 identities. BGP ASNs are not required to be equal for this check. eBGP wants them different later. Tunnel interface numbers are local labels. They do not have to match across the two routers, and they are not the identity. Exam caveat: NAT can make an address identity fail if the cloud router expects the private source instead of the public source it actually sees. Expect the address that arrives. Operational check: the IKEv2 profile on the campus router should present the identity the cloud peer is configured to accept, and show crypto ikev2 sa should reach ready.