
IKEv2 to a Google Cloud HA VPN gateway is up. The IPsec SA never forms. The transform set on the IOS XE router is not one the HA VPN tunnel will accept. What must be aligned?
Select an answer to reveal the explanation.
Short Explanation
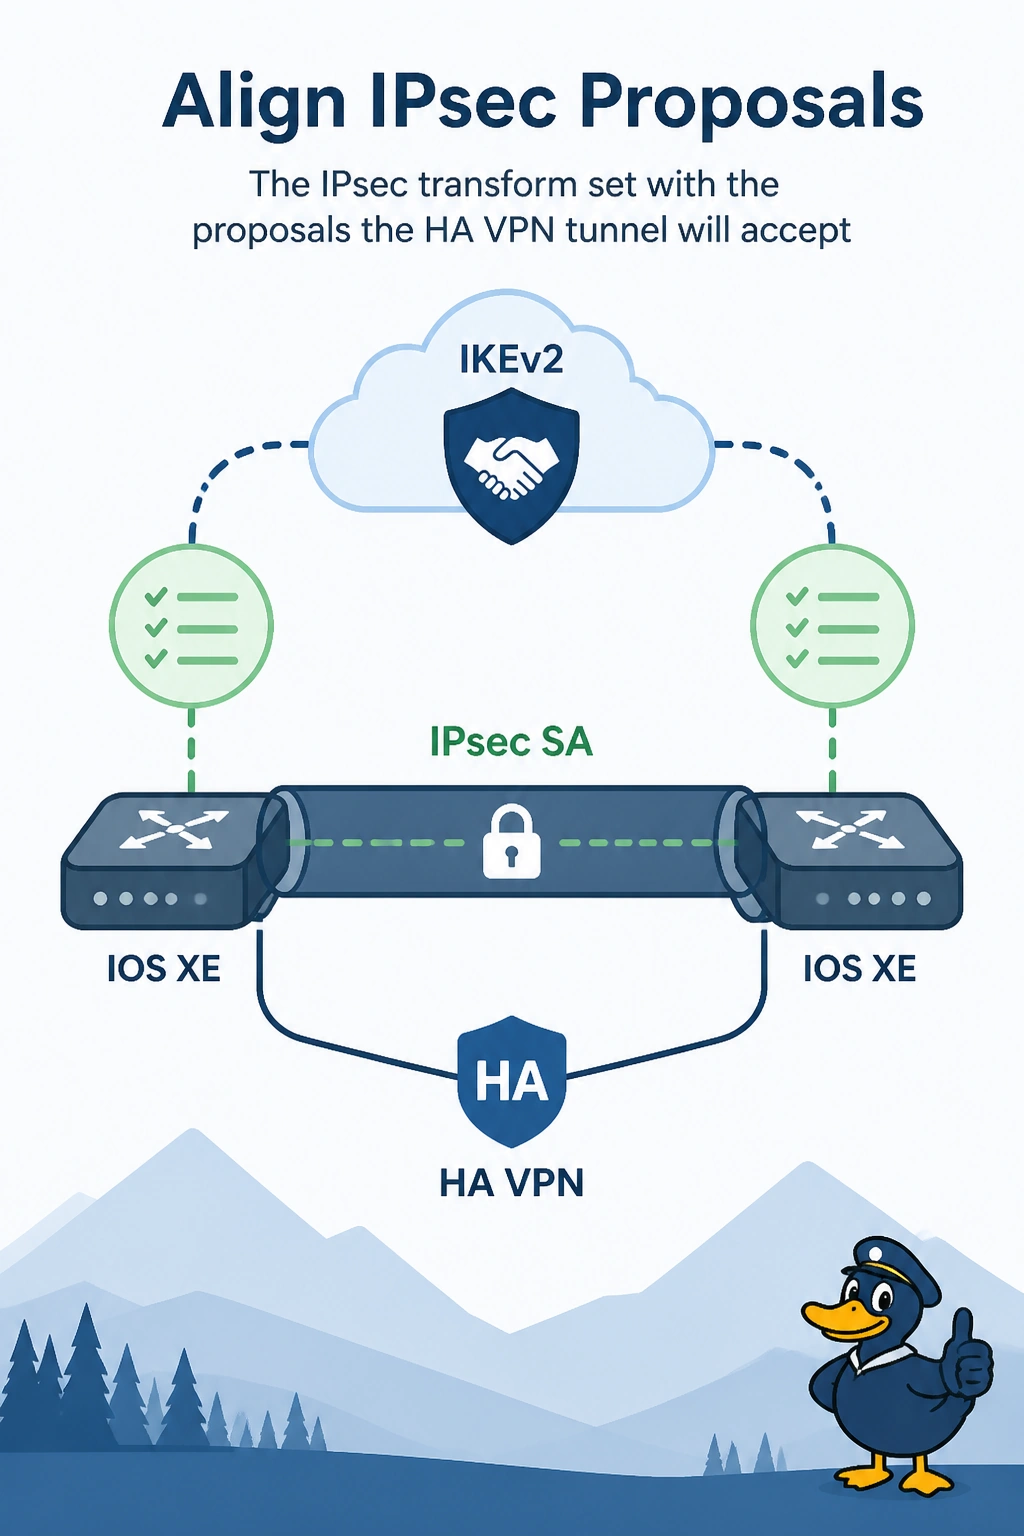
The outer handshake finished and the inner one offered a lock the gateway will not use. You align the IPsec transform set with a proposal the HA VPN tunnel accepts. IKE is already up, so this is not the BGP ASN and not an OSPF setting on Cloud Router.
Full Explanation
IKEv2 up means phase 1 succeeded. The IPsec SA is a separate negotiation. If the transform set is not one the HA VPN tunnel will accept, that SA never forms and no traffic passes. Change the router to a proposal the tunnel is configured to use. The BGP ASN is not part of the transform. BGP can start only after the SA exists. Cloud Router does not use an OSPF network type, and OSPF does not select an IPsec transform. This is a standalone IOS XE router. An SD-WAN BFD multiplier is not its transform set. Exam caveat: both HA VPN tunnels need a transform the gateway will accept. Fixing only the first tunnel leaves the second one down at the same step. Operational check: show crypto ipsec sa should come up after the transform matches, and the HA VPN page should show the tunnel established rather than only IKE.