
A clinic will not run BGP to an AWS virtual private gateway. The IPsec tunnel is up, but AWS never installs the clinic prefix. No static route for that prefix was entered on the VPN connection. What is missing?
Select an answer to reveal the explanation.
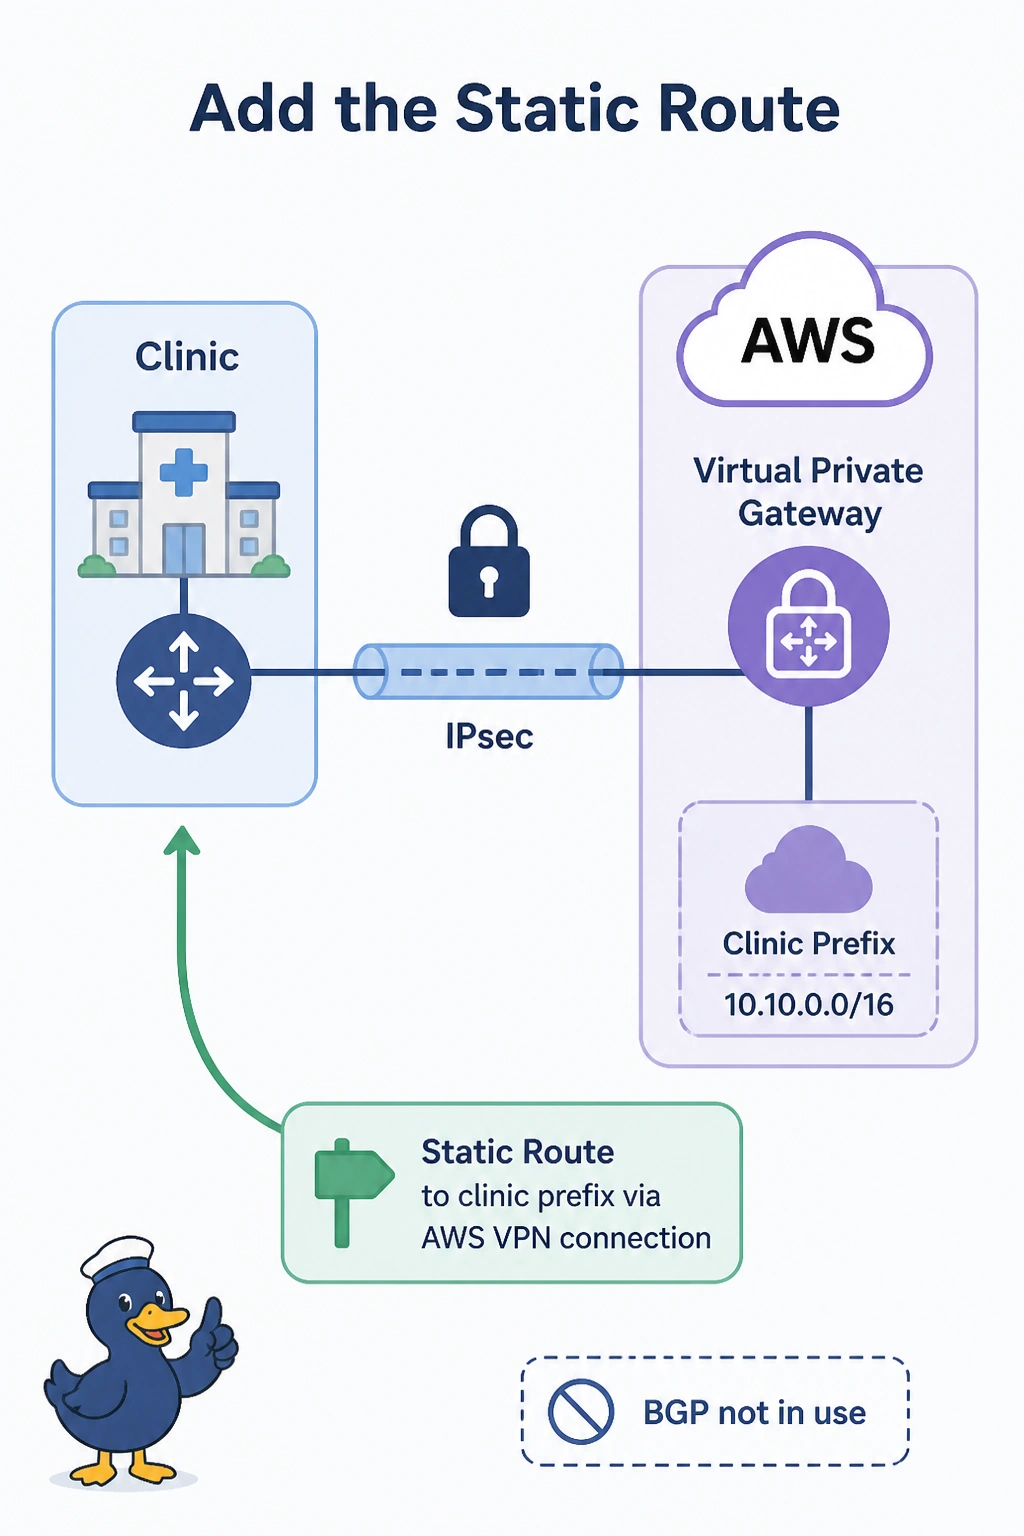
Short Explanation
If you refuse to speak BGP, you have to hand AWS the prefix on paper. You add a static route for the clinic prefix on the VPN connection, because the tunnel being up only means IPsec works. It does not invent a route AWS was never given.
Full Explanation
When a customer does not use BGP, AWS Site-to-Site VPN relies on the static routes associated with the VPN connection to learn customer prefixes and to decide what to send back through the tunnel. The clinic left that static route out, so AWS has no clinic prefix to install even though IPsec is up. OSPF redistribution on the virtual private gateway is not possible. That gateway does not run OSPF. The IKE lifetime does not gate static route installation. The SA is already up, and a rekey is not how static routes are entered. OMP is the SD-WAN overlay protocol. This is a standalone IOS XE VPN connection, so there is no OMP advertisement for AWS to read. Exam caveat: the matching static on the clinic router, pointing the VPC prefix at the tunnel, is still required in the other direction. One static on AWS does not fix a missing route on the router. Operational check: the VPN connection's static routes should list the clinic prefix, and the VPC route table should then show that prefix toward the virtual private gateway.