
A hospital IOS XE router will terminate internet IPsec to a new Google Cloud HA VPN gateway. Which configuration matches what HA VPN can actually peer with?
Select an answer to reveal the explanation.
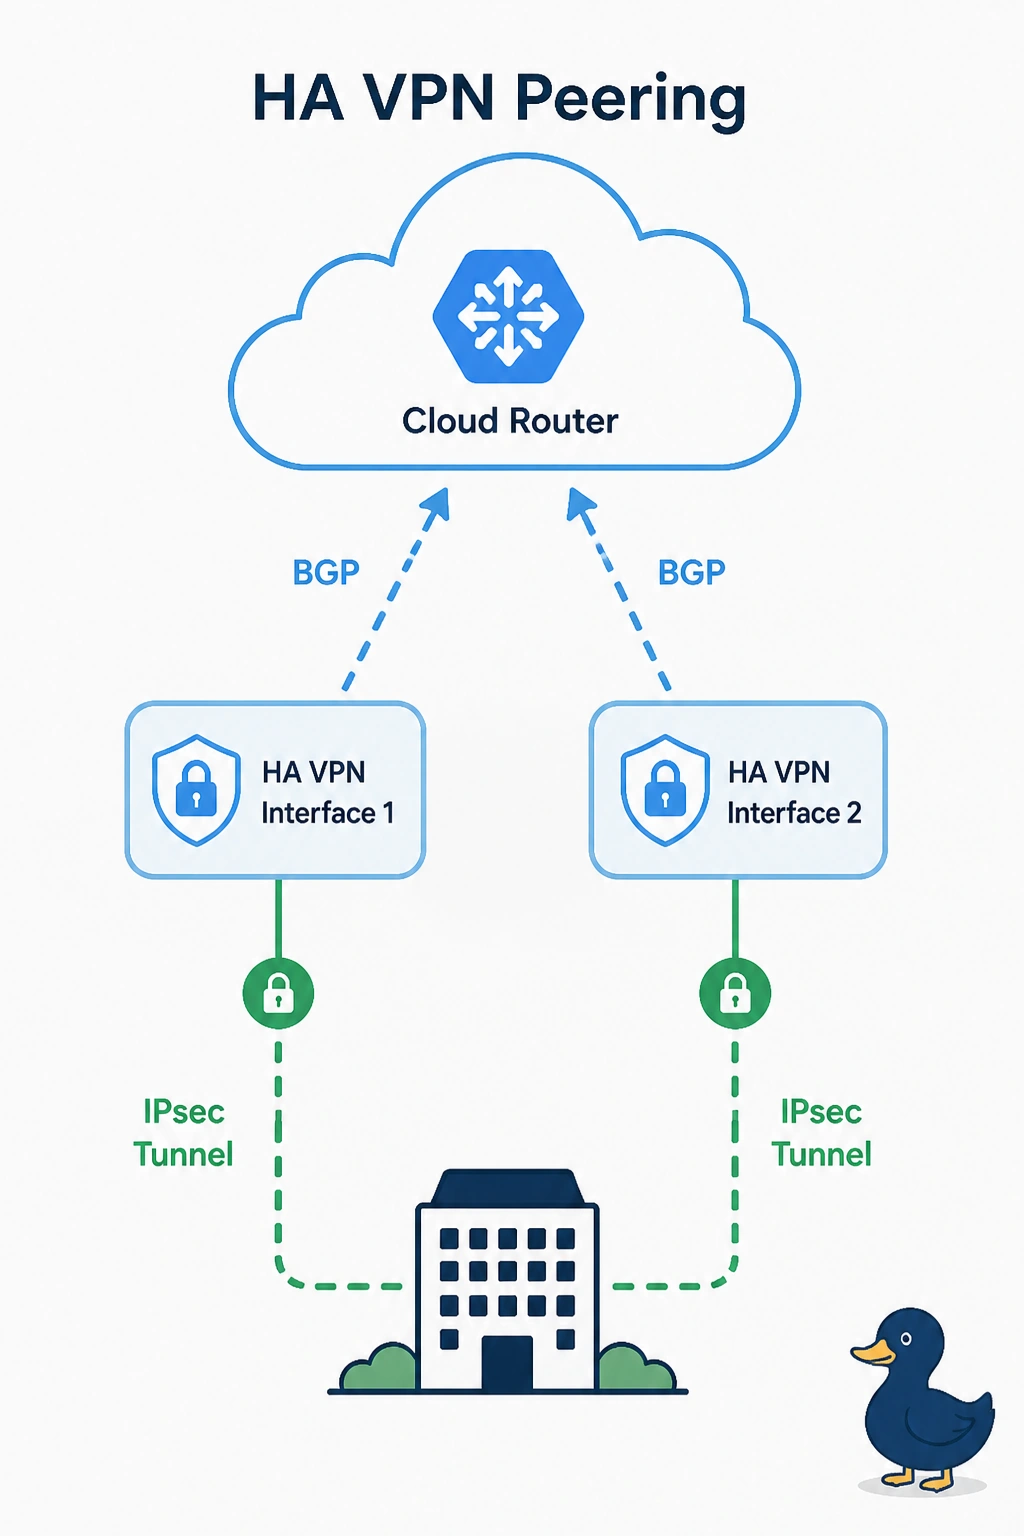
Short Explanation
HA VPN will not learn your routes from a static note or from OSPF. You build an IPsec tunnel to each HA VPN interface and peer BGP with Cloud Router. One Classic tunnel is a different gateway, and EIGRP is not on the menu.
Full Explanation
Google Cloud HA VPN supports dynamic routing only. The hospital router needs an IPsec tunnel to each of the two HA VPN interface addresses and a BGP session, via Cloud Router, for each tunnel it will use. That is the configuration the gateway will peer with. A single static route over Classic VPN talks to a different gateway type. Classic VPN can still use static routing, but it is not an HA VPN gateway and it does not use the two HA interfaces. Cloud Router does not terminate OSPF or a GRE tunnel for HA VPN. There is no OSPF adjacency to configure. EIGRP is not a Cloud VPN routing protocol. Leaving the second interface empty also fails the redundant HA VPN design even before the protocol mismatch. Exam caveat: both tunnels can stay up while route priorities make one preferred. That is active-passive forwarding with two live BGP sessions, which is still valid HA VPN. Operational check: show ip bgp summary on the hospital router should show the Cloud Router neighbors, and the Google console should show both HA VPN tunnels established.