
A stadium's Cisco IOS XE router in an AWS VPC has an up IPsec tunnel to the campus, but campus hosts still cannot reach VPC instances. Those instances use the VPC route table, which has no route for the campus prefix. What should be added?
Select an answer to reveal the explanation.
Short Explanation
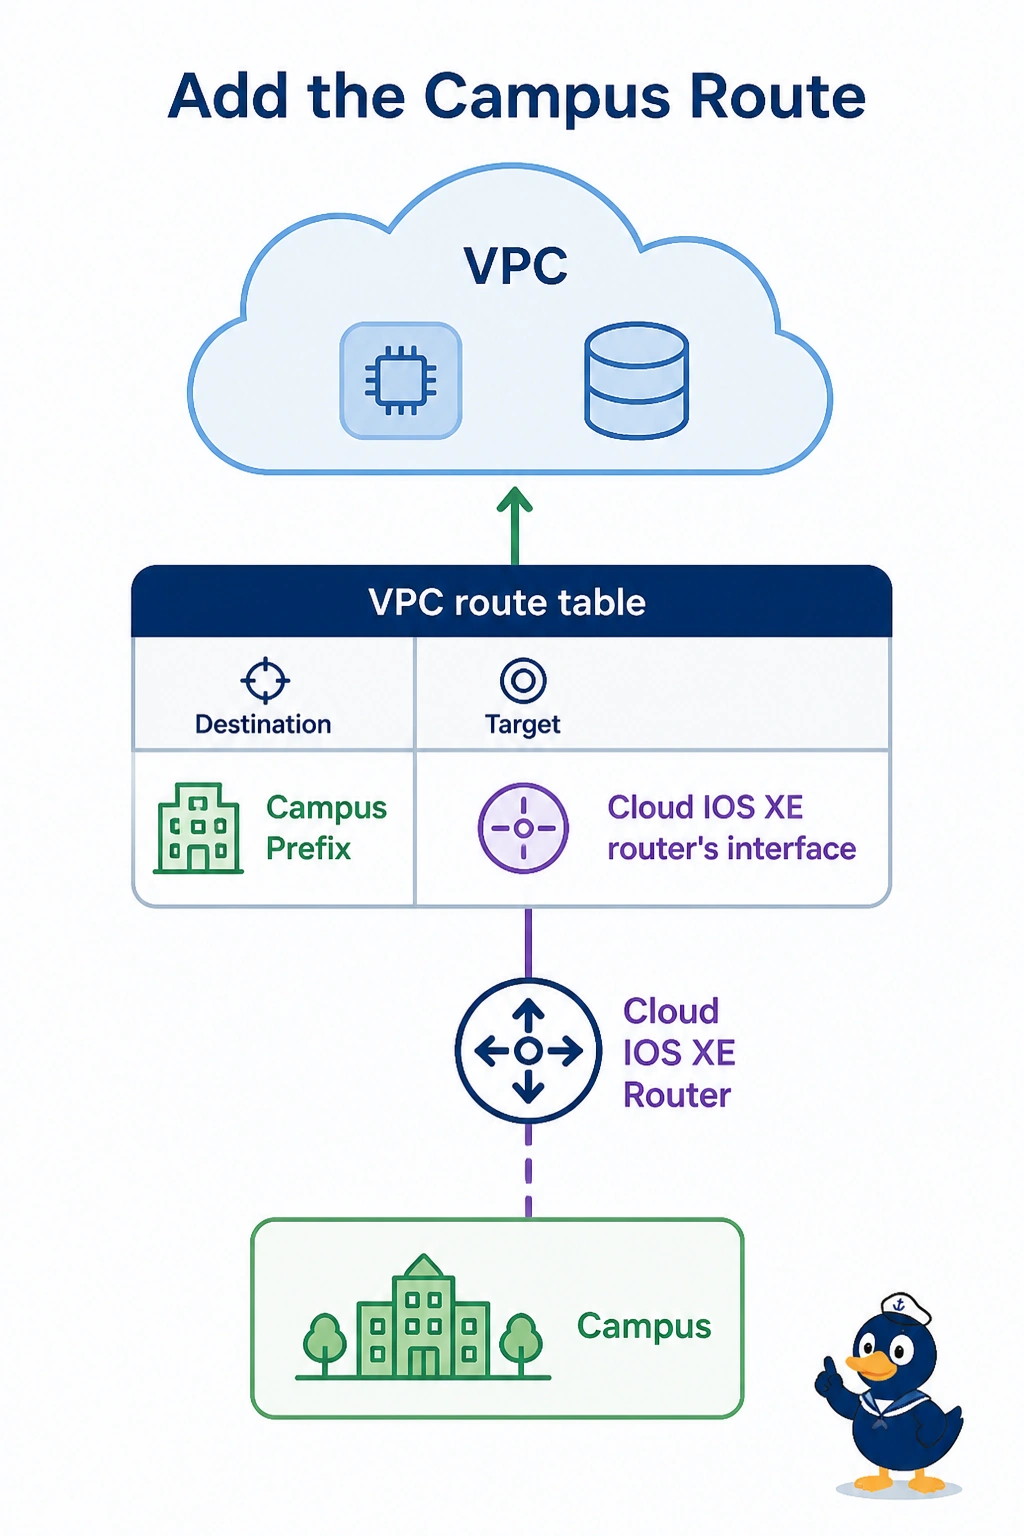
The tunnel being up only means the two routers can talk. The instances follow the VPC route table, and that table has no campus route, so they never hand return traffic to your cloud router. Point the campus prefix at that router's interface.
Full Explanation
A Cisco IOS XE router hosted in the VPC is just another instance to the VPC network. Instances send return traffic where the subnet route table points. With no route for the campus prefix, that traffic does not arrive on the cloud router's NIC, even though the IPsec SA to the campus is up. Add a route for the campus prefix targeted at that router's interface. An OSPF process on the virtual private gateway does not apply. This tunnel terminates on the IOS XE router, not on the native gateway, and the native gateway does not run OSPF. A longer IKE lifetime does not install a VPC route. The SA is already up, so phase 1 is not the outage. A public virtual interface is a Direct Connect construct for public AWS services. VPC instance forwarding is controlled by the subnet route table, not by that virtual interface. Exam caveat: the cloud router's own security group must also allow the campus traffic, and the router must have a route back to the instances. The route table is the piece this symptom isolates. Operational check: the subnet route table should list the campus prefix toward the IOS XE network interface, and a trace from an instance should hit that interface before it enters the tunnel.