
A logistics IOS XE edge must send guest internet traffic to a secure internet gateway for inspection, while a separate tunnel still reaches an AWS VPC. How should the guest traffic be sent?
Select an answer to reveal the explanation.
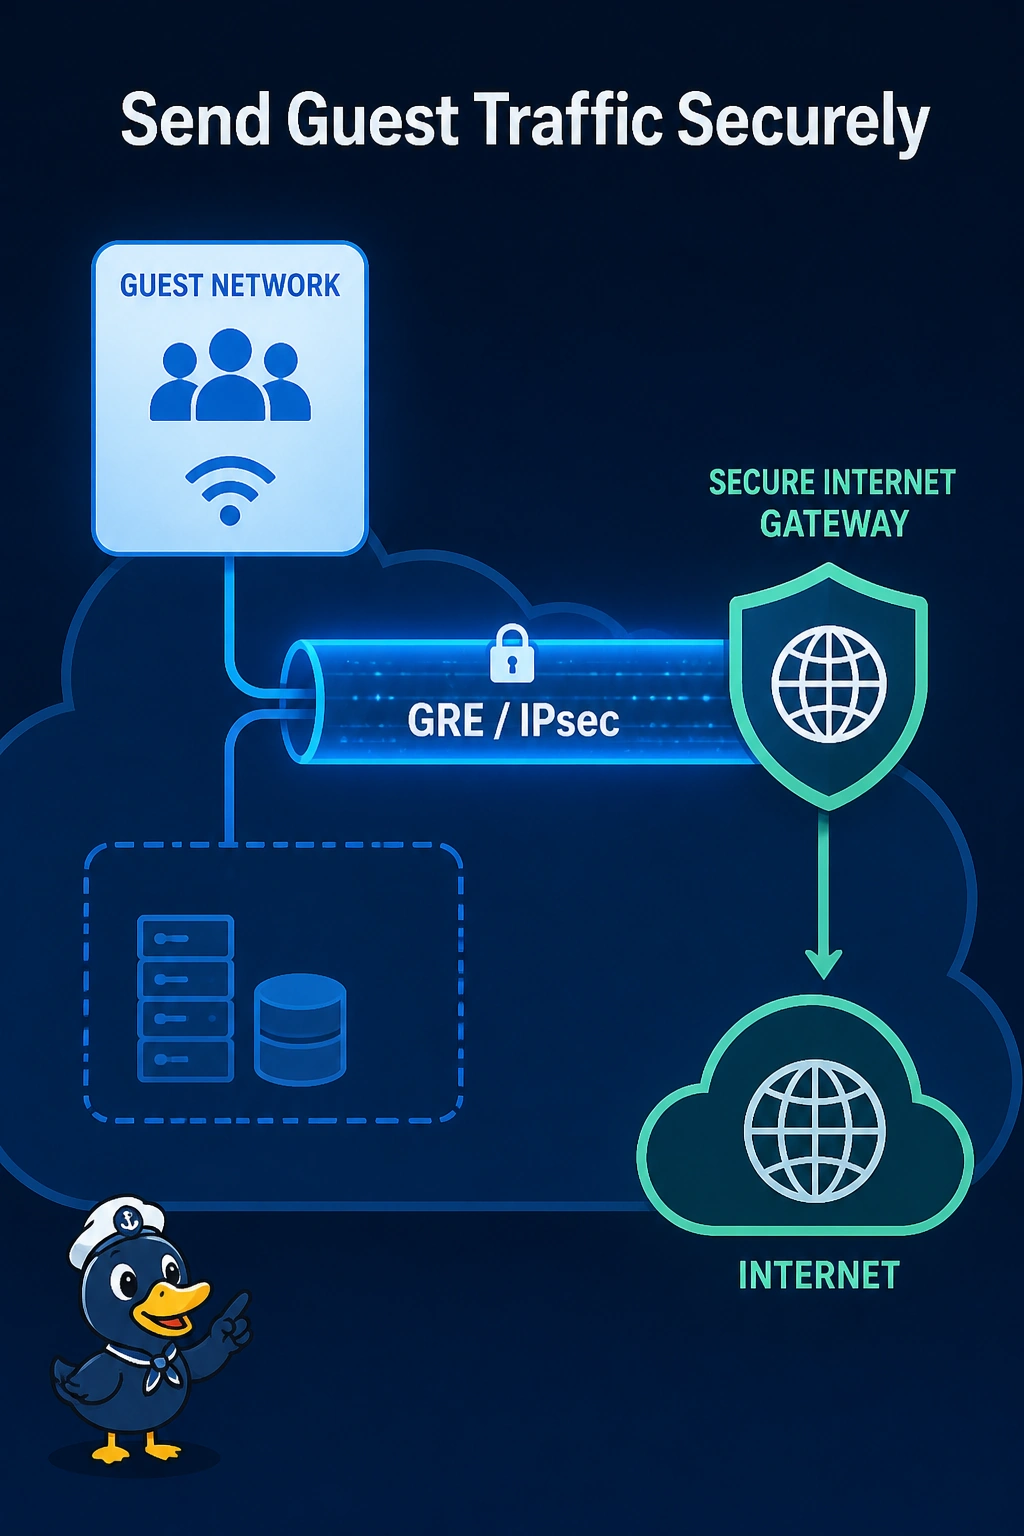
Short Explanation
Guest traffic needs the inspection dock, not the warehouse door. You point it at the GRE or IPsec tunnel that ends on the secure internet gateway. The AWS tunnel delivers the VPC, and it does not inspect the guest internet session.
Full Explanation
A secure internet gateway is the cloud security stack in objective 3.1. Cisco IOS XE reaches it with a GRE tunnel or an IPsec tunnel, depending on what that gateway expects, and a route or policy sends the guest prefix there. That path is separate from the tunnel that terminates on an AWS virtual private gateway. The VPC tunnel decrypts into the VPC. It does not apply the secure internet gateway's inspection policy to guest web traffic. Sending guest traffic in the clear on the WAN skips the gateway the design required. An AWS security group filters traffic at an instance or subnet inside AWS. It never sees a guest session that left toward the public internet from the logistics edge. An OSPF adjacency with the secure internet gateway over the campus LAN is not how those gateways are attached. They sit across the internet, reached by the tunnel. Exam caveat: build the SIG tunnel with the encapsulation that gateway documents, then route only the intended guest ranges at it so VPC traffic stays on the AWS tunnel. Operational check: a guest trace should show the SIG tunnel as the egress, and the SIG portal should show the tunnel up and the session inspected.