
A retailer redistributes BGP routes from an AWS virtual private gateway into OSPF, and OSPF routes back into BGP, on the same IOS XE router. No tags or prefix filters are applied. What failure should they expect?
Select an answer to reveal the explanation.
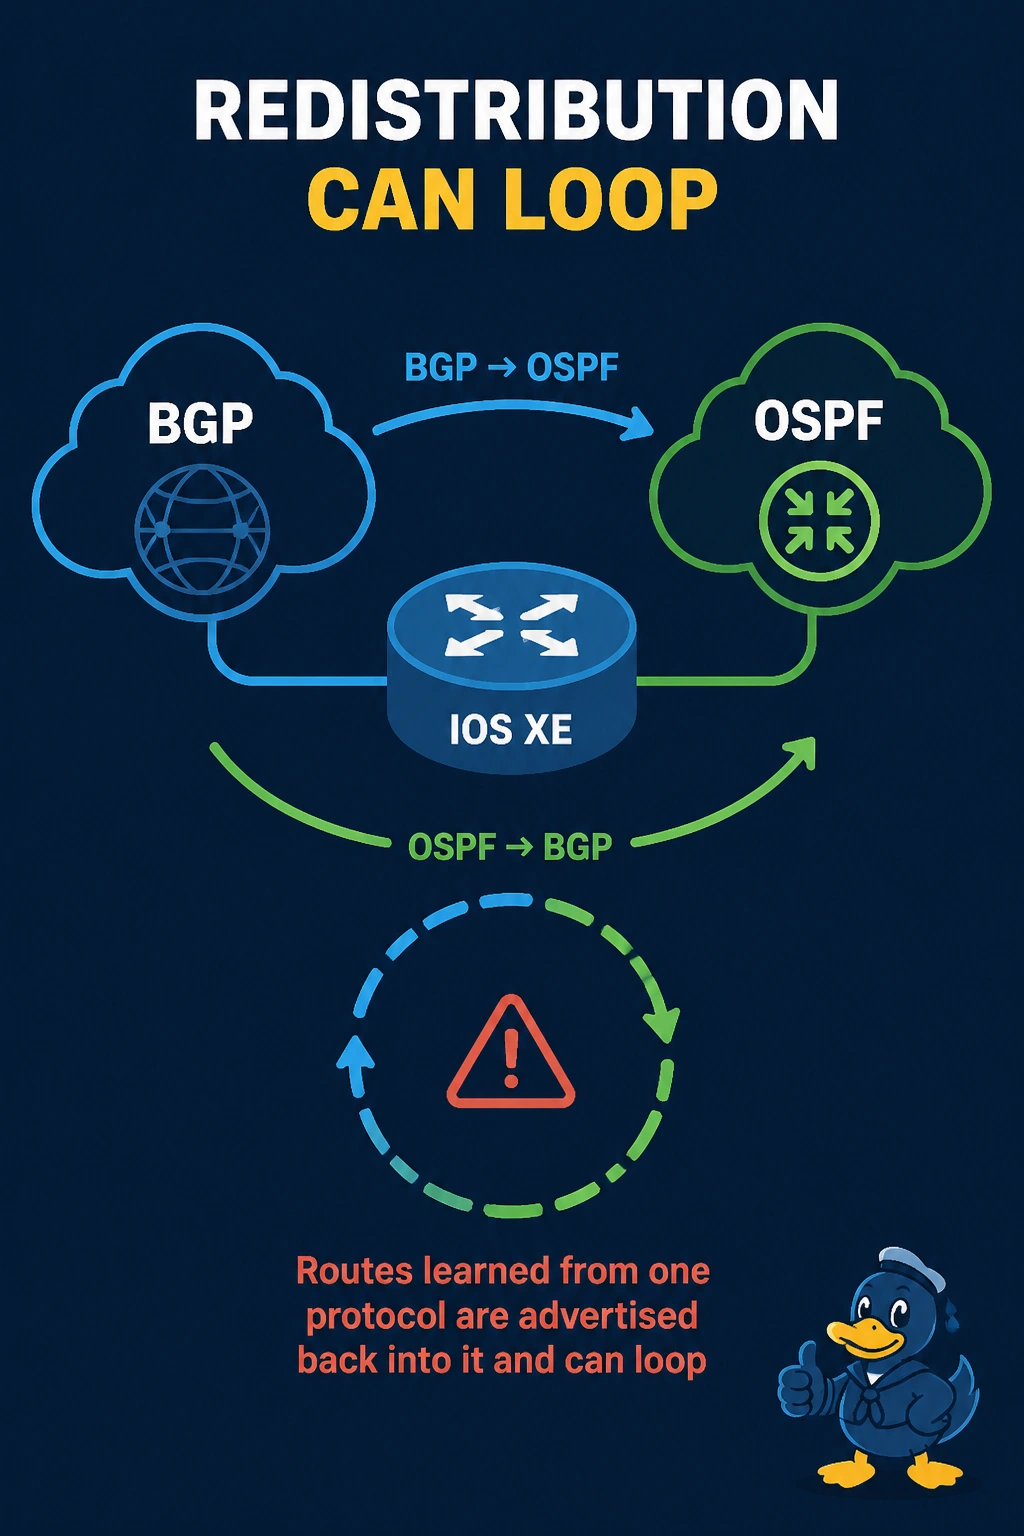
Short Explanation
If you pour water from one bucket into the other and back with no mark, you cannot tell what you already poured. Tag the routes, or filter them, when you redistribute both ways. Otherwise a prefix you learned from BGP gets handed back to BGP.
Full Explanation
Mutual redistribution on one Cisco IOS XE router will take a route learned from BGP, inject it into OSPF, and then inject it back into BGP if nothing filters it. The same happens in the other direction. Without a route tag or a prefix filter, the cloud prefixes and the campus prefixes can loop, and the router can prefer a path that points back at itself. AWS does not need to run OSPF for this failure. The OSPF adjacency is between IOS XE devices. The virtual private gateway only has the BGP session. Redistribution does not change eBGP's administrative distance to 110. OSPF uses 110. eBGP still uses 20 when it is the route installed from BGP. The IPsec tunnel does not reset because a prefix was redistributed. The SA stays up while the routing table thrashes. Exam caveat: a one-way redistribution can be safe. The hazard is the return path with no tag and no filter. Operational check: tag BGP routes as they enter OSPF, deny that tag when OSPF is redistributed into BGP, and confirm show ip bgp no longer lists the router's own cloud prefixes as learned from the OSPF side.