
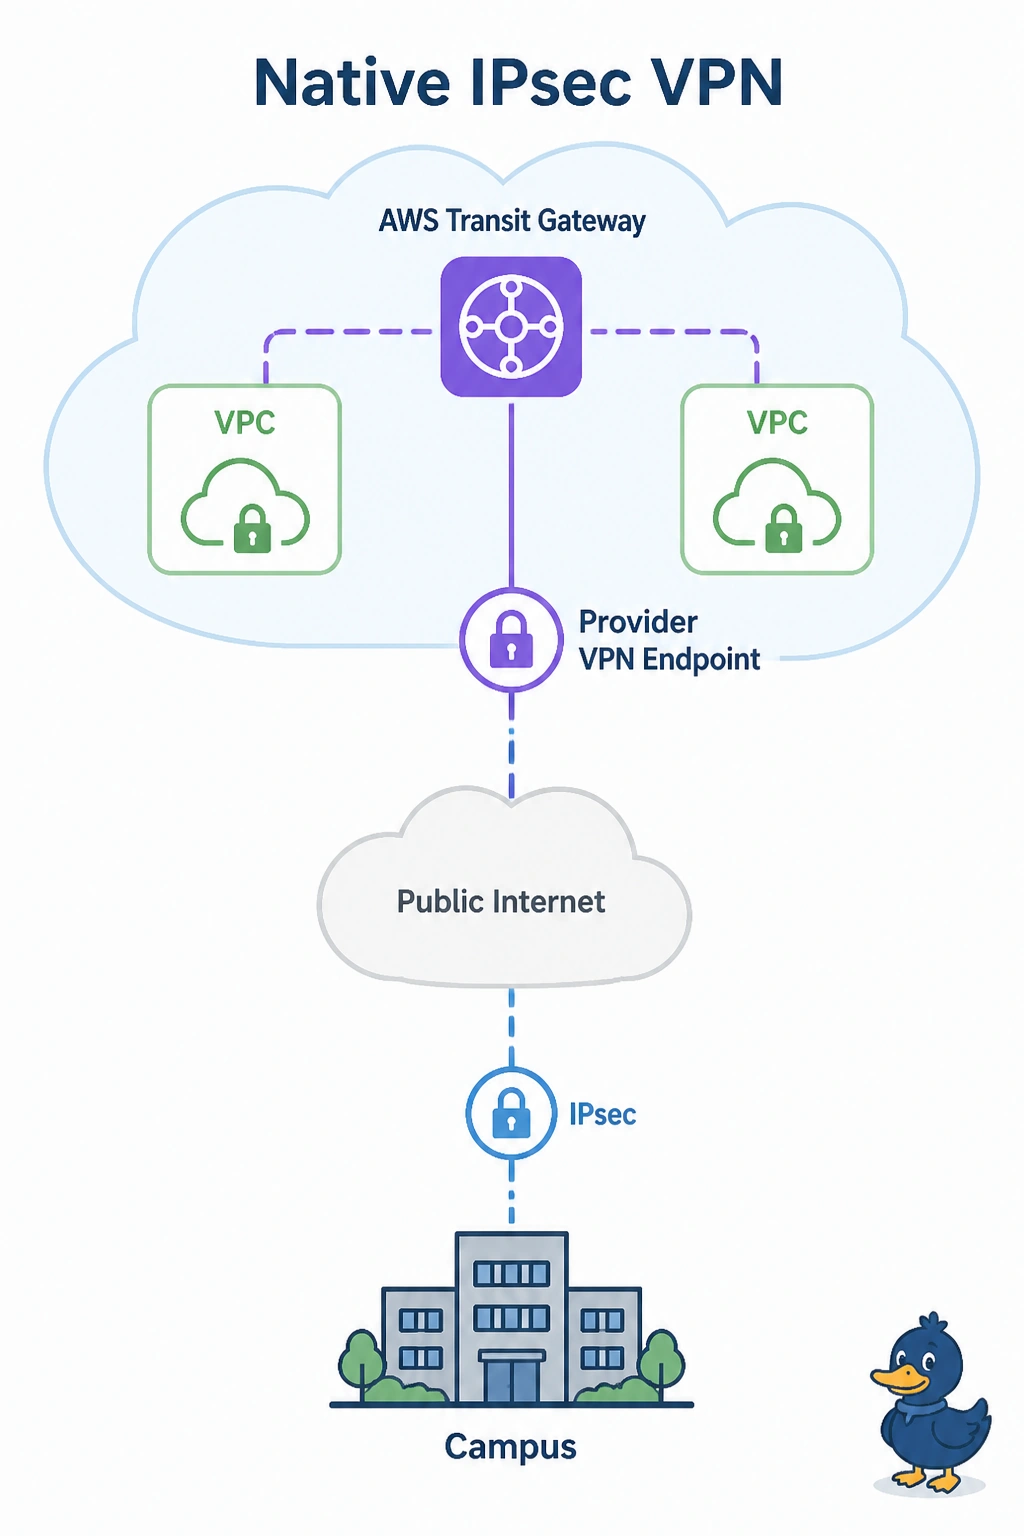
A shipper attaches several VPCs to one AWS transit gateway and builds a VPN attachment to the campus over the public internet. There is no Catalyst SD-WAN controller. Which model is this?
Select an answer to reveal the explanation.
Short Explanation
Several VPCs on one transit gateway do not change the road you used to get there. You built a VPN over the public internet to AWS, with no SD-WAN controllers, so this is native IPsec. Direct Connect and a cage cross-connect were not ordered.
Full Explanation
A transit gateway VPN attachment is still the AWS Site-to-Site VPN service. The underlay is the public internet, the endpoint belongs to AWS, and the payload is encrypted. That is native IPsec even when several VPCs share the transit gateway. Direct Connect is a private port into AWS, and this design does not use one. Catalyst SD-WAN internet connectivity needs the overlay controllers and OMP. The shipper has neither. A colocation cross-connect is a physical circuit from a customer cage, which was not ordered. Exam caveat: moving this same transit gateway onto a Direct Connect transit VIF later would change the model. The VPN attachment by itself does not become private. Operational check: the campus peer should be the transit gateway VPN outside address on the internet, and the transit gateway route table should show the campus prefixes from that attachment.