
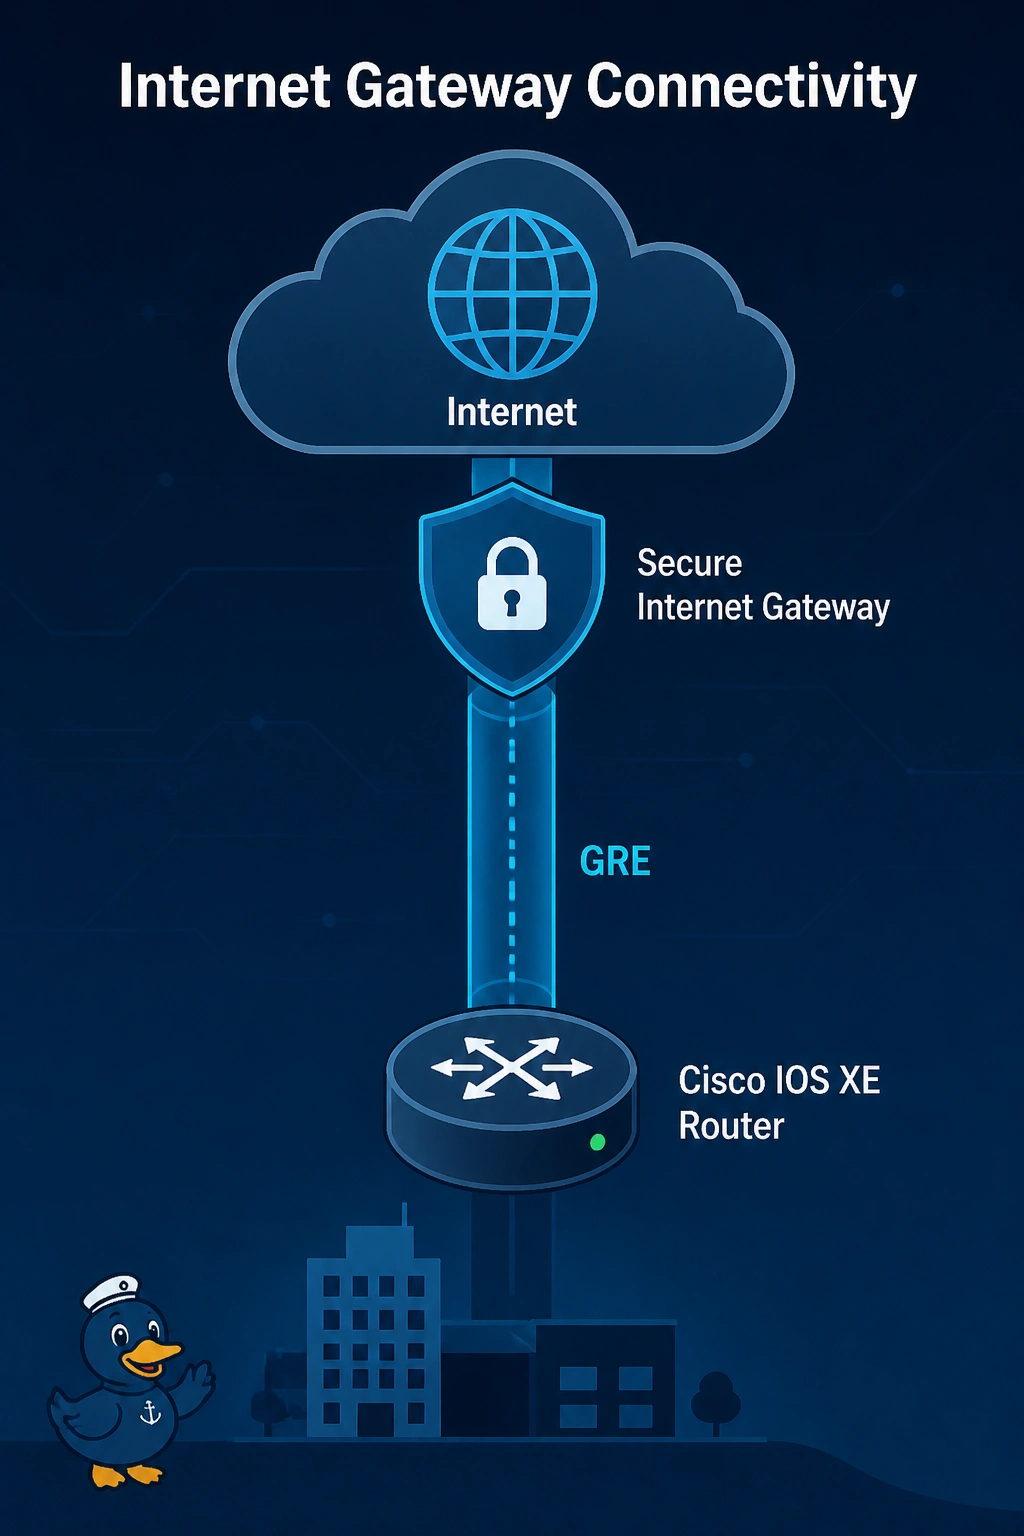
A warehouse uses a standalone Cisco IOS XE router to send internet traffic through a GRE tunnel to a secure internet gateway. There is no SD-WAN controller. Which model is this?
Select an answer to reveal the explanation.
Short Explanation
A tunnel to a cloud security stack is not an SD-WAN overlay just because the far end lives in the cloud. You have a standalone router and a GRE tunnel over the internet, with no controller. That is internet connectivity to a secure internet gateway, not a cross-connect and not MPLS.
Full Explanation
Objective 1.1 includes internet paths that terminate on a secure internet gateway, not only paths that terminate on a provider VPN gateway. This warehouse router is standalone IOS XE, the underlay is the internet, and the tunnel is GRE to the gateway. There is no SD-WAN controller, so it is not Catalyst SD-WAN cloud connectivity. Calling it SD-WAN because the gateway is a cloud service confuses the far end with the overlay. A colocation cross-connect would be a physical cable in a shared building. This path is a GRE tunnel. An MPLS handoff would keep the traffic off the internet. The stem sends it through the internet to the gateway. Exam caveat: the same gateway can also be reached by Catalyst SD-WAN's SIG feature. The model follows how you attach, and this attachment is a standalone router. Operational check: the warehouse router should show a GRE tunnel to the gateway's published address and should not show SD-WAN control connections.