
A boutique hotel hosts its guest Wi-Fi sign-in page on its own server and points an MX at it as an external captive portal. Meraki redirects each guest browser there before access is allowed. Which step in the external captive portal flow authorizes the guest on the network?
Select an answer to reveal the explanation.
Short Explanation
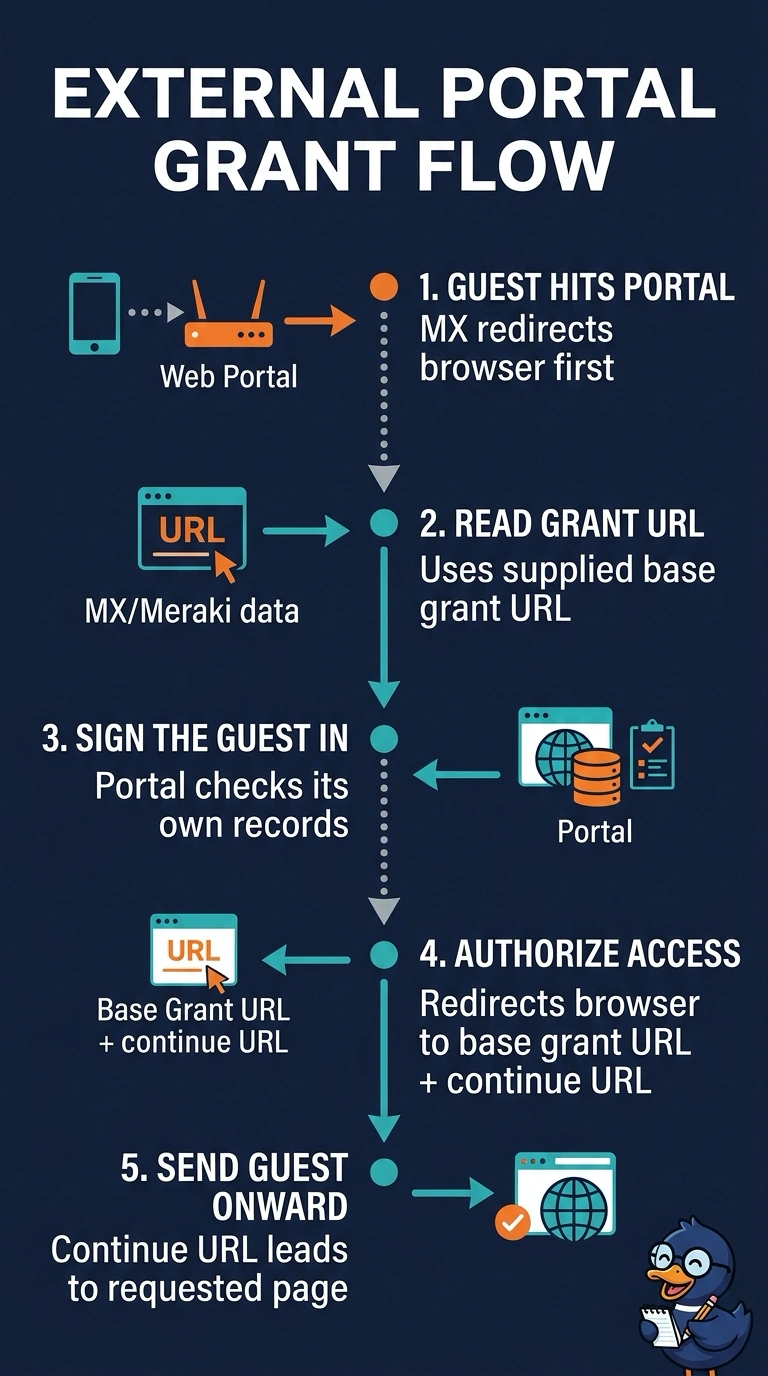
After you sign in, the portal redirects your browser to Meraki’s base grant URL, including the continue URL. That redirect is the green light that authorizes you on the network; the continue URL then takes you to your next page.
Full Explanation
The external captive portal flow uses a browser redirect. The MX sends the guest to the hotel's portal with parameters that include a base grant URL and a continue URL. After the portal completes its own sign-in, it redirects the browser to the supplied base grant URL to authorize access; the continue URL is used to send the guest onward. Registering a device through the dashboard REST API is a different operation and does not authorize this captive portal session. Returning the guest straight to the continue URL does not grant access, and a hosted Meraki splash page is not the hotel's external portal. Follow the current Meraki documentation for the required redirect parameters and any optional parameters.