
A junior engineer is writing a small Python tool that logs in to SD-WAN Manager with POST /j_security_check and then runs six read-only queries in a loop. The first query succeeds while the login response is still in hand, but every later query fails once those headers are discarded. Which authentication approach keeps the Manager API session valid for the whole loop?
Select an answer to reveal the explanation.
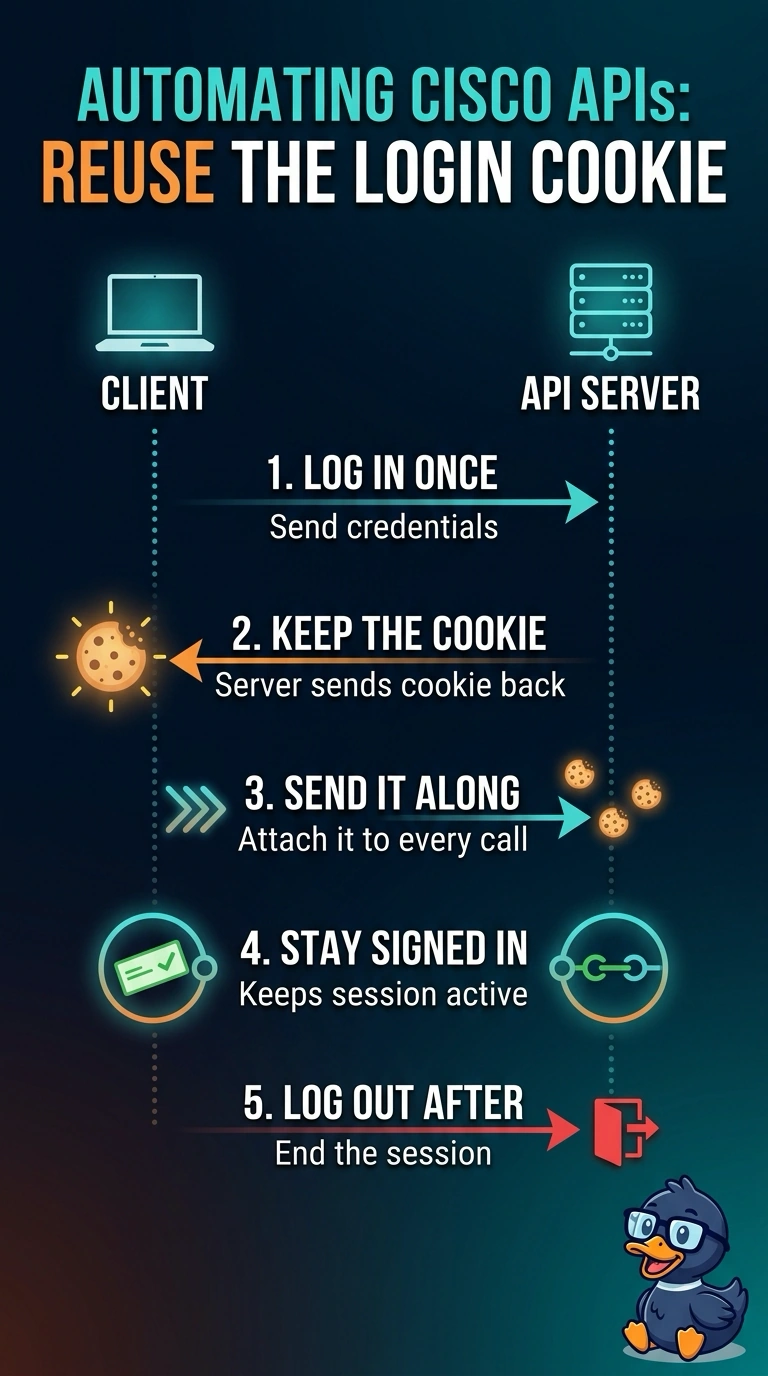
Short Explanation
Manager returns a session cookie in the login response, and you carry it on every later call, like keeping an entry wristband on all day. Basic auth and identity-provider tokens are not substitutes for the Manager session cookie. Lose the cookie and the session is no longer identified.
Full Explanation
The login response provides a session cookie, which Manager uses to identify the authenticated session. Every follow-up dataservice call must carry that cookie in its Cookie header, or the server sees an unauthenticated request and rejects it. HTTP Basic authentication does not replace the Manager-issued session, and an OAuth bearer token from a separate identity provider is not a substitute for the authentication method configured for Manager. Sending the cookie just on the first call fails because later requests arrive without the session identifier. Authentication details can vary by Manager release; follow the documented method for your release. State-changing requests may also require an XSRF token, but these queries are read-only. Practical check: capture the Set-Cookie value once and replay it on the next request.