
A power utility with 80 WAN Edges must centralize logins for audits: network admins need role-based GUI access to the management platform with an external server, and field techs need external logins to routers with local fallback during WAN outages. Which AAA design covers external AAA for the Manager and for WAN Edges?
Select an answer to reveal the explanation.
Short Explanation
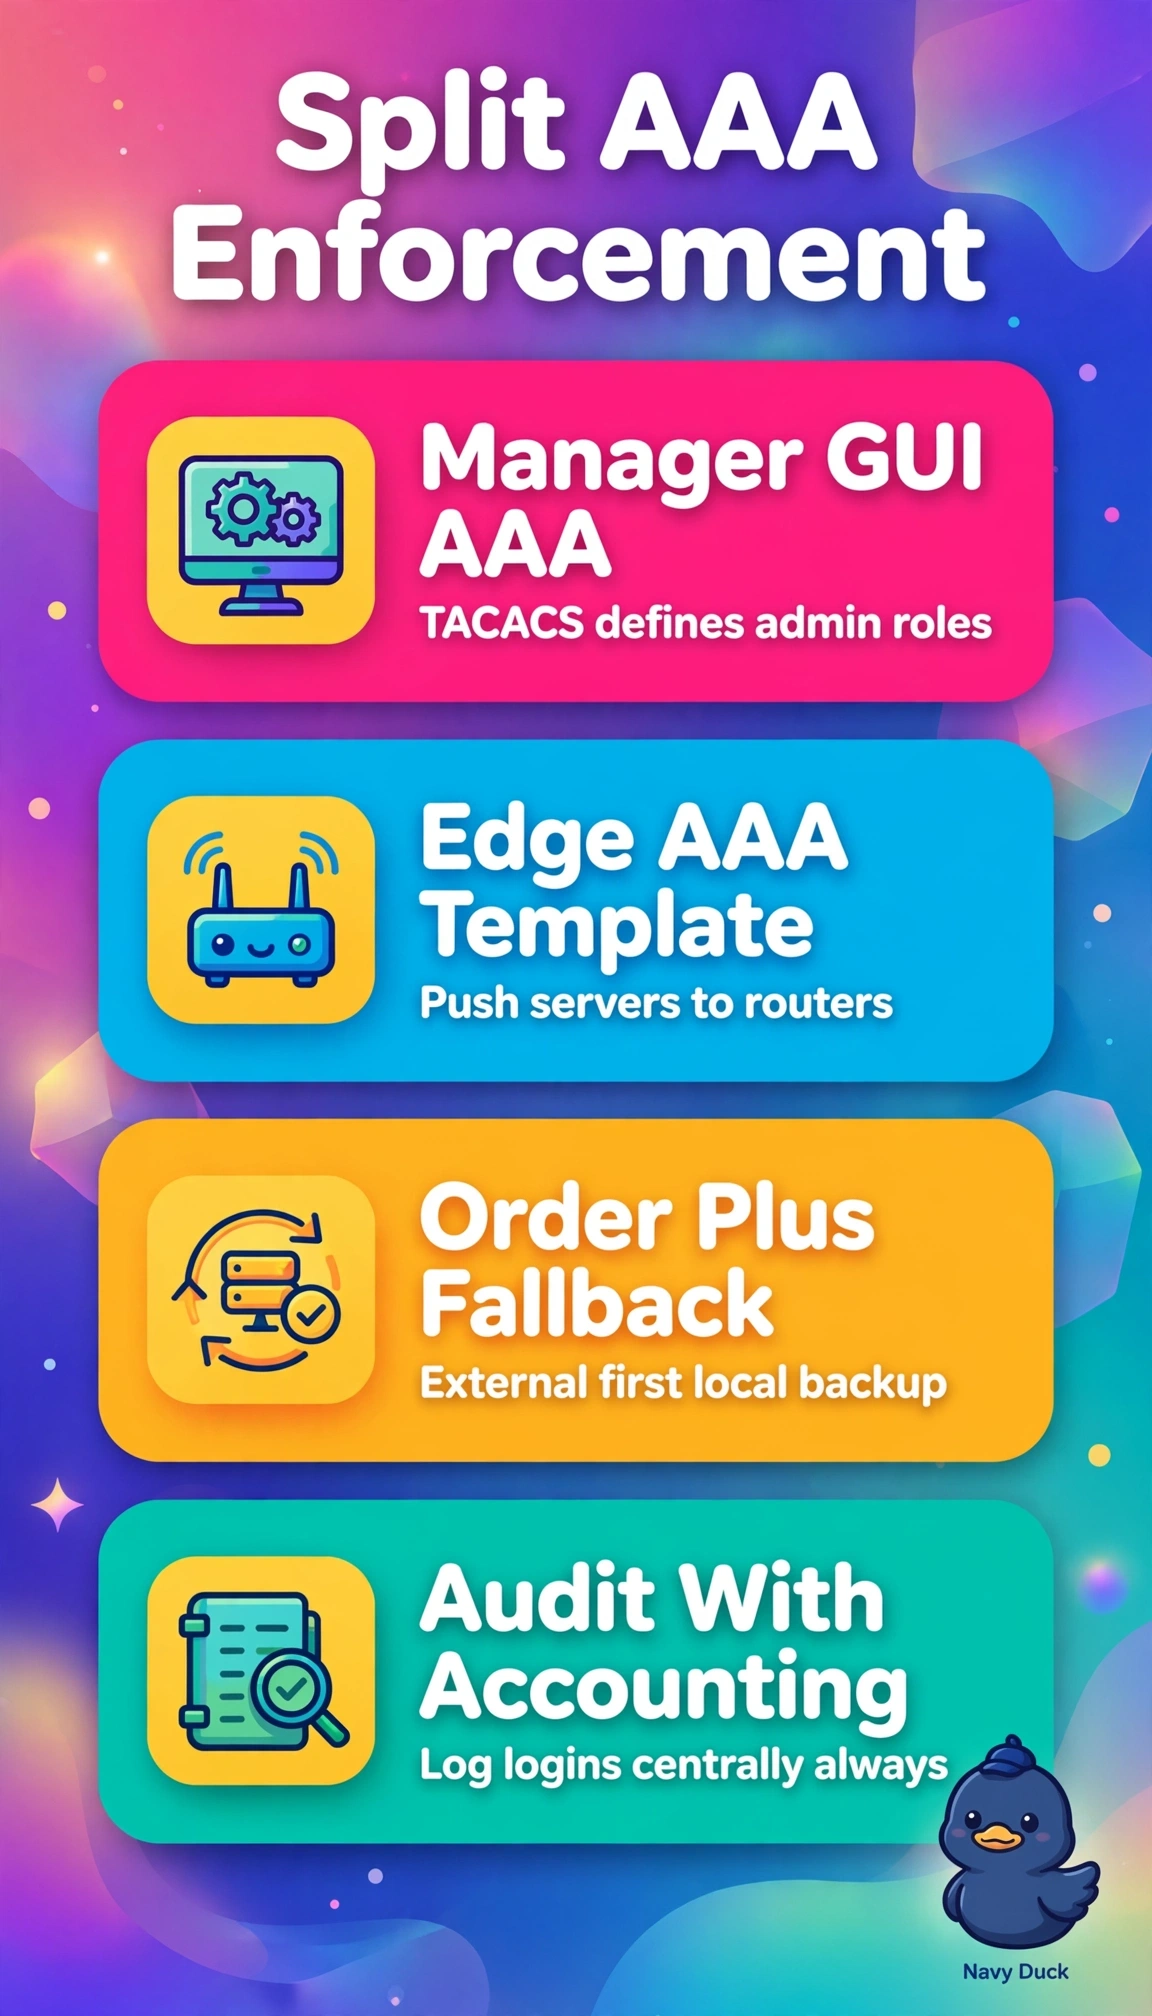
You're covering both front doors, not just one. Central TACACS+ with roles guards your management dashboard, while a pushed AAA template guards every router, with local accounts as your spare-key backup. VPN, SNMP, and syslog pieces handle other jobs entirely.
Full Explanation
The correct design succeeds because it addresses both planes with the proper mechanisms: TACACS+ on SD-WAN Manager provides centralized authentication plus granular authorization through groups and roles for GUI audit compliance, while an AAA feature template distributes TACACS+ server definitions and ordered authentication to all 80 WAN Edges at scale with local fallback preserving field access during outages. The default-privilege design fails on authorization concept because authentication alone with a shared default profile centralizes logins but cannot enforce least-privilege GUI roles and audit differentiation required for network admins. The controller-based design fails on architecture because Controllers handle control-plane peering and have no GUI user-role store, so defining groups and roles there leaves Manager GUI logins uncentralized despite correct Edge configuration. The external-authentication-only Edge design fails on resiliency because strict reliance on reachable TACACS+ without a local fallback order denies field tech logins precisely when WAN transport is down, violating the outage requirement while satisfying centralization. As an exam caveat, distinguish management-plane AAA configured on Manager from device AAA pushed via feature templates and remember TACACS+ rather than RADIUS enables command and GUI role authorization. As a practical check, verify Manager accounting shows per-admin GUI logins, confirm template attachment across all Edges, then simulate isolation to confirm fallback to local credentials and review logs after restoration.