
A university with 60 helpdesk staff needs role-based Manager access, seamless login for faculty using campus identity, and full command accounting for network changes with existing Cisco ISE. Auditors require centralized credentials, MFA-capable SSO, and per-command logs. Which external authentication combination on SD-WAN Manager satisfies these monitoring and access needs?
Select an answer to reveal the explanation.
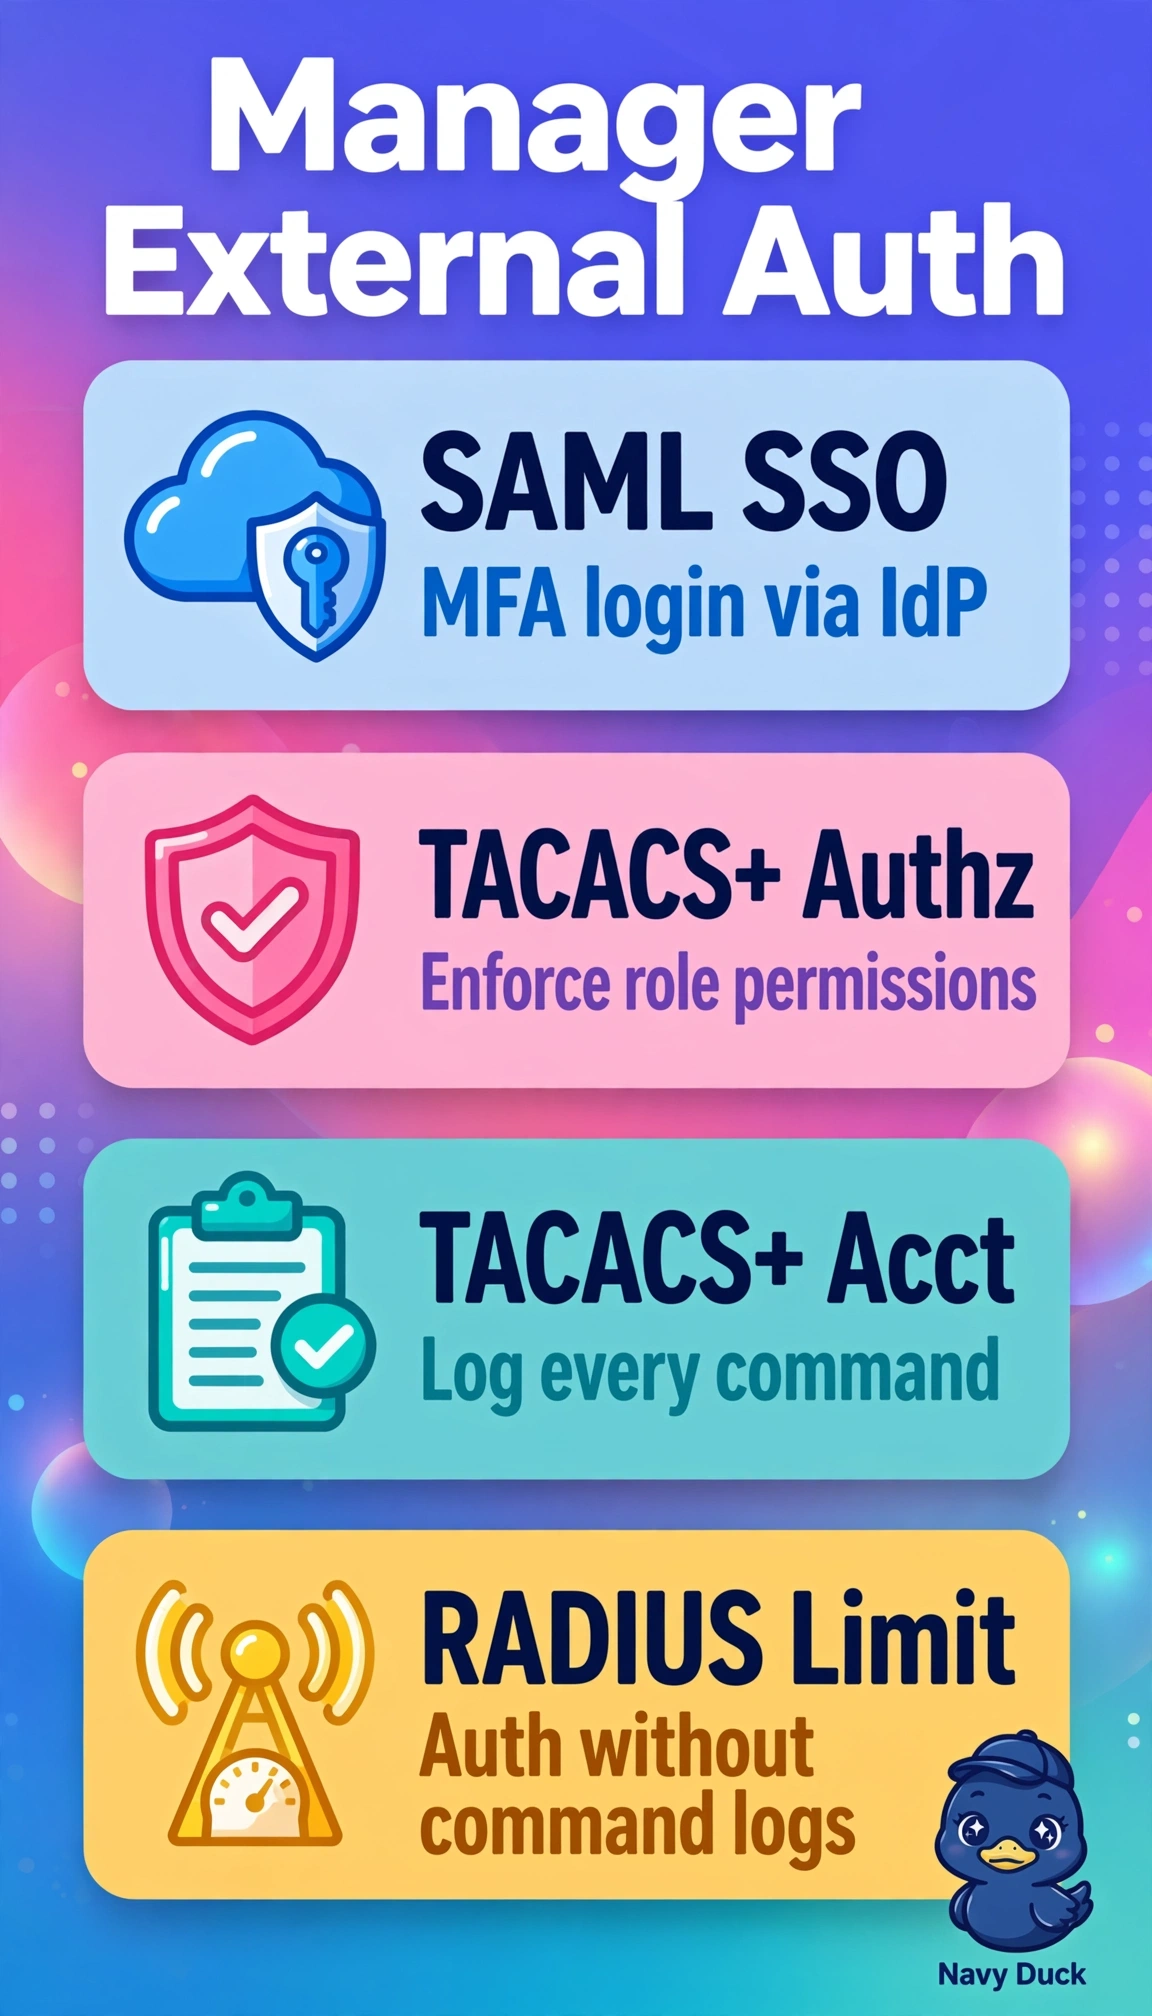
Short Explanation
You split login convenience from change control perfectly. Combine TACACS+ accounting with SAML SSO and both auditors and users stay happy.
Full Explanation
Manager external authentication separates concerns: SAML SSO offloads interactive GUI login to the campus identity provider, enabling MFA and centralized deprovisioning, while TACACS+ with the existing ISE provides centralized credentials, role-based authorization and per-command accounting that RADIUS and SAML cannot supply at command granularity, ideal for audit trails. RADIUS-only with local authorization fails because RADIUS can authenticate users but lacks TACACS+ style command authorization and accounting, and it does not provide IdP-based SSO. SAML-only fails by concept because SAML carries authentication assertions, not command authorization or accounting, so change attribution would be incomplete. Local accounts with SNMP polling fails because SNMP monitors metrics rather than authenticating users or logging commands, leaving centralized credential and MFA requirements unmet. Exam caveat is to match RADIUS to authentication, TACACS+ to authorization plus accounting, and SAML to SSO, and practical check is to test SSO login, execute config commands, then verify the TACACS+ accounting logs show user and command (SD-WAN Manager formerly vManage).