
A university uses TrustSec to group students, faculty and IoT cameras and needs those group tags preserved across an SD-WAN fabric with mixed MPLS and internet for policy at the data center. Inline tagging on all links is unreliable. Which Cisco SD-WAN security feature should the engineer describe to carry group context end to end?
Select an answer to reveal the explanation.
Short Explanation
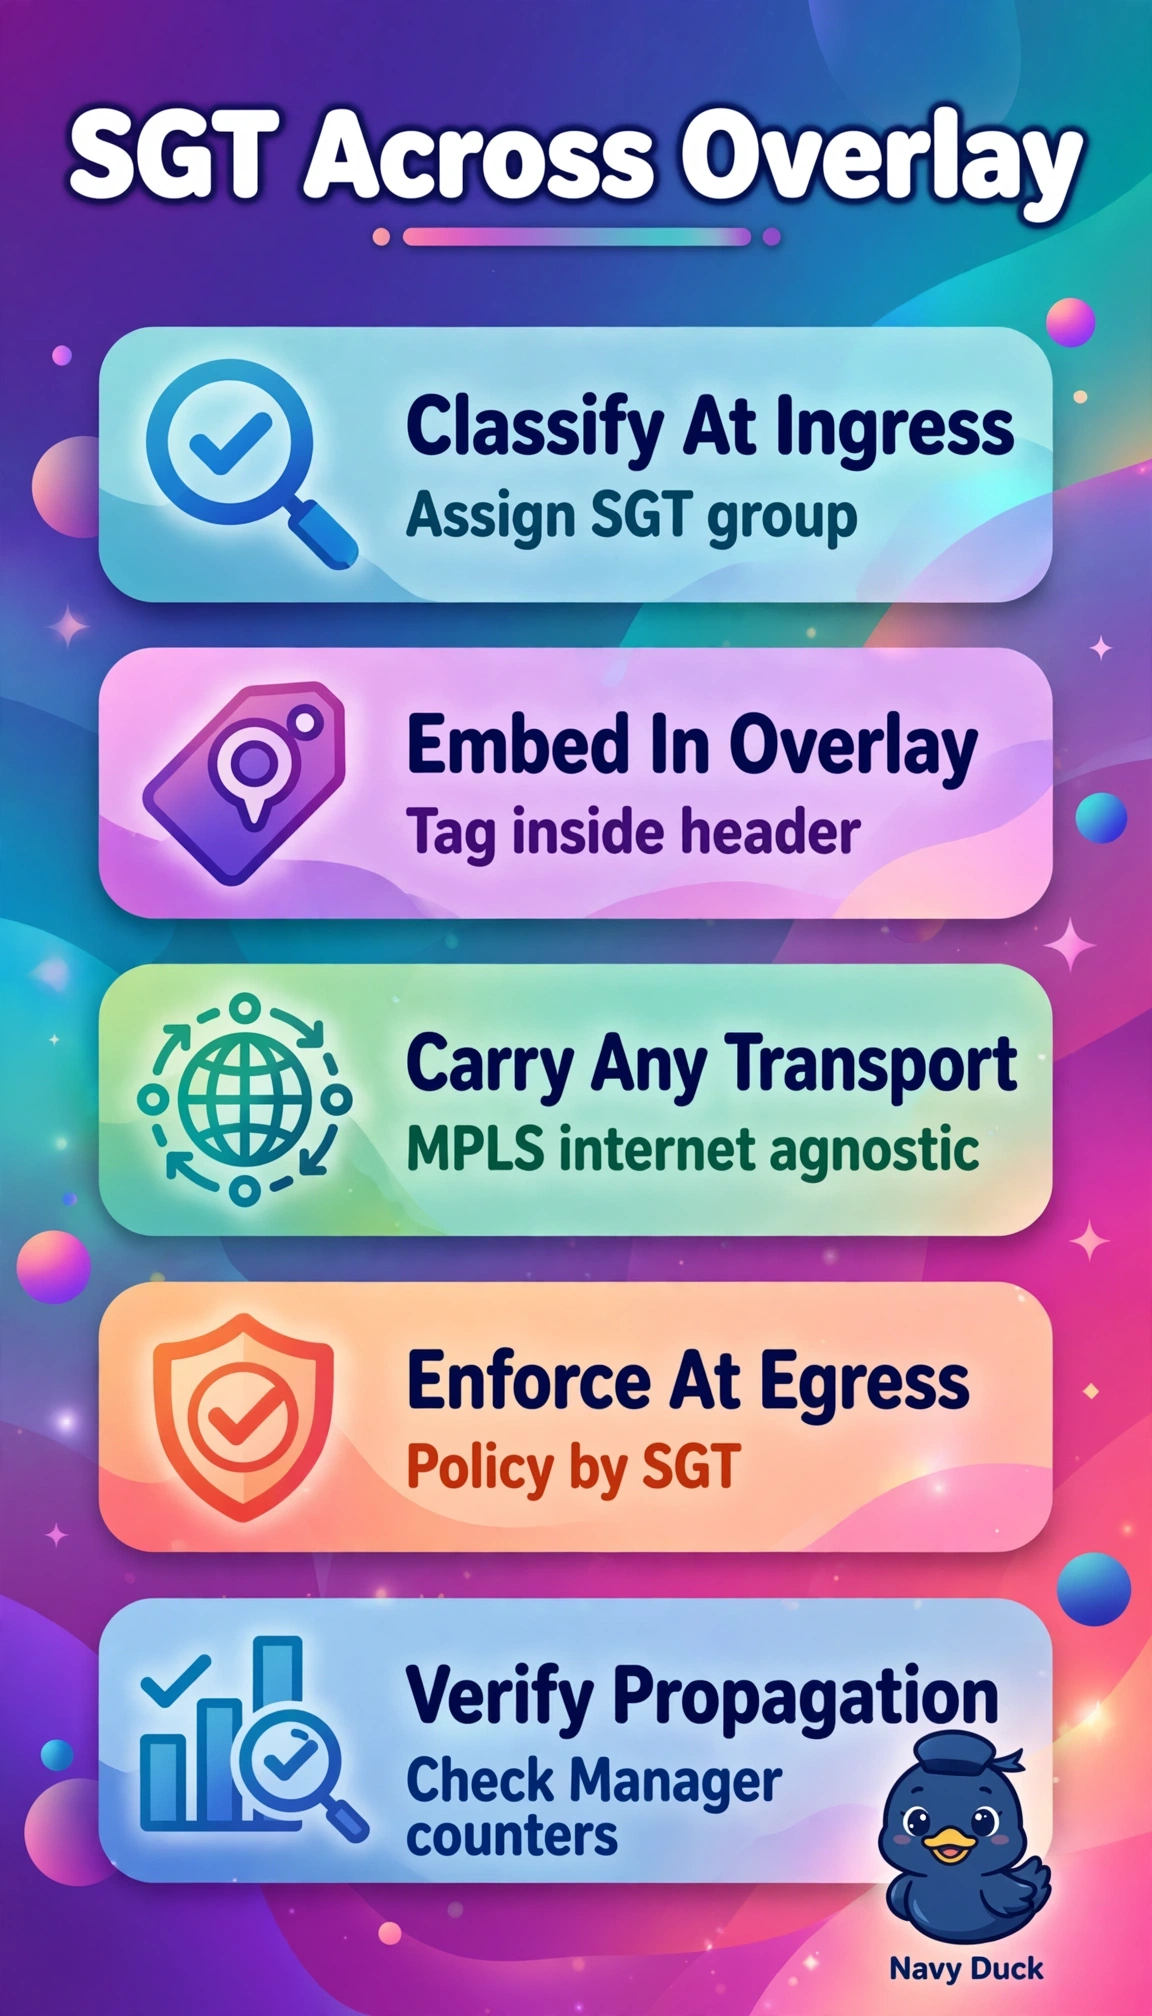
You need name badges that survive every hallway, not just one door. Overlay SGT-propagation tucks tags inside SD-WAN packets across any transport.
Full Explanation
Cisco SD-WAN can propagate Security Group Tags by embedding the SGT in the SD-WAN encapsulation so classification at ingress is preserved to egress for enforcement even when underlay transports strip inline SGTs, which meets end-to-end TrustSec policy over heterogeneous links. MACsec on uplinks fails by concept because link-layer encryption secures a single hop and does not carry SGTs across routed MPLS or internet paths. Zone-based firewall with DSCP fails by concept because firewall zones enforce inter-VPN traffic and DSCP conveys QoS, not identity group membership for TrustSec. Rekey on controller nodes fails by concept because the SD-WAN Controller (formerly vSmart) distributes control policy and keys but does not forward data traffic or insert SGT headers. Exam caveat is to distinguish overlay SGT propagation from Ethernet inline tagging. Practical check in SD-WAN Manager is to verify SGT in data policy and enforcement counters at the data-center edge.