
A new WAN Edge at a warehouse never reaches the controllers. It reaches the SD-WAN Validator on UDP 12346, but its DTLS handshake is repeatedly rejected, and the serial is already whitelisted. Which control-connection failure cause best explains this symptom set for control-plane troubleshooting?
Select an answer to reveal the explanation.
Short Explanation
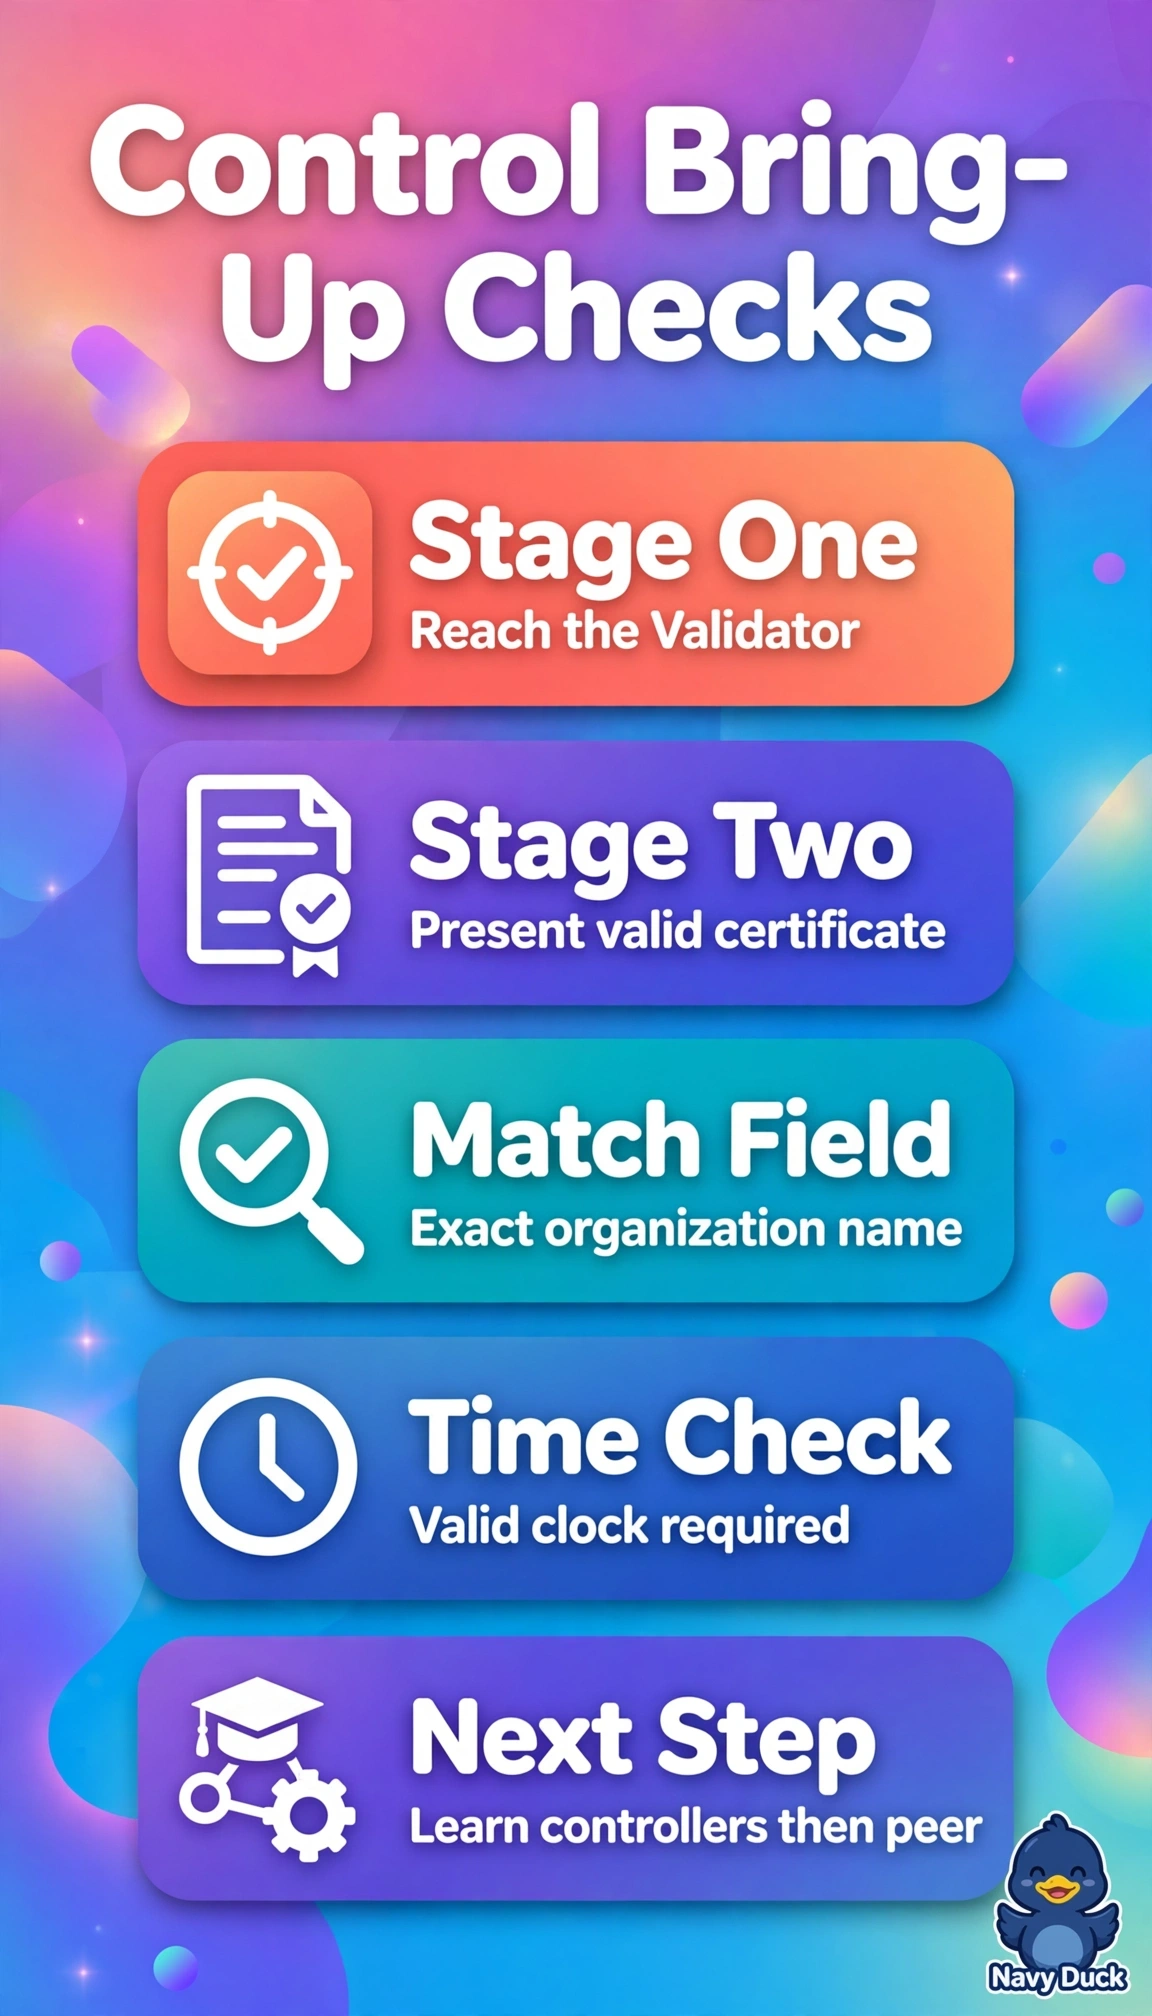
You're seeing your router stuck at the validator, so you'll want to check your identity details first. It's like getting stopped by the bouncer before you can join the party inside, and that organization-name match plus a valid certificate is your ticket in.
Full Explanation
The correct response isolates the failure to the Validator authentication stage, which must succeed before any peering to controllers can occur, and organization-name mismatch or expired and invalid certificates with untrusted roots are classic causes of repeated DTLS hello attempts that never progress when transport and onboarding identity are otherwise correct. The firewall and NAT hypothesis is a sound field check for blocked UDP 12346 and impaired Internet egress, yet it fails by concept here because the completed UDP 12346 exchange with the Validator already prove bidirectional transport liveness to that peer, shifting suspicion from underlay to trust. The whitelist synchronization hypothesis is also standard onboarding troubleshooting for rejected chassis, yet it fails by stated fact because the stem explicitly confirms the serial is already whitelisted, so re-syncing that list cannot explain continued authentication failure. The software compatibility hypothesis is legitimate for stalls during controller negotiation and protocol mismatch, yet it fails by sequencing because version negotiation occurs after successful Validator authentication, while this device never clears that earlier gate. An exam caveat is to distinguish Validator authentication from controller peering and orchestrator mediation, since questions deliberately provide one successful stage to force analysis of the next required stage rather than generic reachability. A practical check is to compare organization-name case-sensitively on Validator and edge, inspect certificate validity dates and root-CA installation with show certificate and system logs, and confirm Validator reachability counters increment while controller sessions remain down.