
A bank has LAN printers and servers behind a branch router and must filter traffic leaving the LAN toward the SD-WAN overlay differently from traffic arriving from the overlay to the LAN across all sites in one site list. Which data-policy direction design correctly applies from-service versus from-tunnel semantics?
Select an answer to reveal the explanation.
Short Explanation
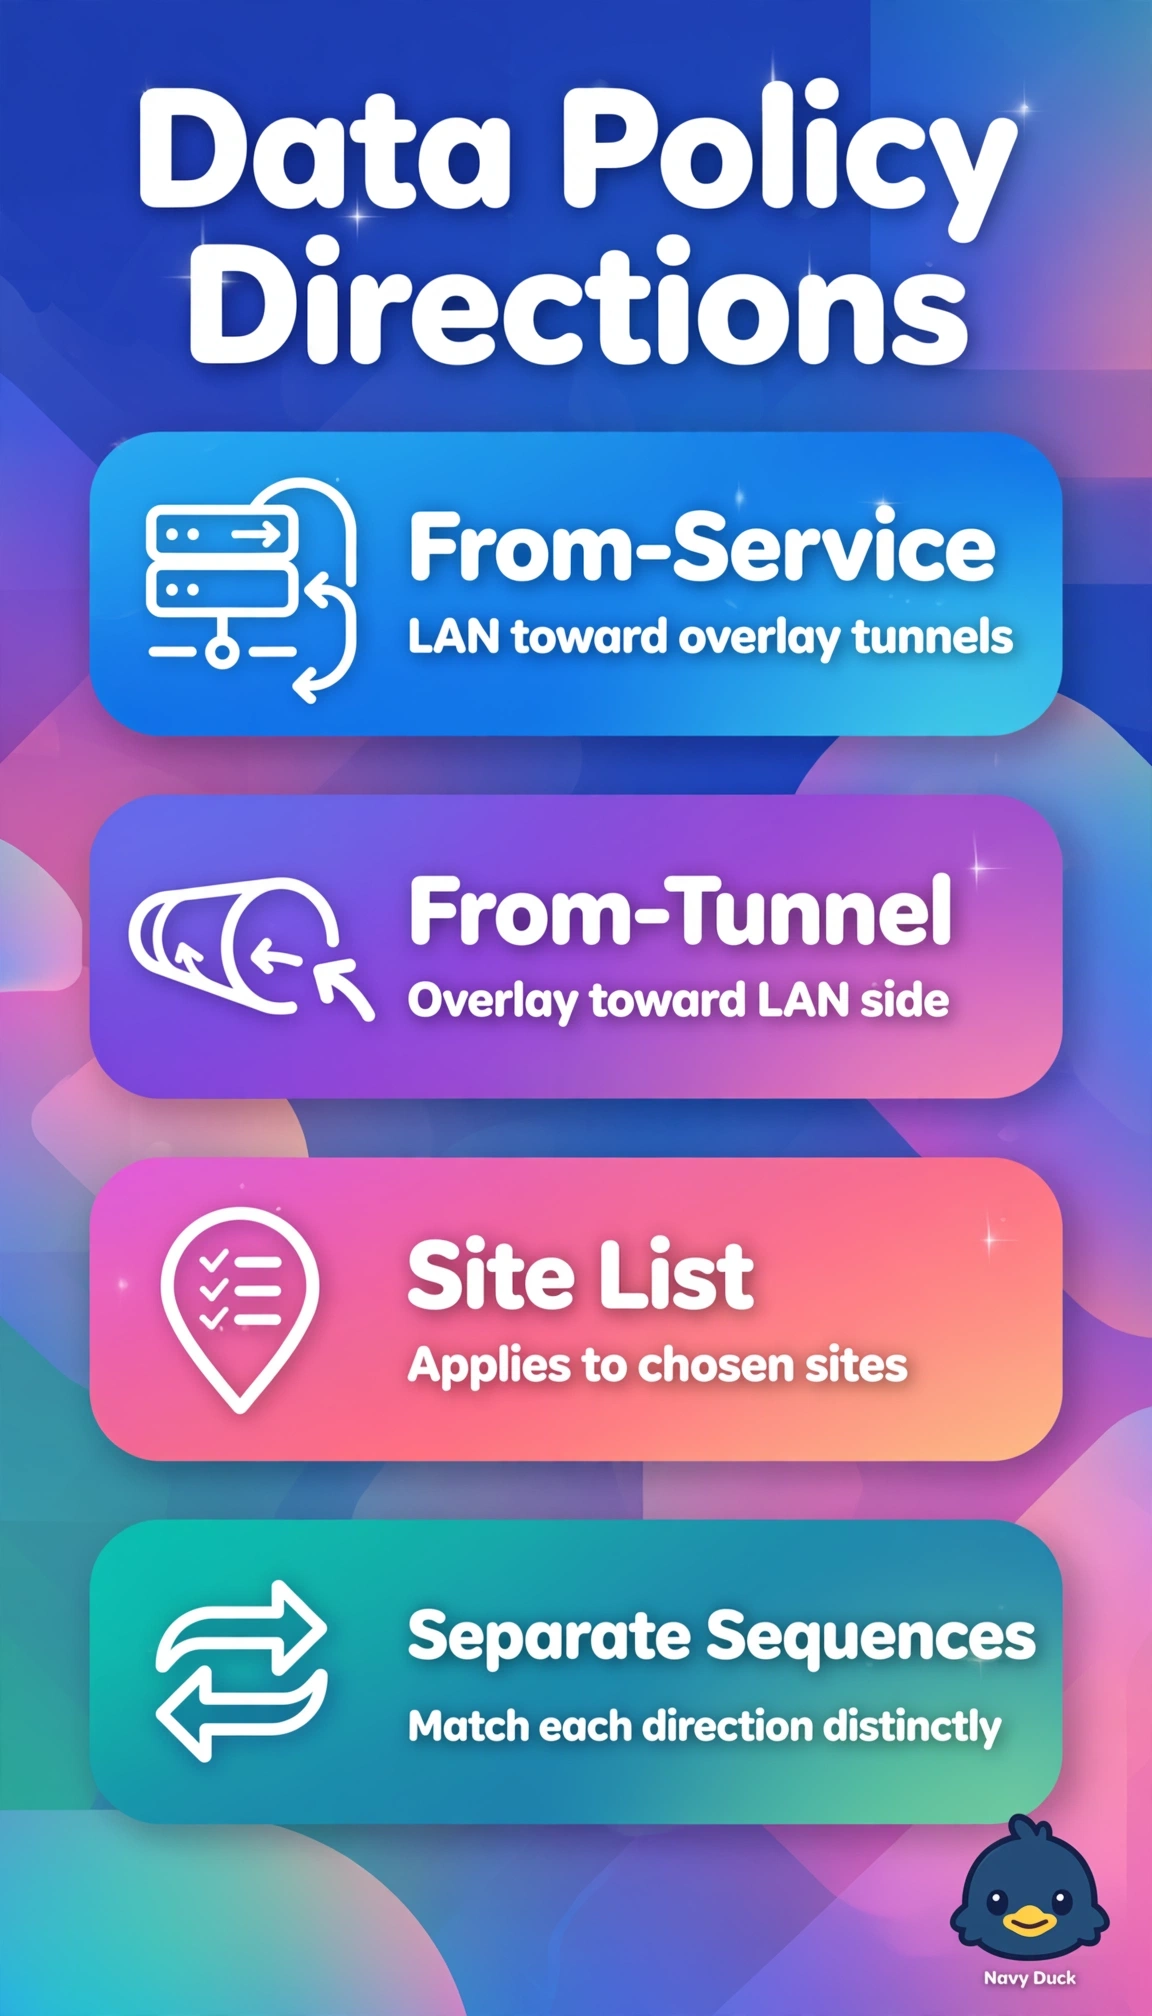
Direction trips up lots of engineers, so good on you for checking. From-service means leaving the LAN toward tunnels, like exiting a service-exit door. From-tunnel is the reverse entry from overlay to LAN.
Full Explanation
In Cisco SD-WAN centralized data policy, from-service correctly matches service-side LAN sources such as printers and servers as traffic enters the edge router toward the overlay, while from-tunnel correctly matches traffic decapsulated from IPsec tunnels leaving the overlay toward the LAN, so pairing them on a single site list enforces bidirectional but asymmetric filtering across all branches consistently. The separate-per-branch variant fails by scale concept because it replicates identical direction logic without the required single site-list aggregation, increasing operational overhead and risking policy drift across sites. The control-policy variant fails by policy-type concept because from-service and from-tunnel are data-policy sequences for forwarding and filtering, whereas control policy governs OMP route advertisement and TLOC selection and cannot enforce data-plane directionality. The reversed-direction variant fails by semantics concept because it applies tunnel decapsulation logic to LAN-originated traffic and service ingress logic to overlay-originated traffic, inverting match conditions and causing policies to miss or mishandle flows. For exams, remember direction is defined by packet origin relative to the router, not by allow or block intent, so read LAN-to-overlay versus overlay-to-LAN carefully. As a practical check, verify in SD-WAN Manager that the site list includes all branch IDs and preview device configurations to confirm from-service sequences show service VPN sources and from-tunnel sequences show tunnel sources before pushing.