
A NOC engineer builds a Python monitor that polls SD-WAN Manager alarms every five minutes. Security requires authenticated HTTPS calls with protection against cross-site request forgery on POST operations. Which authentication sequence enables the Manager REST API monitoring session correctly?
Select an answer to reveal the explanation.
Short Explanation
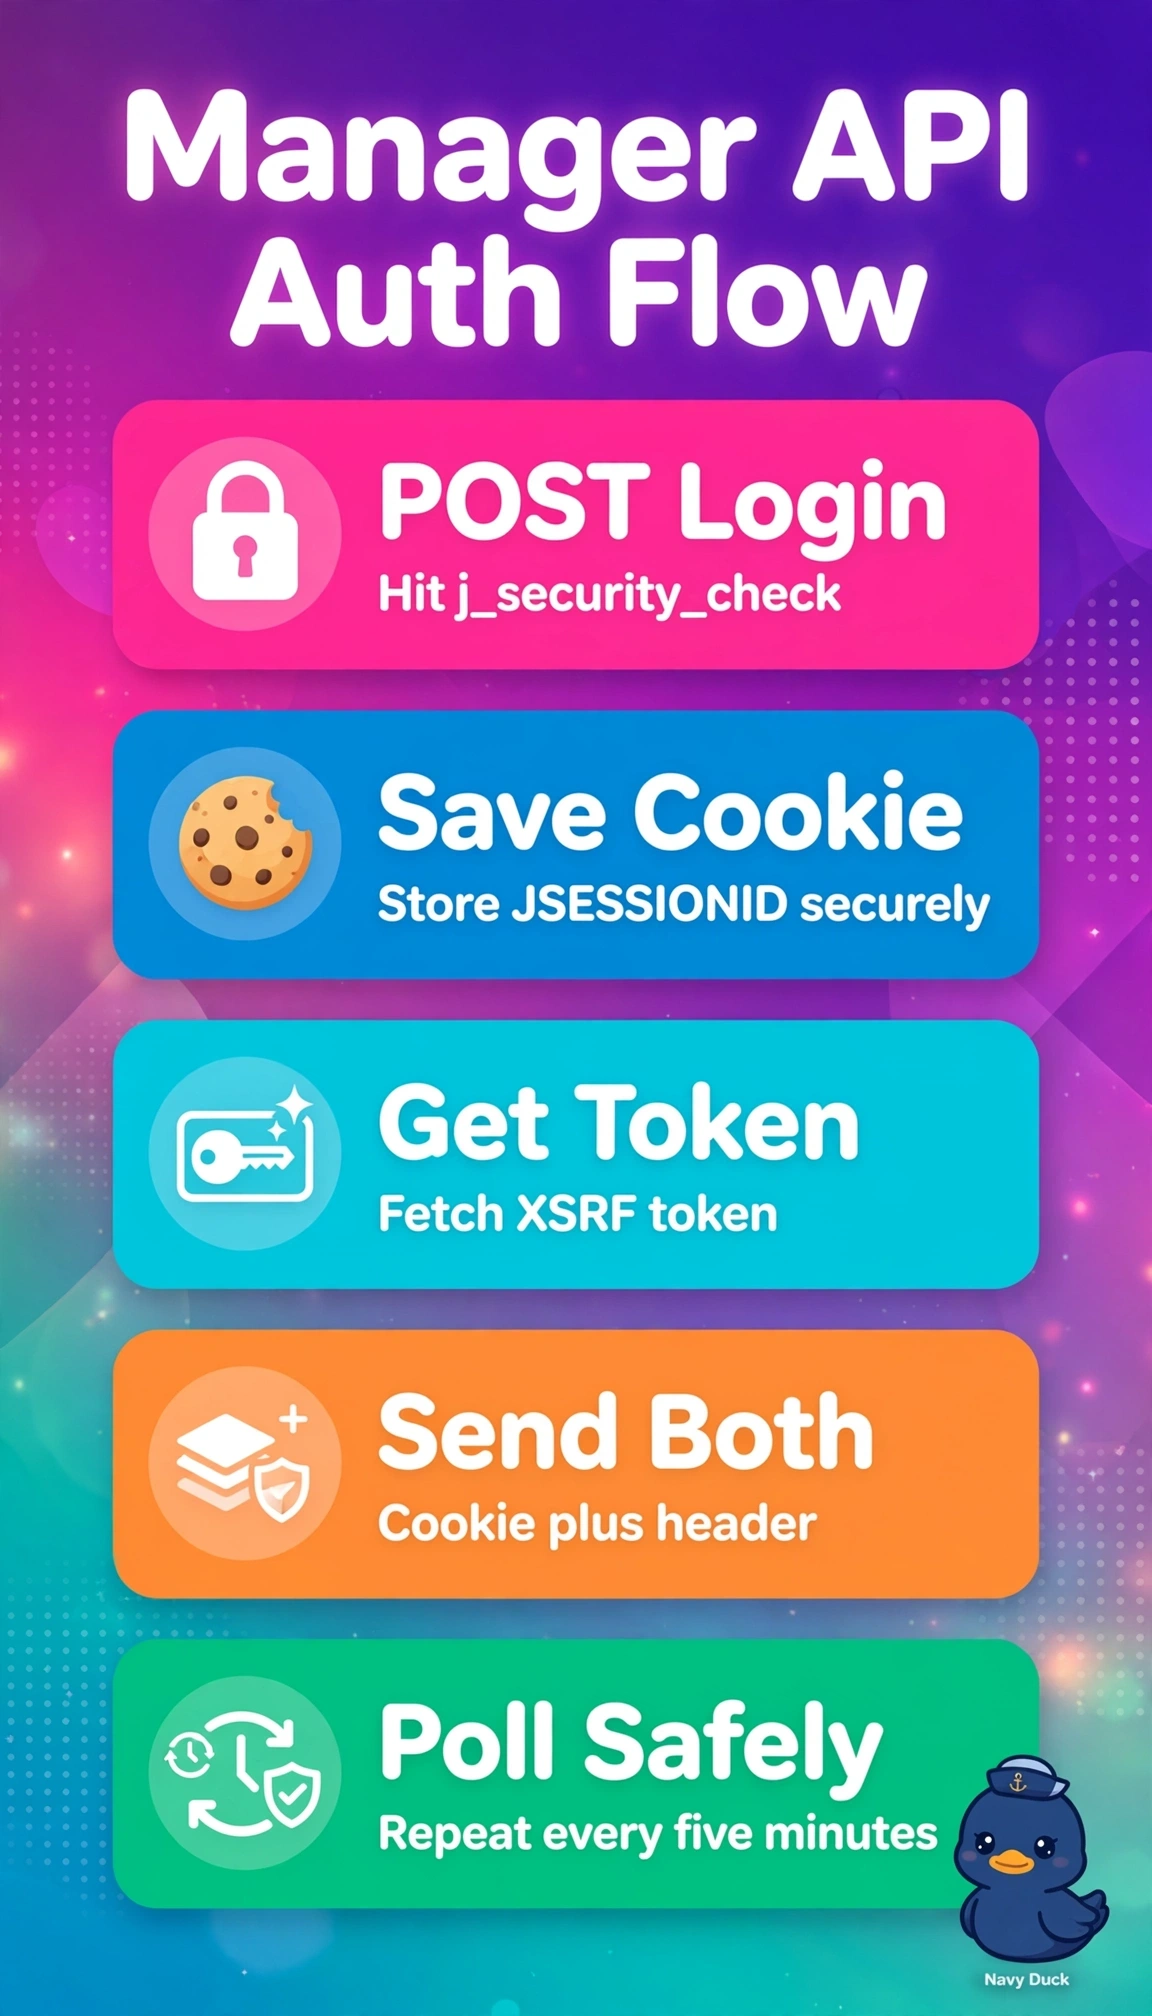
You're getting a wristband then showing it at every door. Keep that JSESSIONID cookie plus XSRF header together and your polling script stays authenticated.
Full Explanation
The correct sequence works because Cisco SD-WAN Manager uses form session authentication where a POST to j_security_check over HTTPS validates credentials and returns JSESSIONID, a subsequent GET to the client token service returns the XSRF token, and every later API call pairs the cookie with the X-XSRF-TOKEN header so POST operations carry both session identity and forgery protection required for the five-minute alarm monitor. The dataservice user login variant is attractive because that path pattern is common in REST APIs, but it fails on endpoint specificity since Manager only establishes the expected session through j_security_check. The Authorization bearer variant is attractive because bearer tokens are standard in modern APIs, but it fails on header contract since Manager checks X-XSRF-TOKEN with the cookie and does not accept the token as bearer authorization. The persistent WebSocket variant is attractive because streaming is efficient for monitoring, but it fails on interface contract since the task mandates REST polling on a fixed interval, with different session handling and error recovery. For exams, remember that HTTPS plus any login is insufficient unless endpoint, cookie, and header all match Manager semantics. For practice, test with requests Session to confirm Set-Cookie, retrieve a non-empty token, force expiry, and verify automatic re-login and token refresh before scheduling production polls.