
A new engineer diagrams steady-state connectivity for a single-homed branch WAN Edge and must label control versus data connections to each controller type. Tunnels to other branches are already shown. Which description correctly states the WAN Edge role in the data plane and which DTLS/TLS connections it forms to each controller?
Select an answer to reveal the explanation.
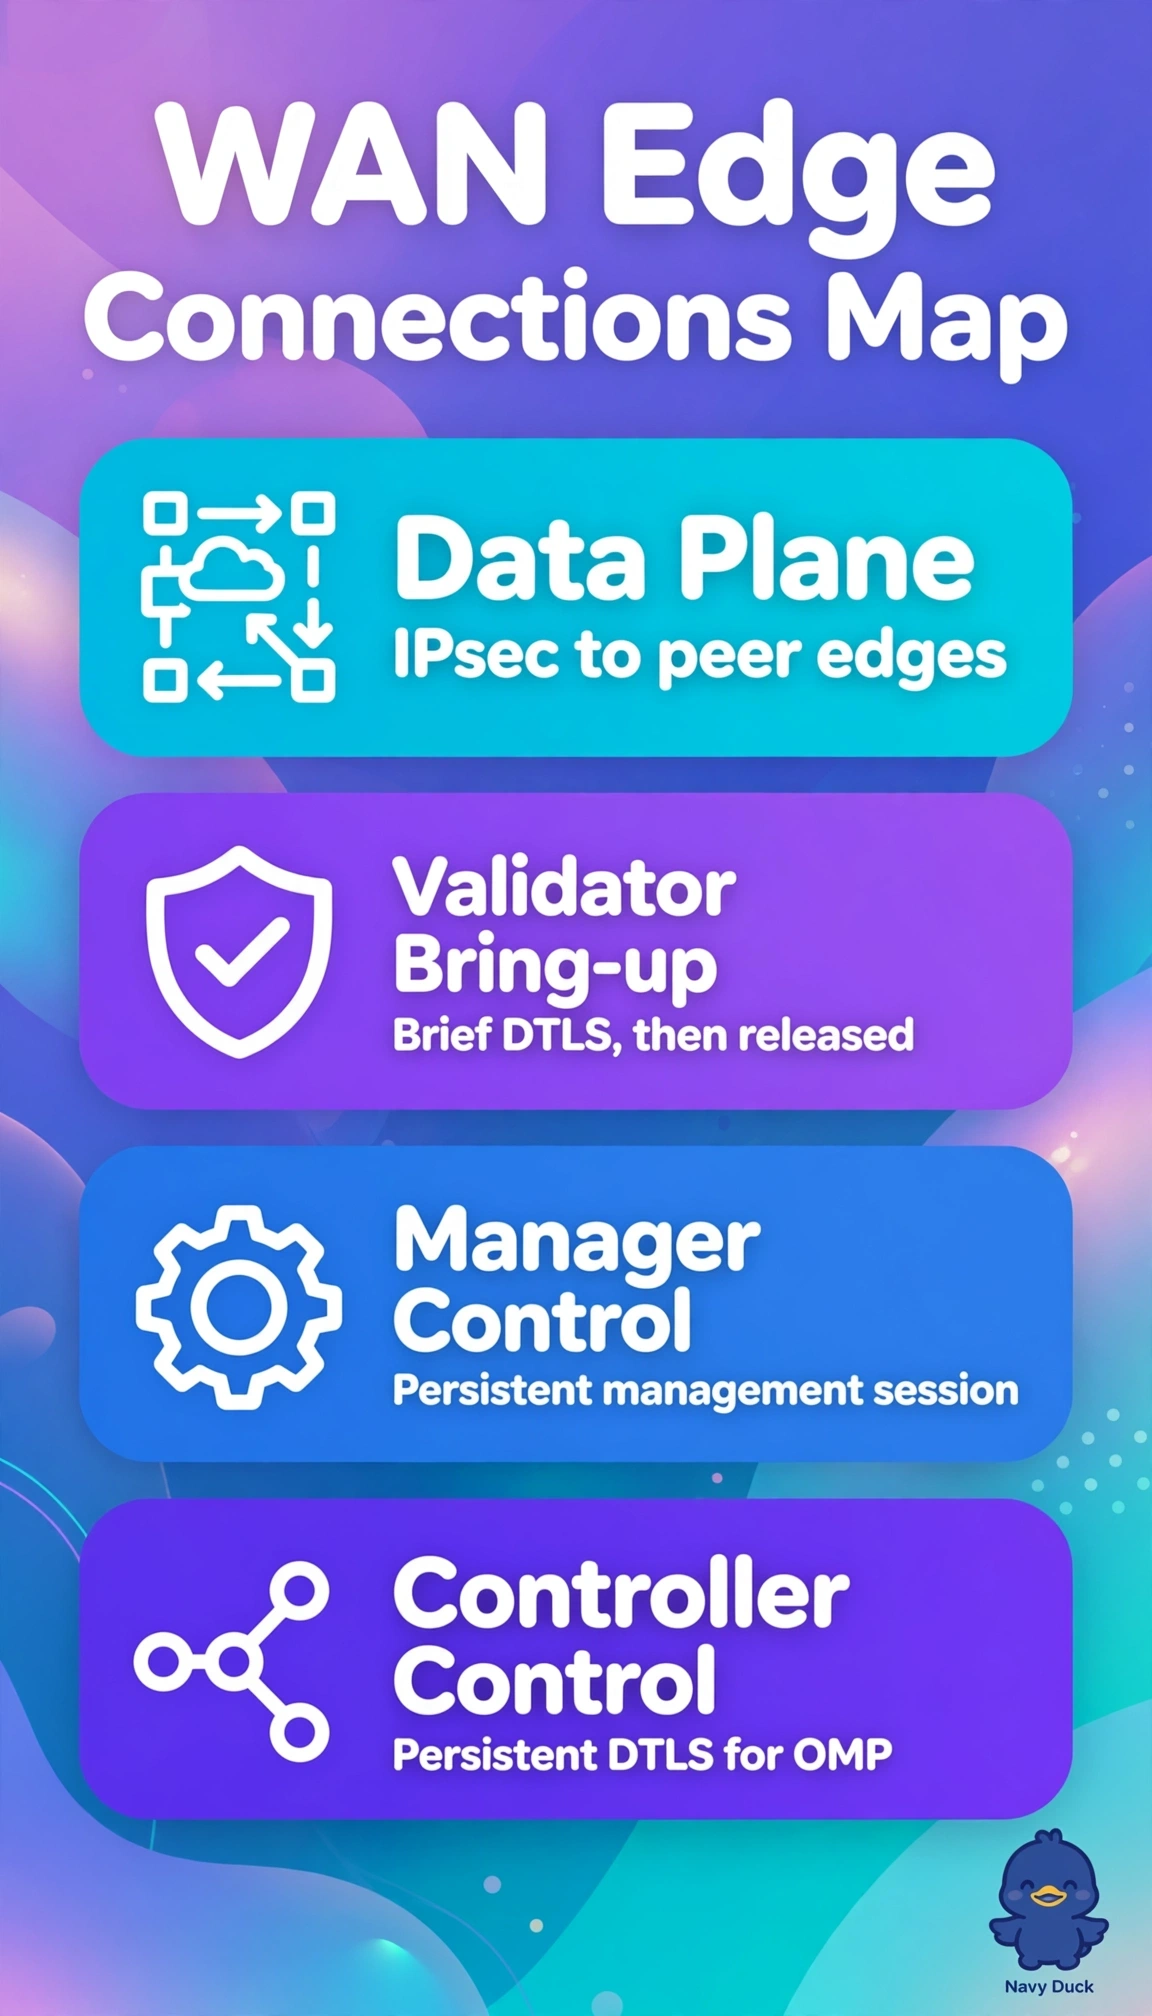
Short Explanation
You’ll see your WAN Edge wear two hats: it forwards branch data over IPsec and keeps steady DTLS/TLS control sessions open. The Controller and Manager stay in the conversation, while the Validator helps you get introduced during initial orchestration.
Full Explanation
In steady state, the WAN Edge forwards branch data over the edge-to-edge IPsec tunnels already shown; it does not send user traffic through a controller. The Controller distributes OMP routes and policy, and the Manager provides configuration and monitoring through persistent DTLS/TLS control sessions. The Validator is used transiently for authentication and discovery during initial orchestration, not as a continuing control peer. A design that adds a standby Validator session for failover gets the IPsec forwarding and persistent Controller and Manager sessions right, but misapplies the Validator’s orchestration role; resiliency comes from multiple Controllers and Managers, not a persistent Validator channel. A design that keeps the Validator session persistent while bringing up OMP to the Controller only when routes change reverses the steady-state roles: continuous Controller connectivity supports route exchange and policy convergence. A design that sends inter-branch traffic through the Controller for policy inspection confuses control with data forwarding; controllers signal state and do not forward user traffic once edge tunnels are established. Exam caveat: distinguish day-zero orchestration from steady-state control, especially when tunnels are already shown and operation is single-homed. Practical check: use show control connections to confirm persistent Controller and Manager sessions with no Validator session, then check IPsec counters for direct edge-to-edge forwarding.