
A campus edge runs EIGRP with two distribution switches in VPN 30 and must share campus subnets with remote sites over SD-WAN. The WAN Edge must keep EIGRP adjacency local while making routes visible to OMP peers. Which EIGRP and OMP redistribution design should the engineer configure?
Select an answer to reveal the explanation.
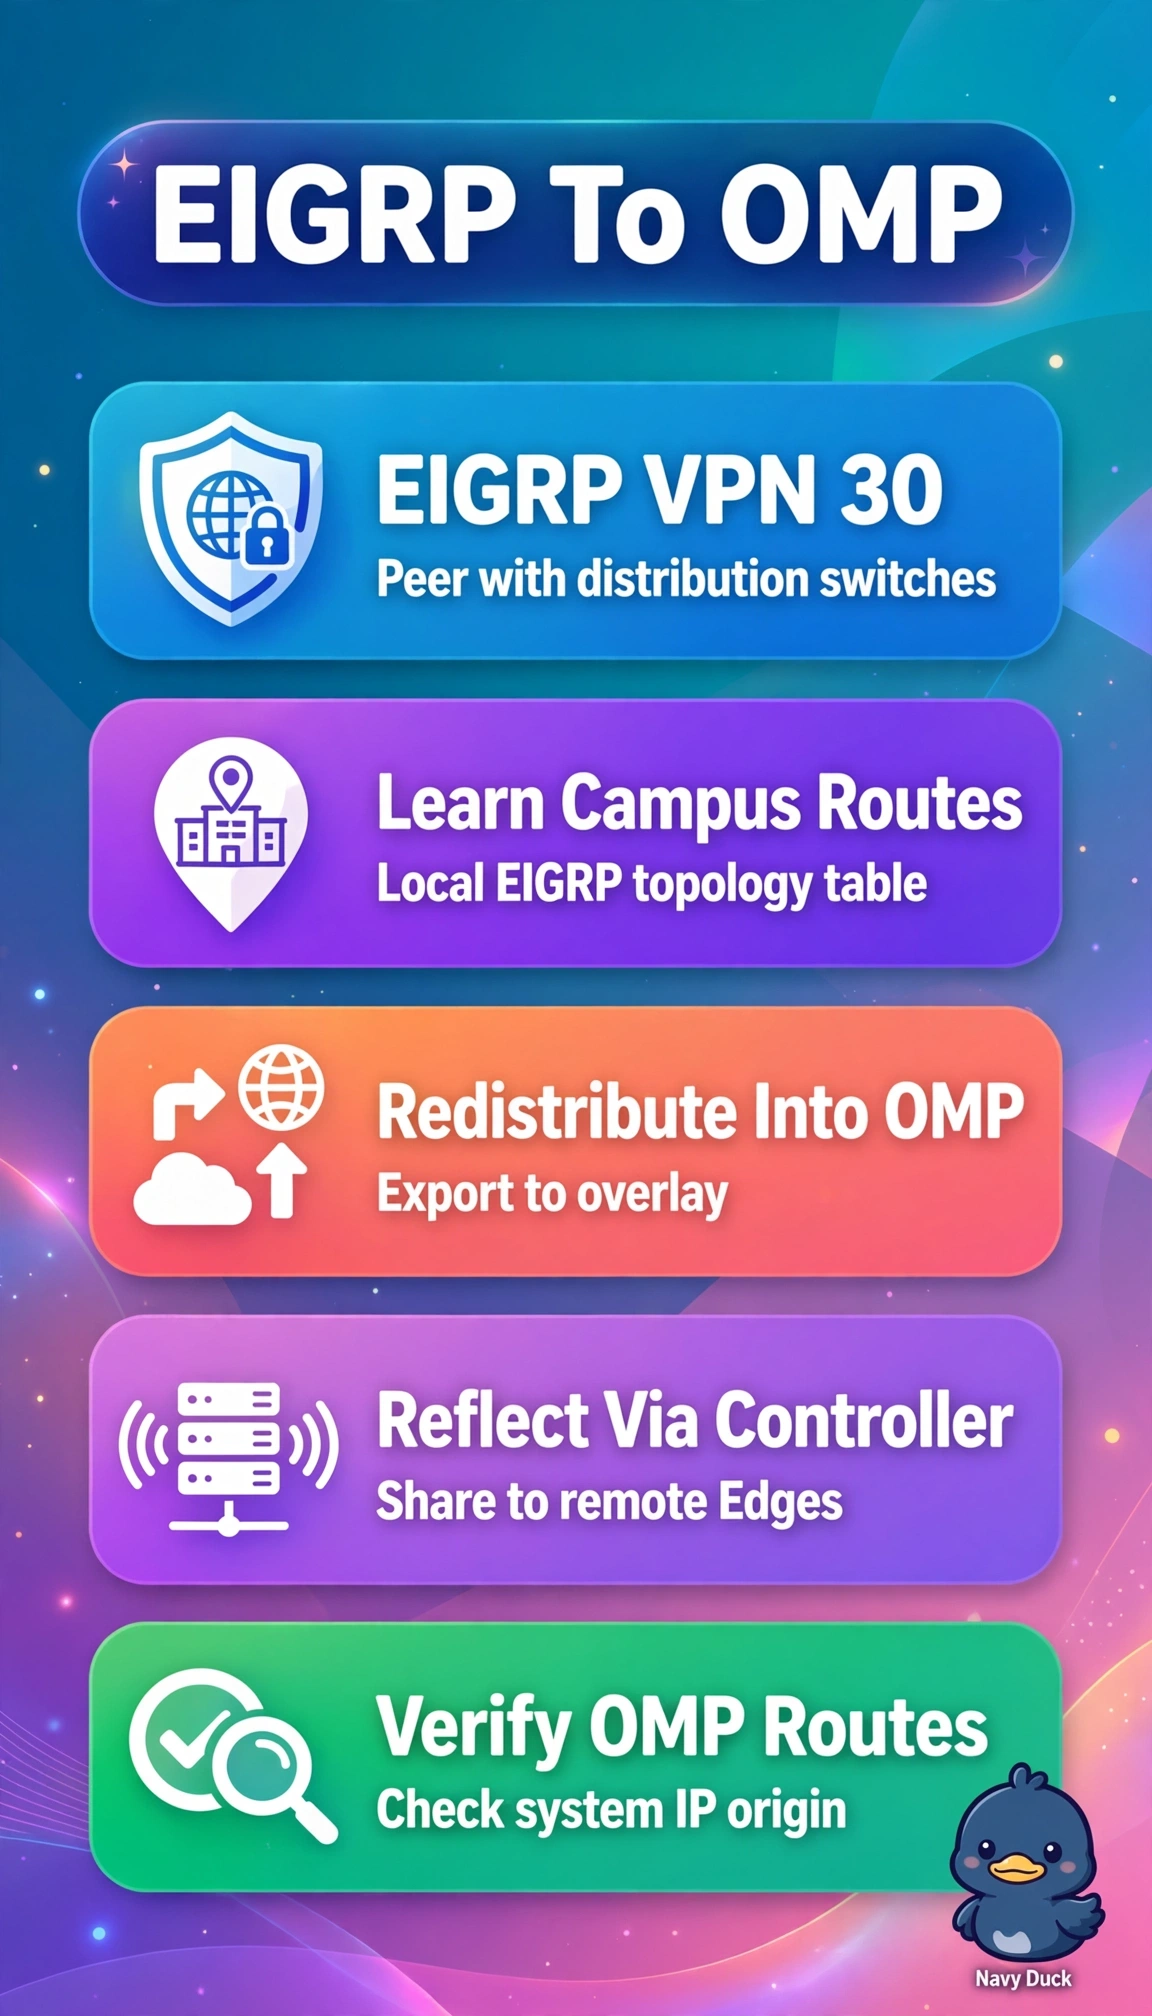
Short Explanation
You're letting neighbors chat locally while sharing news globally. Running EIGRP in the service VPN then redistributing into OMP bridges both worlds. It's like translating a local newsletter for national distribution.
Full Explanation
Service-side EIGRP must be configured inside the service VPN on the WAN Edge so hellos and adjacencies stay with the local distribution switches, and the learned EIGRP routes enter the overlay only through explicit redistribution from EIGRP into OMP, after which the Controllers reflect them to remote Edges that import them into their own VPN 30 instances. Running EIGRP in VPN 0 and redistributing OMP into EIGRP fails by VPN and direction because VPN 0 carries transport tunnels rather than service adjacencies, and importing OMP into EIGRP moves overlay routes locally instead of exporting campus routes. Redistributing only OMP into EIGRP in VPN 30 fails by direction because it achieves the reverse flow and leaves campus subnets invisible to OMP peers, so remote sites never learn them. Configuring EIGRP on the Controller fails by role because Controllers are OMP reflectors without service VPN adjacencies or LAN interfaces and never form IGP neighbor relationships with campus switches. Exam caveat: service protocol stays on the Edge in its VPN, overlay visibility always requires redistribute service protocol into OMP. Practical check: verify EIGRP neighbors are up on the Edge and the campus prefixes appear as OMP routes from that system IP.