
A civic data center loses reachability to its TACACS+ servers during a WAN outage. How should AAA method lists preserve admin access on the routers?
Select an answer to reveal the explanation.
Short Explanation
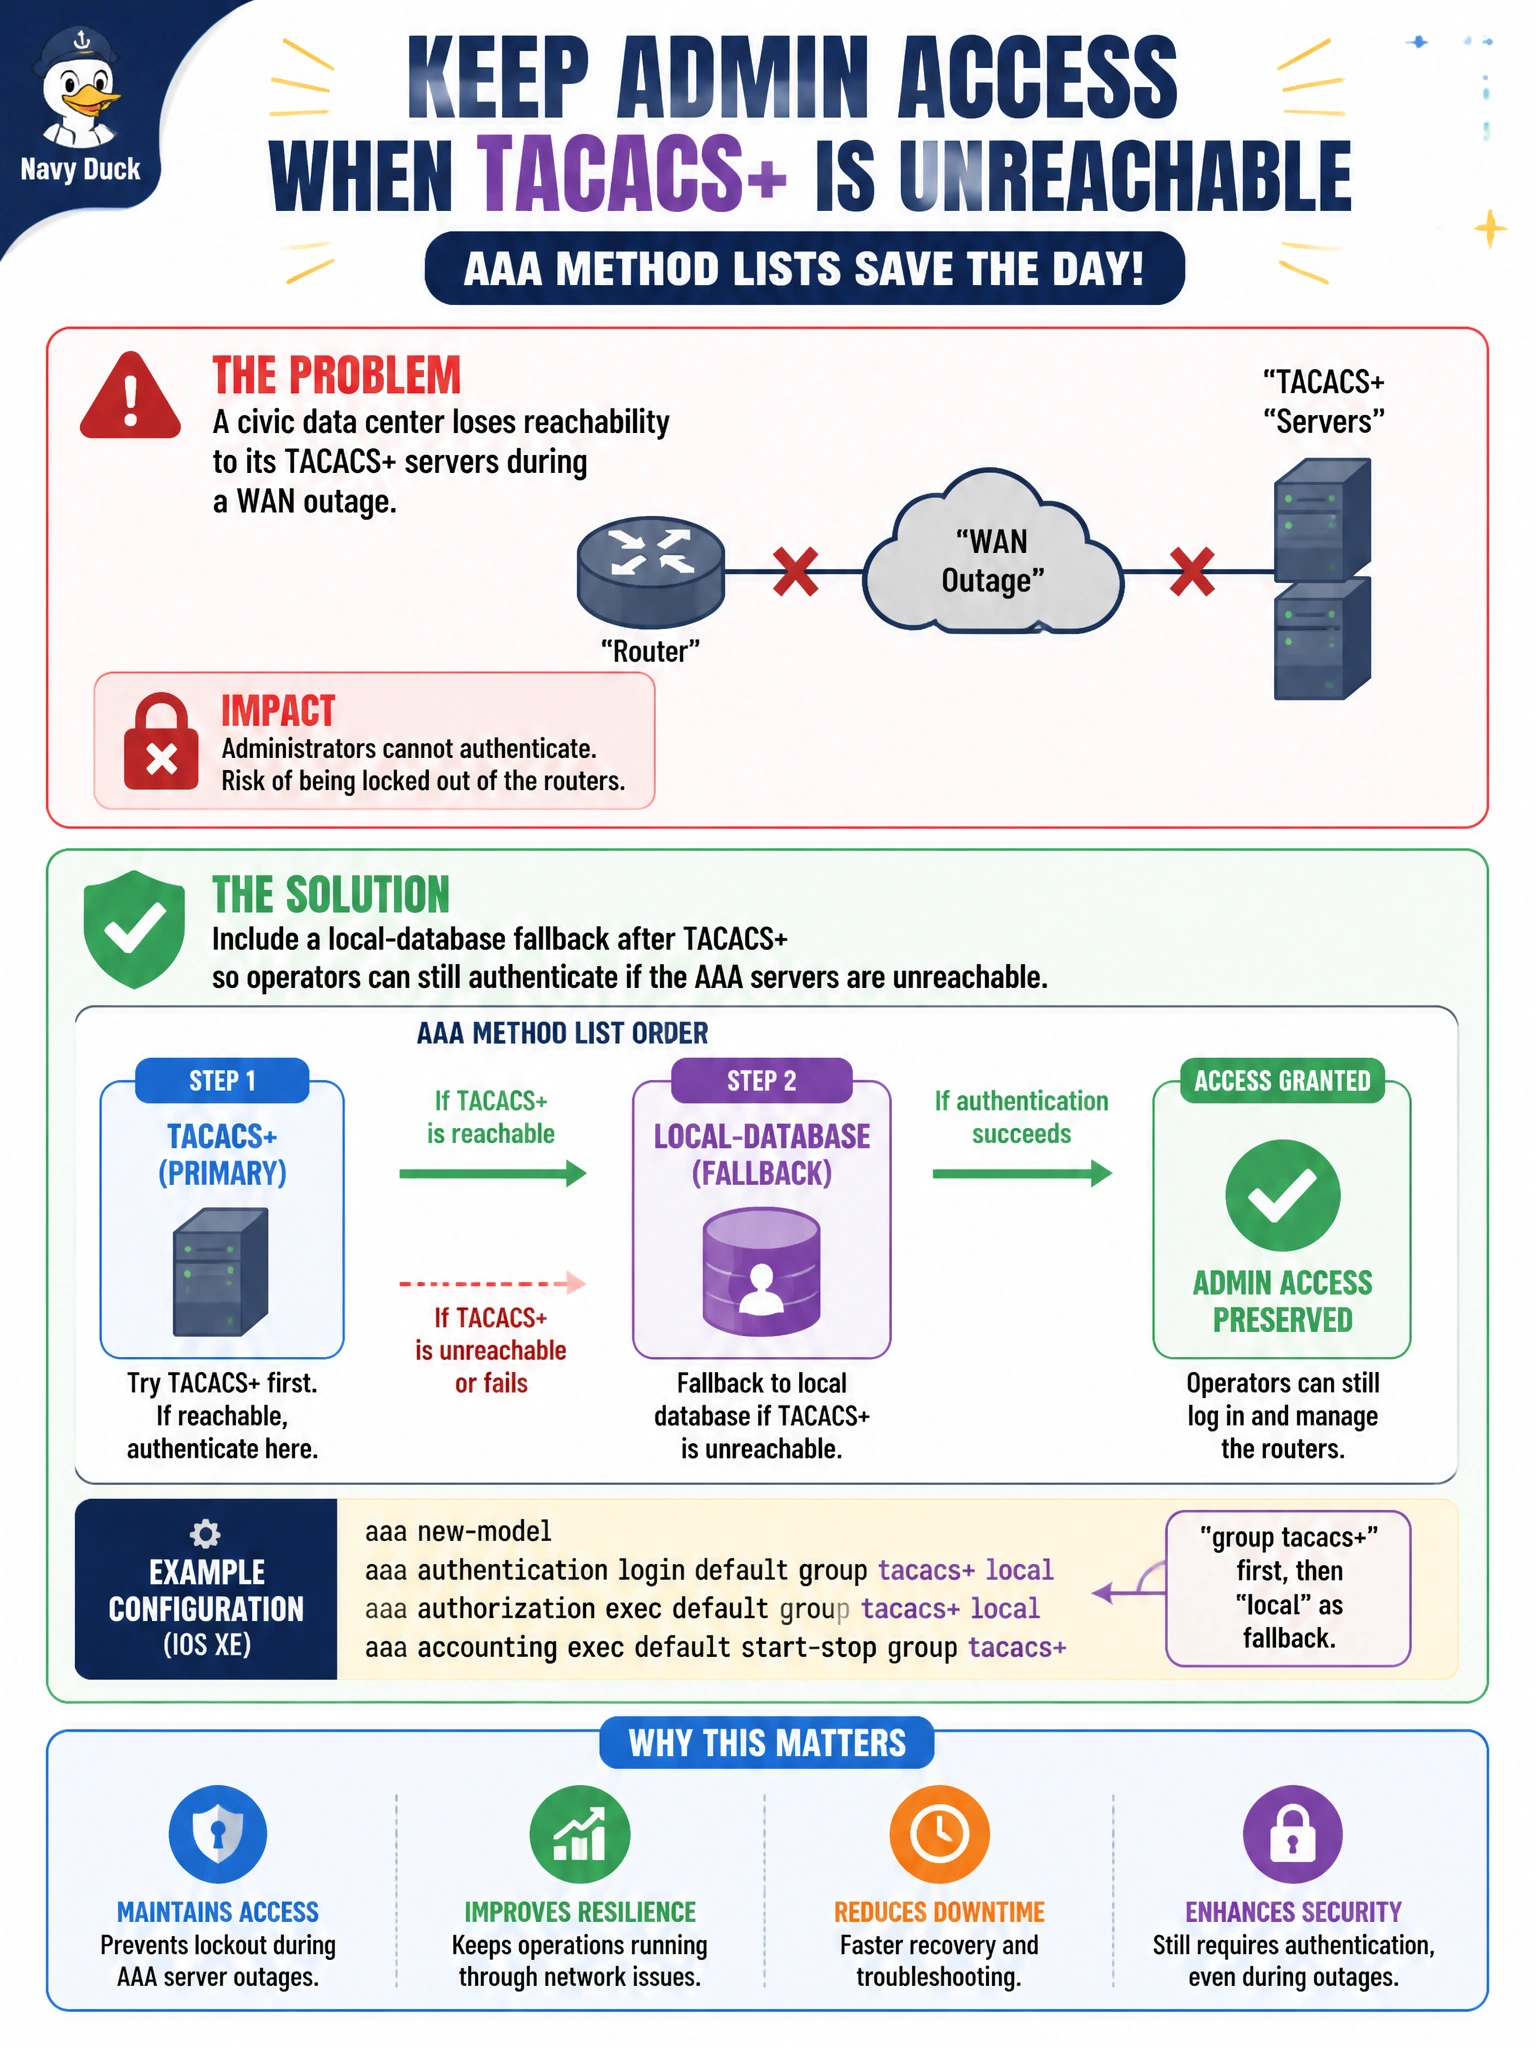
Put local after TACACS+ in the method list—when the AAA servers go dark in a WAN mess, the router's own user database still lets you in.
Full Explanation
When a civic data center loses reachability to its TACACS+ servers during a WAN outage, AAA method lists should include a local-database fallback after TACACS+. Operators still authenticate with a known local emergency user so data-center and edge routers remain manageable while centralized AAA is dark—critical for restoring civic services without waiting for WAN AAA path recovery.
Removing all local users permanently so only TACACS+ can ever succeed eliminates the break-glass path and strands engineers in the exact outage scenario. Disabling aaa new-model during outages to open unauthenticated VTY access is unsafe and operationally reckless. Relying on SNMPv3 informs alone for interactive shell login confuses monitoring with CLI access; informs do not provide an interactive admin shell when TACACS+ times out.
Exam caveat: ordered method lists with local fallback are the standard resilience pattern—not disabling AAA or deleting locals. Operational check: configure tacacs-then-local (or group-then-local) on VTY and console as policy allows, simulate AAA unreachable with an ACL or path shutdown, confirm local login still works, then restore TACACS+ and confirm centralized auth returns without leaving anonymous access enabled.