
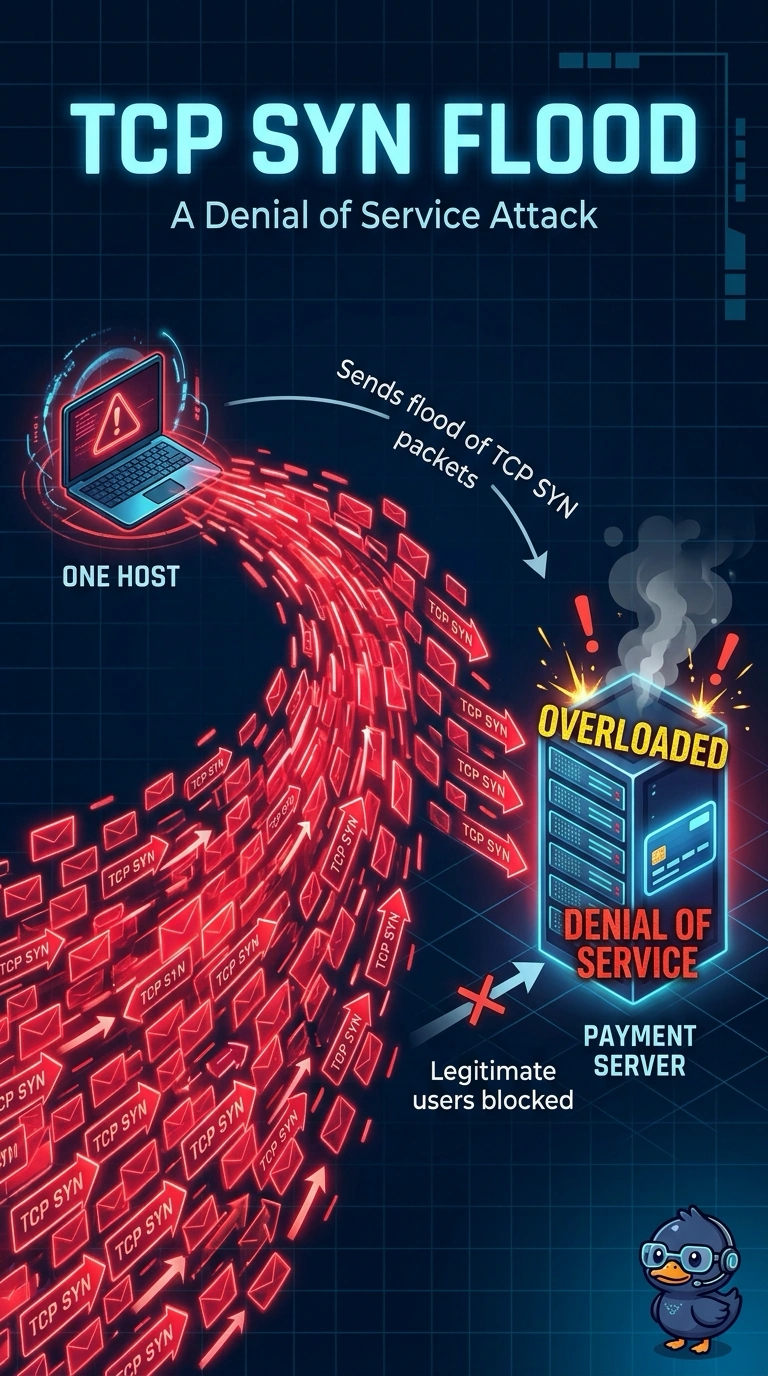
At a retailer, one host sends a huge number of TCP SYN packets to the payment server, and legitimate clients can no longer complete a connection. Which attack class fits this traffic?
Select an answer to reveal the explanation.
Short Explanation
One open hydrant can flood a street without a crowd helping. You are seeing denial of service from a single host. The trap is adding the word distributed just because the SYN count is large.
Full Explanation
The right selection is "Denial of service from the one host flooding the payment server with TCP SYN packets". One source is opening a flood of handshake requests, the payment server cannot finish legitimate connections, and nothing in the report shows a second source. Availability is what failed, and the source count is one. The statement "Distributed denial of service, with many outside sources overwhelming the payment server at once" would require many independent sources, and this report names a single host. The statement "On-path interception that still forwards shopper sessions after observing them in transit" would leave shopper sessions flowing while something in the middle read or altered them, but the failure here is that connections no longer complete. The statement "Cross-site scripting that runs an injected script in a shopper browser on the payment page" would place script content in a web page a browser executes, and a SYN flood has no page content at all. Exam caveat: if later logs show many sources, reclassify the same symptom as distributed; classify the sources you can actually see. Operational check: count the distinct source addresses sending SYNs to the payment server during the outage.