
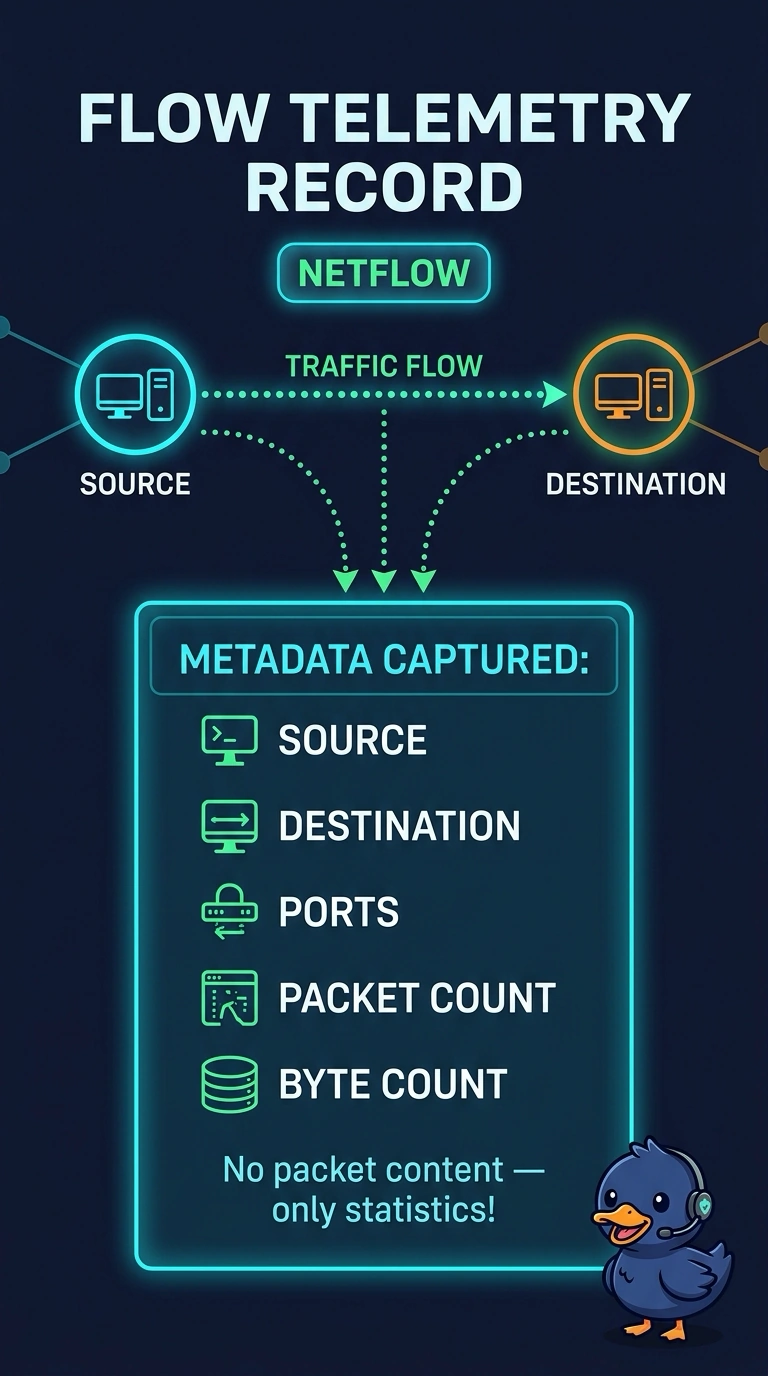
At a logistics hub, a record shows source, destination, ports, packet counts, and byte counts, and it contains no URL and no file contents. Which source type is that record?
Select an answer to reveal the explanation.
Short Explanation
A toll booth can tell you which vehicle passed and how much it weighed, not what was in the trailer. You have addresses, ports, and counts, with no URL and no file contents, so this is flow telemetry. The trap is a full packet capture, a proxy log, or an email-filter verdict.
Full Explanation
NetFlow or other flow telemetry showing addresses, ports, packet counts, and byte counts only is the source type. NetFlow and other flow telemetry record the conversation: source, destination, ports, packet counts, and byte counts. The hub record has those fields and has no URL and no file contents. That is a summary of the flow, which is what flow telemetry is for. The 5-tuple and the counts let you see who talked to whom and how much moved. They do not reconstruct the file. A full packet capture that stores the payload bytes, including any file contents from the transfer would store the payload bytes, including file contents. This record has no file contents, so it is not a full packet capture. A proxy log that records the user, the full URL, and a web category for the request at the hub would record the user, the full URL, and a web category. The record has no URL. A proxy log that cannot show a URL is not what this entry is. An email filter verdict that names the sender, the subject, and a spam or malware result would name a sender, a subject, and a spam or malware result. Nothing in the record is a mail verdict. An email filter does not log a bare set of addresses, ports, and counts as its decision. Exam caveat: a large byte count shows volume, not contents. Seeing a heavy flow is not the same as seeing the file that created it. Operational check: open the hub record and confirm the fields stop at addresses, ports, packet counts, and byte counts, with no URL and no payload.