
At a manufacturer, an analyst needs the payload bytes of one plant-floor transfer, not a summary of the conversation. Which source contains those bytes?
Select an answer to reveal the explanation.
Short Explanation
A shipping slip tells you a crate moved; it does not lay the parts out on the table. You need the payload bytes of one transfer, so you want a packet capture. The trap is a flow summary, a door-badge log, or a vulnerability score.
Full Explanation
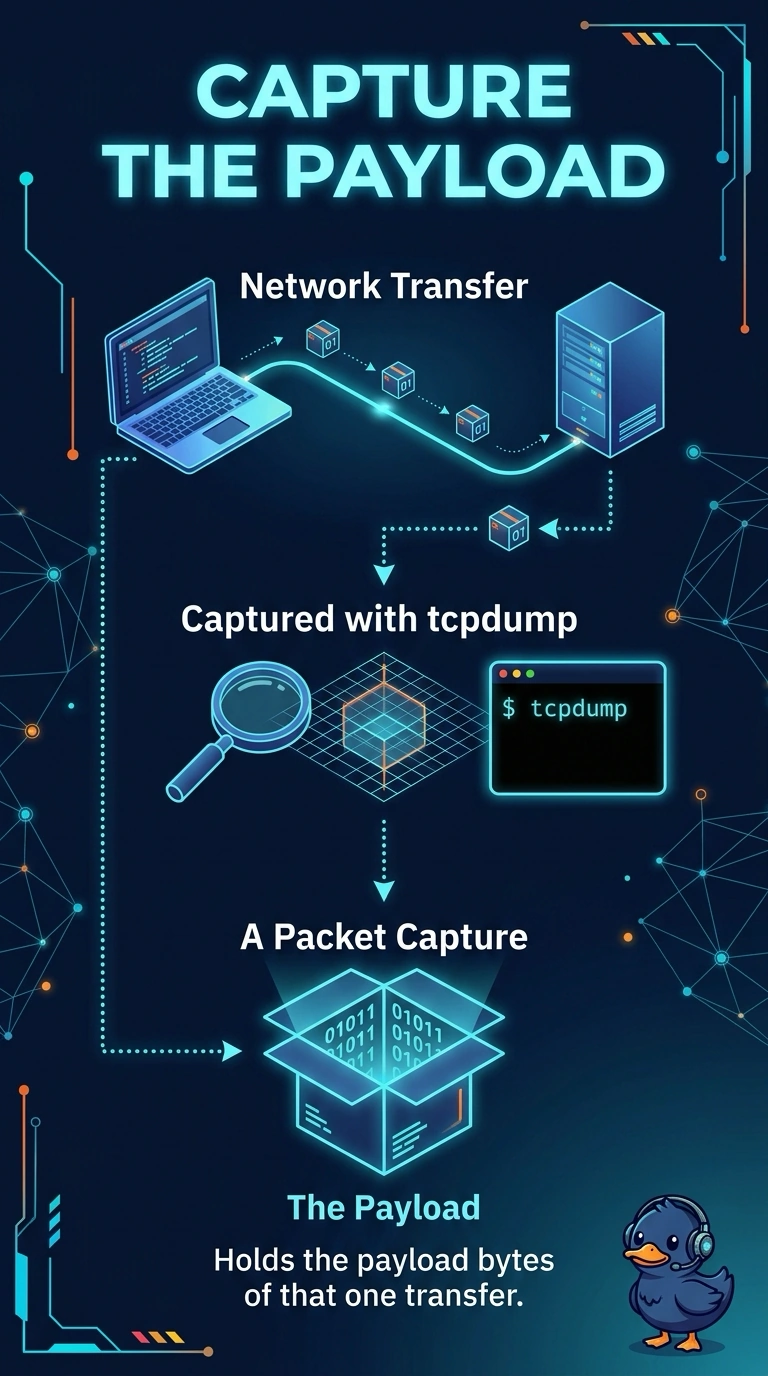
A packet capture, such as one taken with tcpdump, that holds the payload bytes of that one transfer is the source that holds the payload bytes. A packet capture records the packets that passed the capture point, including the bytes inside them. The analyst needs those bytes for one transfer, not a summary, so a capture such as one taken with tcpdump is the record that can contain them. A NetFlow record that summarizes addresses, ports, packet counts, and bytes but omits the transferred payload summarizes addresses, ports, packet counts, and byte counts. Byte counts say how much moved. A flow record omits the transferred contents, so it cannot supply those bytes. A badge log that records who entered the plant floor and when the door opened for them records who badged onto the plant floor and when a door opened. Physical entry is not the transfer, and a badge log has no packet payload. A vulnerability scan score that rates weaknesses found on the plant hosts during a scan rates weaknesses found on hosts. A score from a scan is not a copy of a transfer, and it does not contain the bytes that moved across the network. Exam caveat: a capture contains the bytes that actually passed the capture point. If you captured on the wrong path, the transfer will not be in the file, but the source type that can hold payload is still the capture, not the flow summary. Operational check: capture on the path of the transfer and confirm the payload bytes are present in the saved packets rather than stopping at a flow record.