
At a university, an alert is still unverified and the only fact in hand is a single failed logon on one lab PC. What handling step fits the evidence so far?
Select an answer to reveal the explanation.
Short Explanation
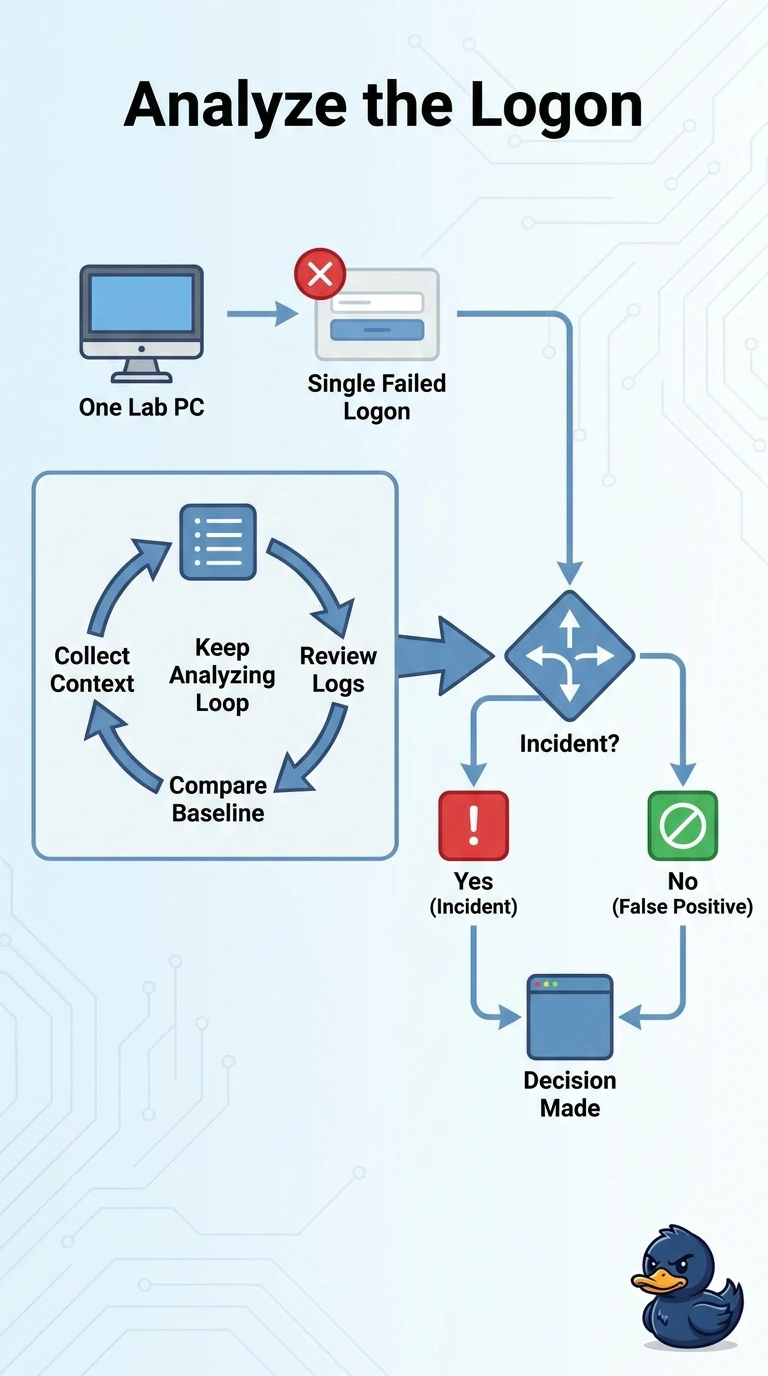
One wrong-number call is not a reason for you to evacuate the campus. The alert is unverified and the only fact is a single failed logon, so the step is analysis. Wiping every lab, holding lessons learned, or revoking the campus PKI skips that decision.
Full Explanation
One unverified failed logon is still in detection and analysis: the team does not yet know whether an incident exists. Keep analyzing the single failed logon until you can decide whether it is an incident, is the step that matches the evidence. Eradicate every lab image on campus before anyone reviews the single failed logon jumps to eradication across systems that have not been tied to this event. Open the lessons-learned meeting for an incident that nobody has confirmed yet is post-incident work, and there is no confirmed incident to review. Revoke the entire campus certificate authority over one failed logon that is still unverified is campus-wide containment of a trust system this fact does not implicate. Exam caveat: NIST SP 800-61 Rev. 3 maps detection and analysis onto CSF 2.0 Functions, and the exam still uses that phase name; a single failure is not enough to skip the decision. Operational check: review the failed logon, event 4625, for account and source, and see whether a successful logon, event 4624, followed for the same account before any campus-wide action.