
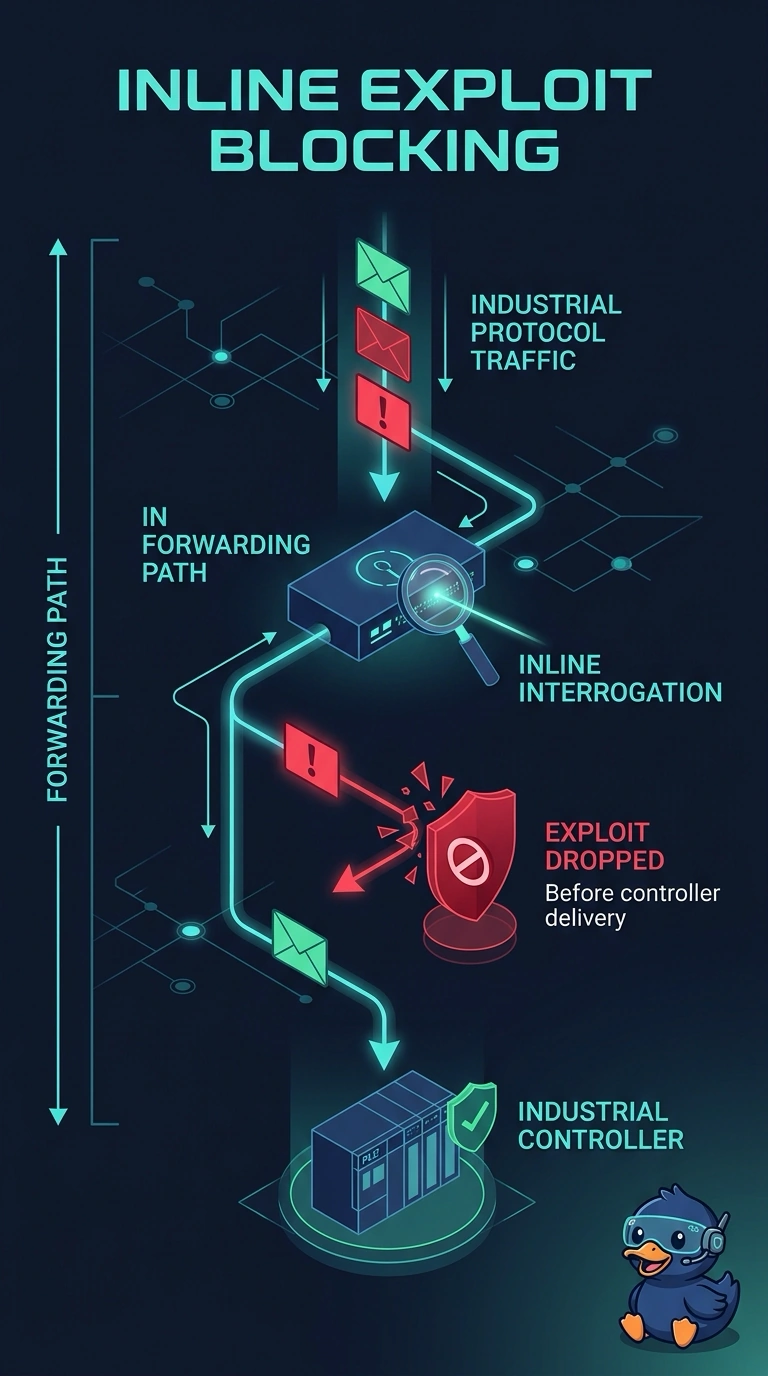
At a manufacturer, a security device sits in the forwarding path and drops an industrial-protocol exploit before the packet reaches a controller. Which deployment is that device using?
Select an answer to reveal the explanation.
Short Explanation
You’re looking for inline interrogation: the device is in the forwarding path and can drop the exploit before it reaches the controller. A passive tap copies frames, NetFlow summarizes conversations, and a syslog server stores event messages; none of those descriptions is the device dropping the packet.
Full Explanation
A device on the forwarding path that discards an exploit packet is performing inline interrogation. Because it can drop the original packet before the controller receives it, this deployment matches the described action. A passive tap copies each frame and leaves the original on the wire; its copy can be inspected, but the tap does not drop the original packet. A NetFlow export summarizes each conversation toward a collector after the fact; it does not sit in the forwarding path and discard the exploit. A syslog server stores event messages from plant devices for later review; storing a message does not remove the packet from the path to the controller. The key distinction is whether the device can act on the original traffic before delivery, rather than merely copy or record information about it. Exam caveat: a sensor receiving a copy can still alert on an exploit, but alerting on a copy is not the same as dropping the original frame. Practical check: confirm the device is inserted in the forwarding path and that a test packet matching the exploit is discarded before it arrives at the controller.