
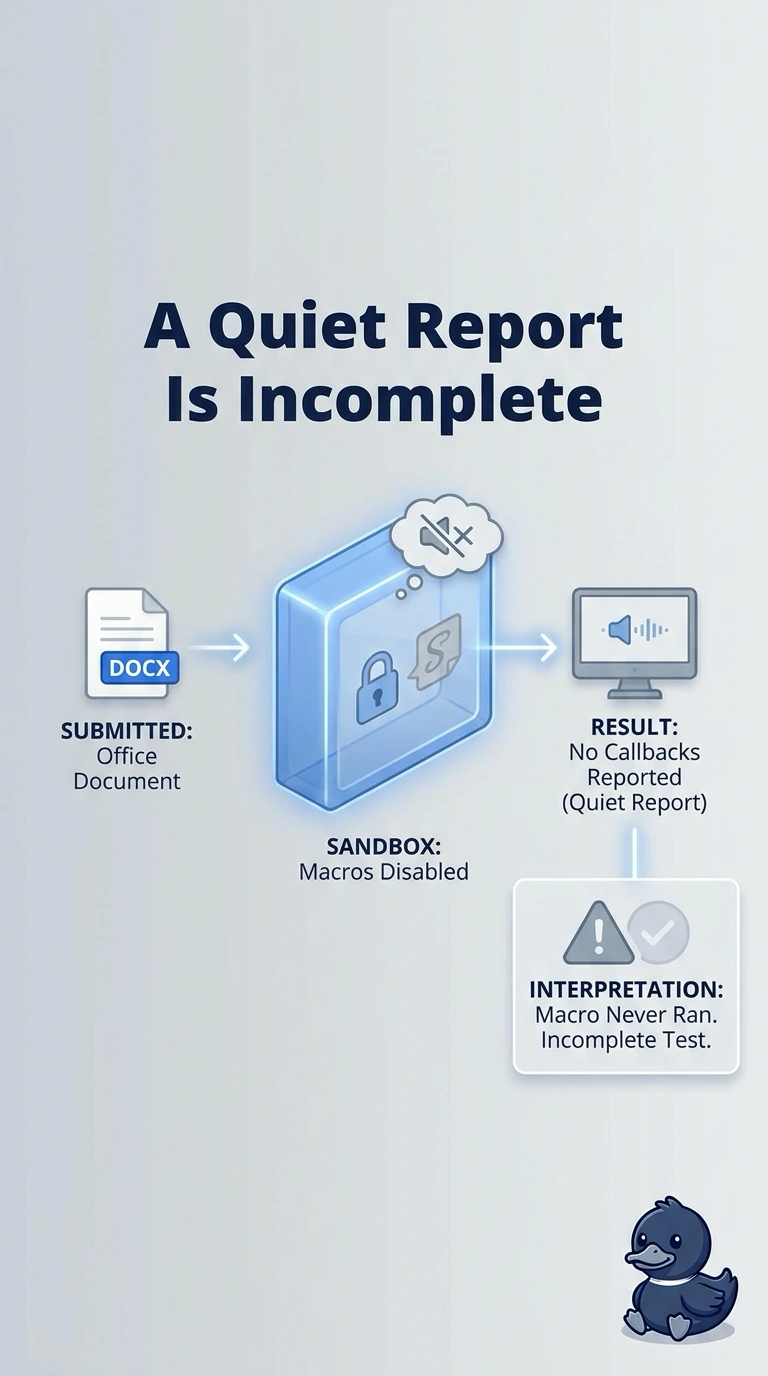
An MSSP customer submits an office document. The sandbox opens it and reports no callbacks, and macros are disabled in the sandbox image. What limitation should the analyst record?
Select an answer to reveal the explanation.
Short Explanation
A fire drill with the alarm switch taped down does not prove the building is safe. You have a detonation that never ran the macro, so the quiet report is incomplete. The trap is calling macros harmless, declaring a hash collision certain, or calling the file a certificate.
Full Explanation
The customer document was opened in an image that has macros disabled. A macro that never runs cannot open a callback, so silence in this report does not exercise the feature most likely to carry the payload. The hash can still identify the file. The limitation is the incomplete detonation. "The detonation never ran the macro, so a quiet report is an incomplete test of the file" states that limit. "Office macros cannot be malicious, so this quiet run is enough to clear the document" is false, and a disabled macro is not a clean bill of health. "A hash collision is certain, so the file identity printed on the report cannot be trusted" invents a collision the quiet run does not show. "The submitted document is a certificate, so the sandbox should not show host behavior" mislabels an office document. Exam caveat: a quiet detonation can also be evasion, and here the image setting already shows the macro was not tested. Operational check: confirm macros are disabled in the image, then detonate again with macros enabled and compare the new events with the quiet report.