
At a logistics hub, the SIEM shows Windows event 1102 on a warehouse PC and then no further security events from that PC. What is the best reading of those facts?
Select an answer to reveal the explanation.
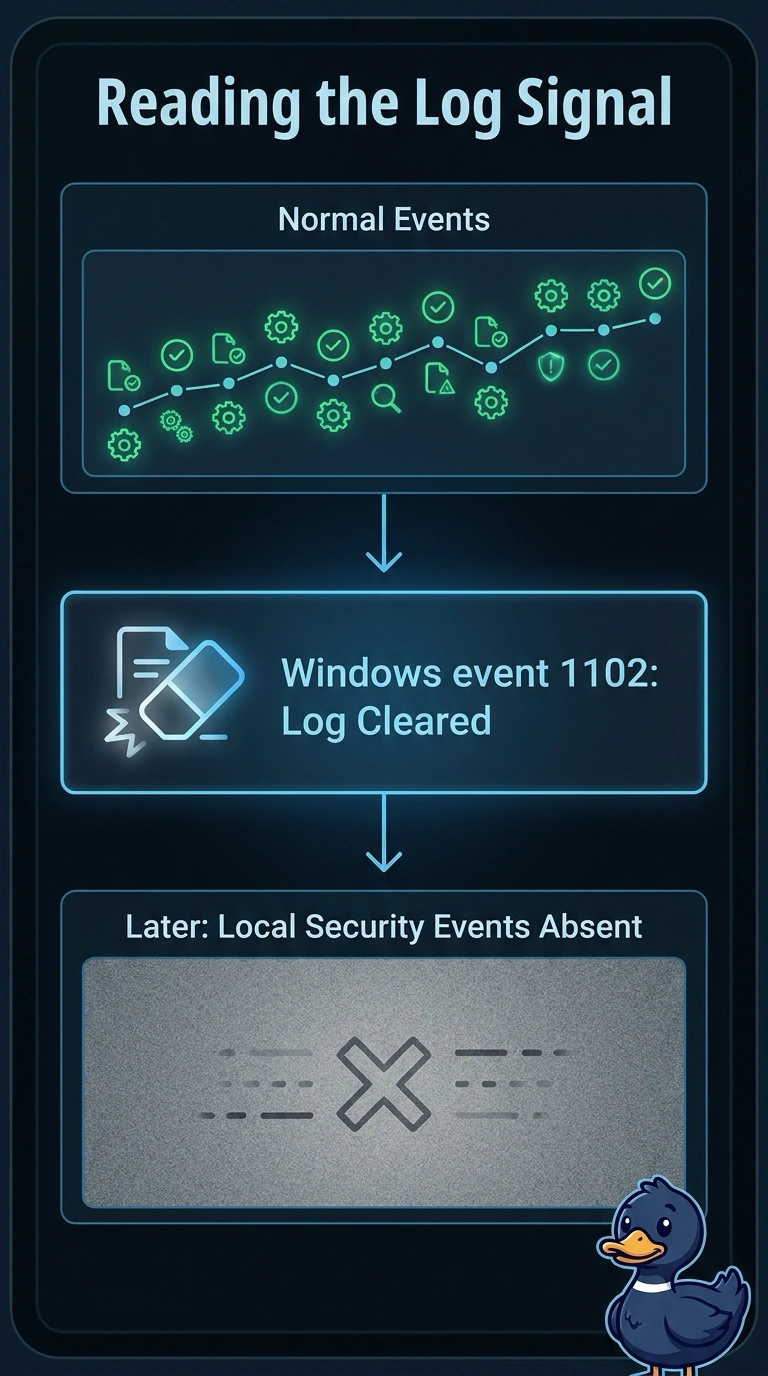
Short Explanation
Someone tore the pages out of the notebook and then the notebook stays blank. You are looking at a cleared security log followed by silence from that PC. The trap is treating event 1102 as proof the disk was encrypted or that a logon succeeded.
Full Explanation
Windows event 1102 records that the security audit log was cleared. When that event is the last security event the SIEM receives from the warehouse PC, the supported reading is that the log was cleared and later local security events are missing. That is "The security audit log was cleared, and later local security events from that PC are absent". "The warehouse PC disk filled with ransomware, and that alone stopped the security log" adds an encryption payload the event does not describe; a cleared log is not the definition of ransomware. "A user completed a successful logon, the normal authentication success event on that PC" would be a successful logon record, and 1102 is the clear event rather than a logon. "Installed patches finished cleanly, and the host stopped sending security events to the SIEM" treats a maintenance outcome as the meaning of 1102, but a patch install is not what that event records. Exam caveat: an administrator can clear the log during approved maintenance, so 1102 is not by itself proof of ransomware or of a specific attacker. Operational check: identify the account associated with the clear, look for a change ticket, and confirm whether security auditing on that PC is still enabled and forwarding.