
At a university, a process on a lab PC begins accepting inbound connections from other hosts in the lab. Which control on that PC blocks those inbound connections?
Select an answer to reveal the explanation.
Short Explanation
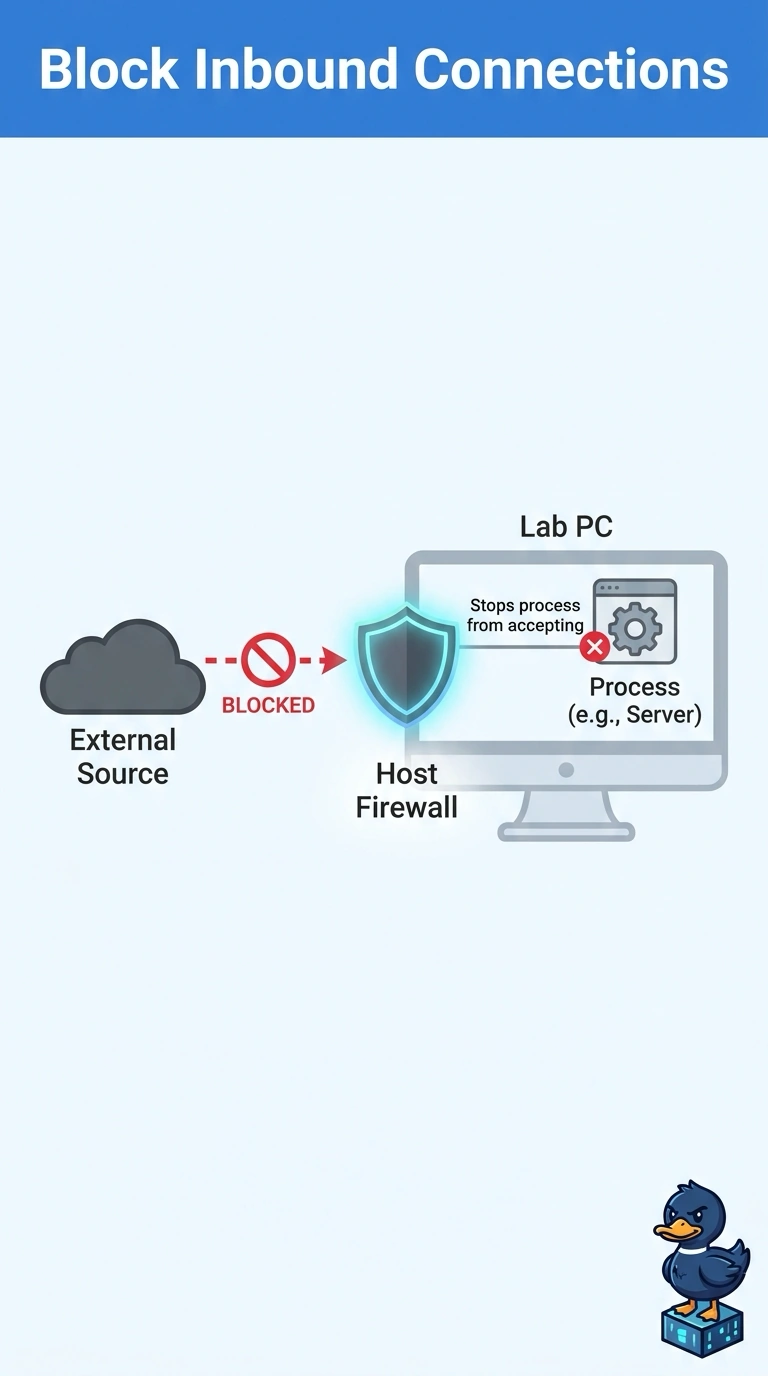
The bolt on the lab PC is what refuses new visitors, not a note that someone rattled the handle. You need the control that stops a process from accepting inbound connections, and that control is the host firewall. The trap is quarantining a file that is not listening, a detection log that does not block, or a sandbox that is not on the PC.
Full Explanation
The host firewall on the lab PC, stopping a process from accepting new inbound connections is the control that blocks the inbound connections. A host firewall on the lab PC can stop a process from accepting new inbound connections. The process started accepting connections from other lab hosts, and the control on that PC which refuses those connections is the host firewall. Antivirus quarantine of a file that is not listening and is not holding an open socket on the PC quarantines a file that is not listening and is not holding a socket. It does not close a listening socket that belongs to some other process, and that file is not the listener. A host intrusion detection log that only records a process injection and does not block the new port records a process injection. A detection log is evidence. The record described here does not block the new port, so writing the injection down does not stop the process from accepting connections. A sandbox that detonates files away from the lab PC and does not enforce any policy on that PC detonates files somewhere other than the lab PC and does not enforce policy on that PC. A sandbox that is not on the PC cannot block a socket the PC has opened. Exam caveat: a host detection log can describe an injection perfectly and still not be the control that blocks a port. Operational check: on the lab PC, confirm a host firewall rule denies new inbound connections to that process, and confirm the detection log did not perform the deny.