
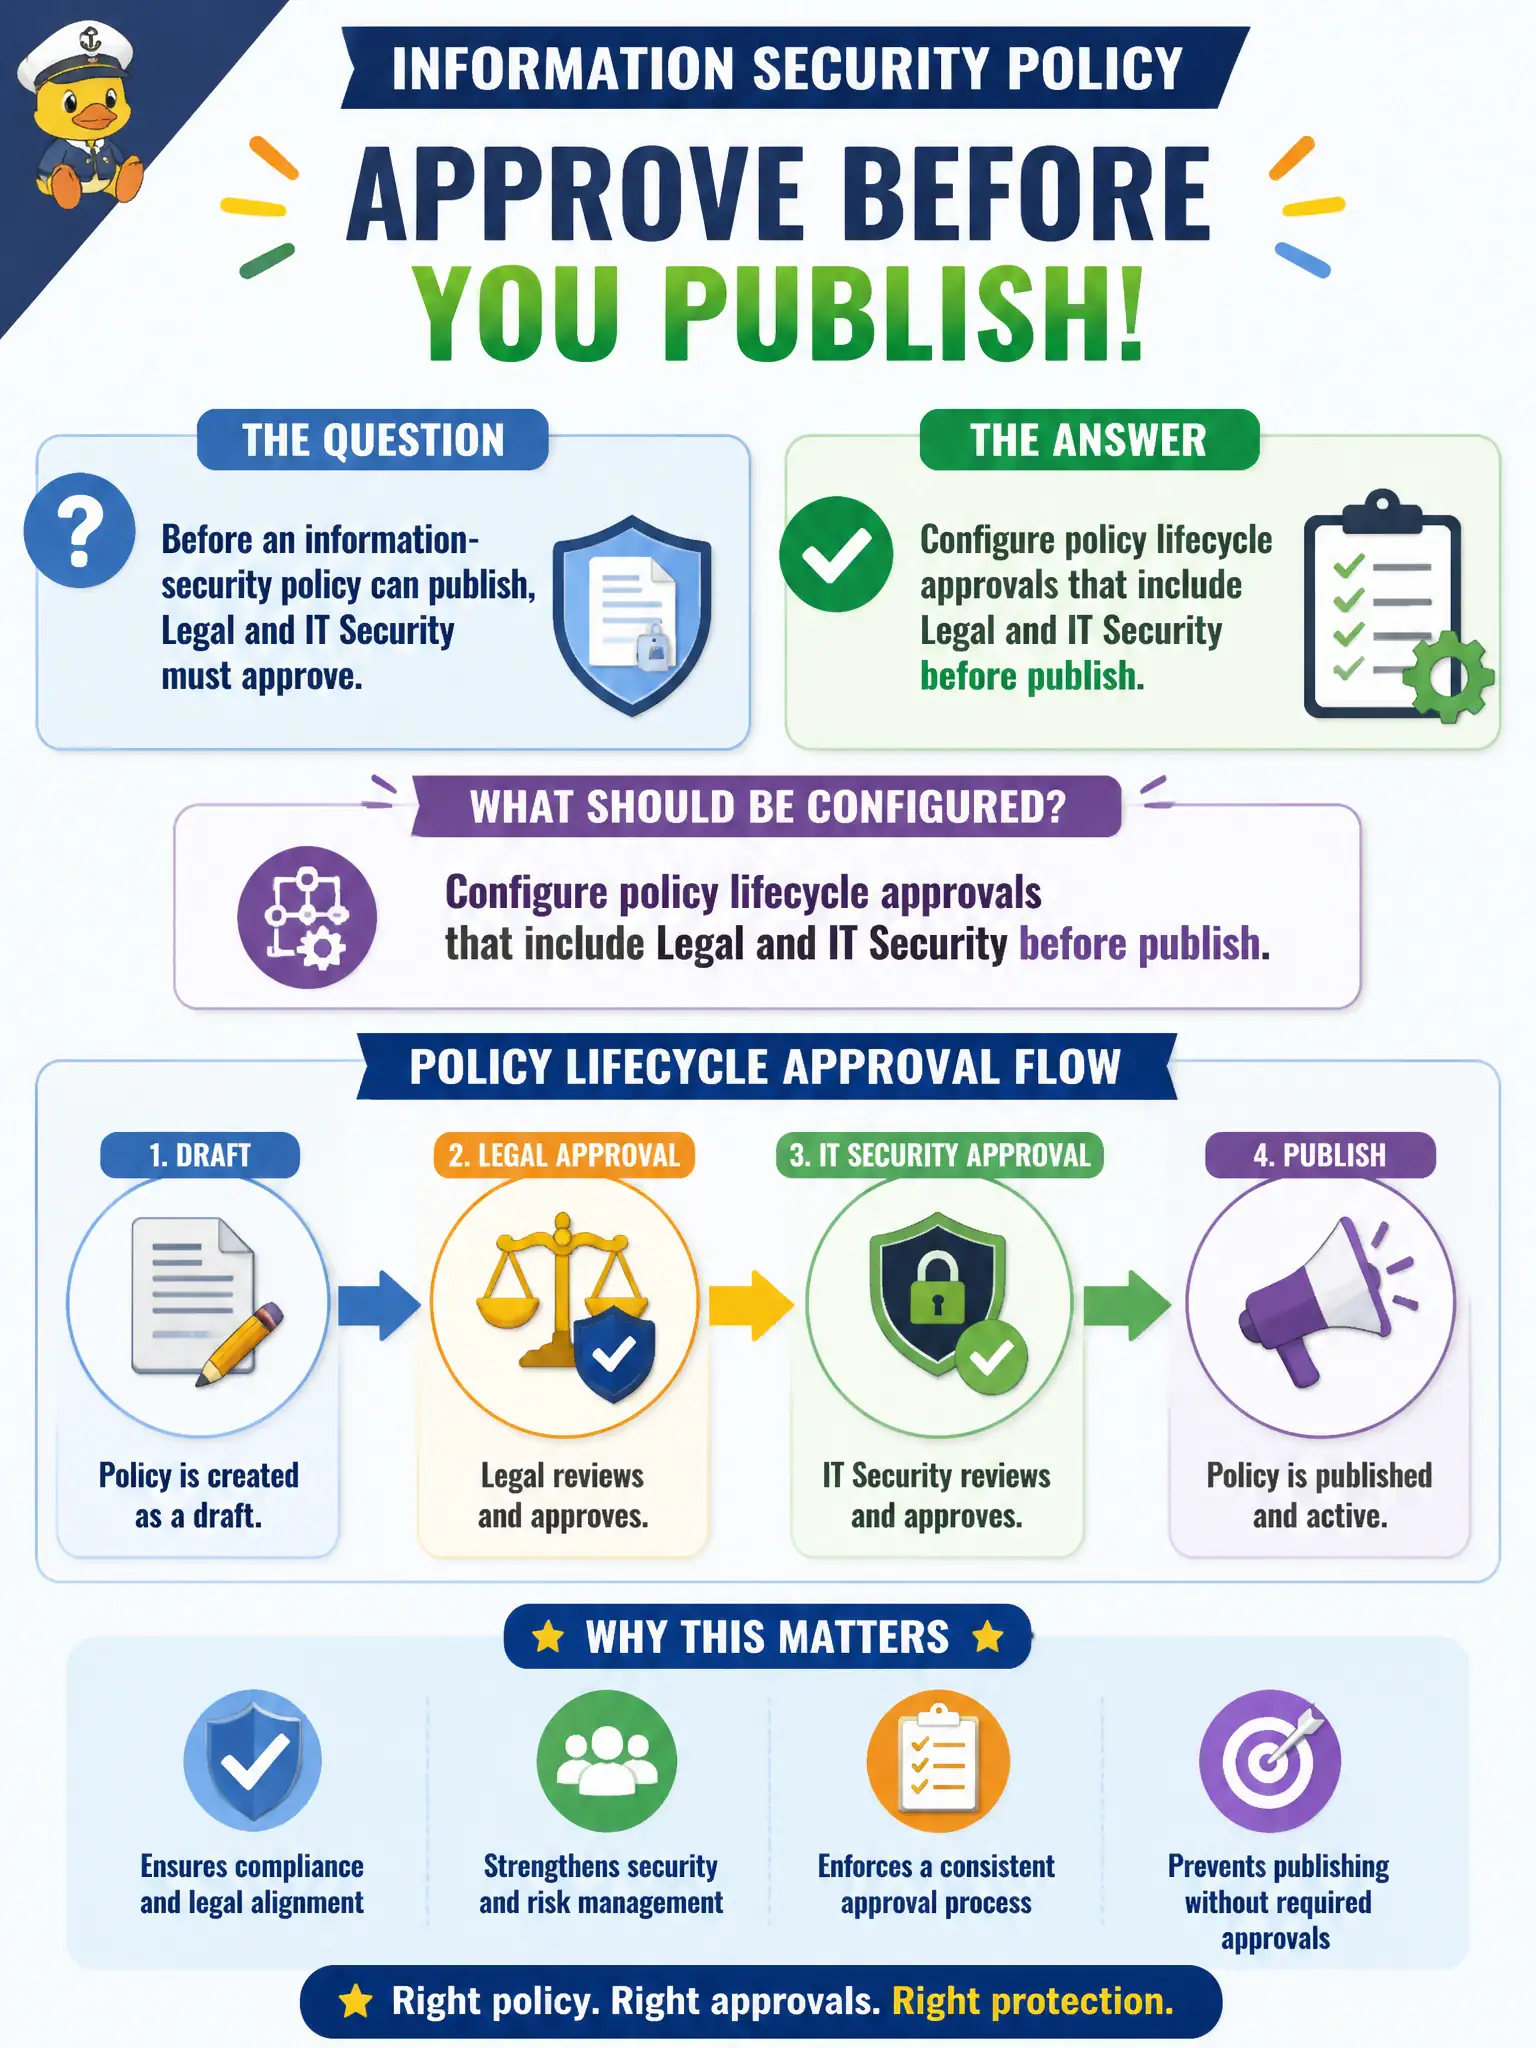
Before an information-security policy can publish, Legal and IT Security must approve. What should be configured?
Select an answer to reveal the explanation.
Short Explanation
Publishing a policy without Legal and Security is like shipping code without review. Put both in the lifecycle approval path before publish. Optional comments, peer-only review, or approve-after-it-is-live are backwards.
Full Explanation
Policy lifecycle workflows gate publication behind designated approvers before a policy becomes effective. For an information-security policy that Legal and IT Security must accept, configuring lifecycle approvals that include both groups ensures civic policy text is reviewed for legal and security fitness prior to publish. Allowing authors to publish immediately with an optional comment fails by concept because optional comments are not controlled approval and allow unvetted policy to bind the organization. Requiring only a peer author review and skipping Legal and Security fails by concept because peer review does not substitute for the mandated stakeholder gates those civic programs require. Publishing first and collecting approvals in email after the policy is live fails by concept because post-publication email approvals invert the lifecycle and leave a window where an unapproved policy is already authoritative. Exam caveat: CIS-RC treats policy publish as a gated lifecycle event, not a post-hoc email ritual. Operational check: configure Legal and IT Security on the policy approval path, attempt to publish a draft without their approval, and confirm publish is blocked until both approvals complete.