
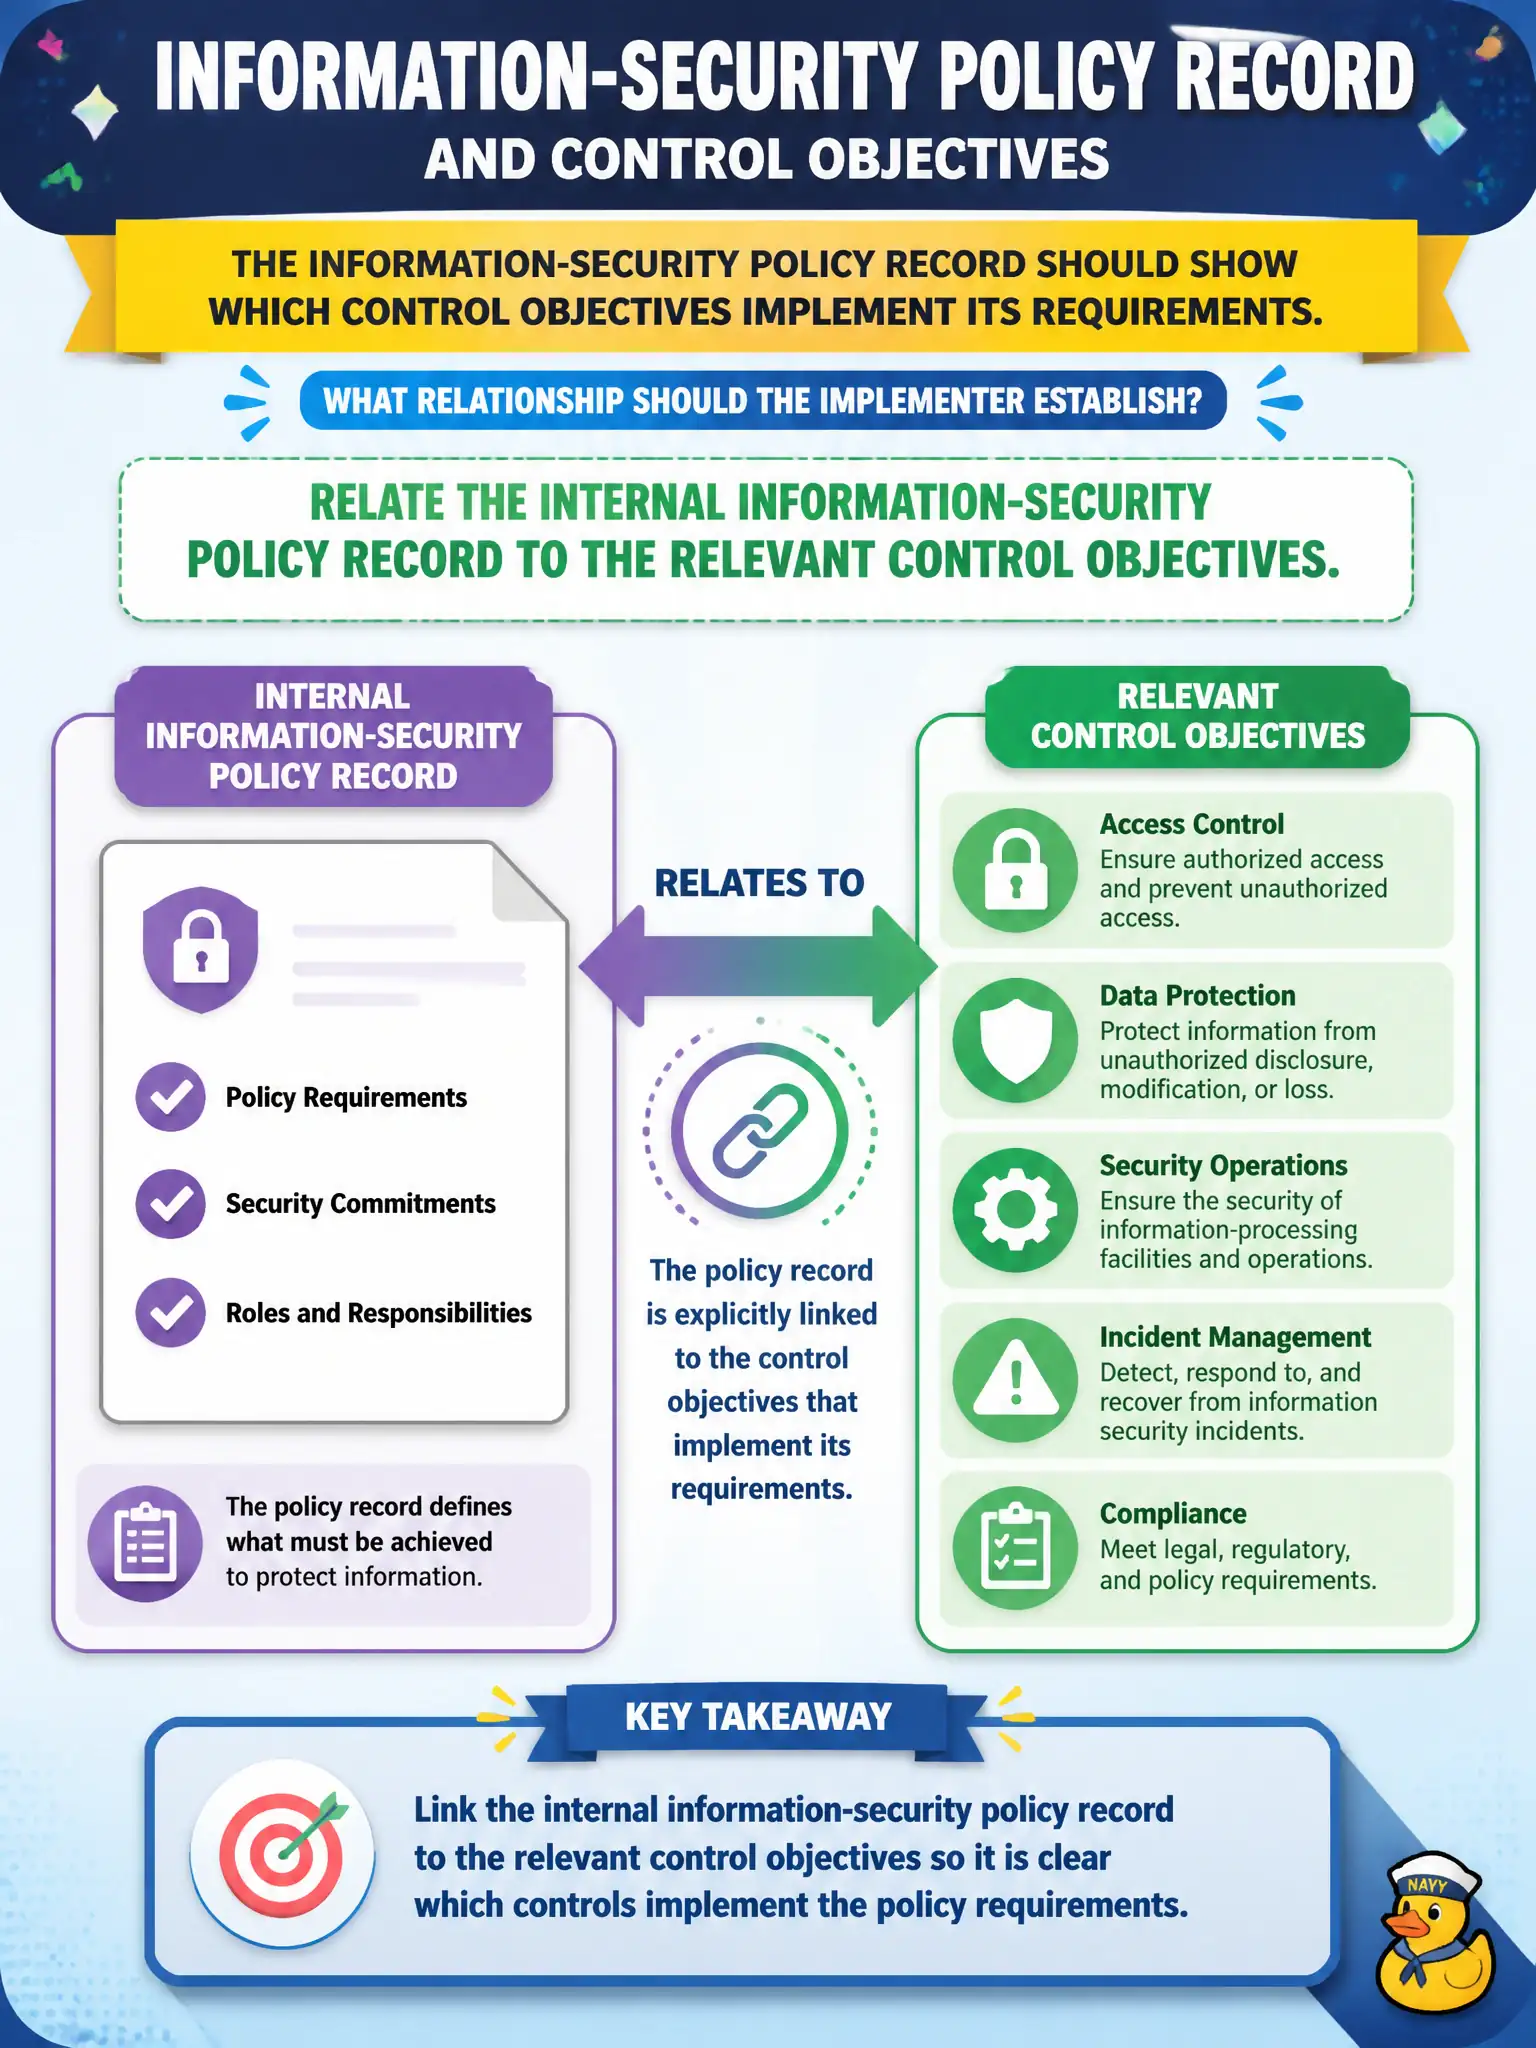
The information-security policy record should show which control objectives implement its requirements. What relationship should the implementer establish?
Select an answer to reveal the explanation.
Short Explanation
Policies say what; control objectives say how you prove it. Link the info-sec policy to those objectives so the chain is obvious. PDFs on every entity, audit-only links, and orphaned URLs leave a gap in the middle.
Full Explanation
Policy and Compliance maintains relationships from internal policy records to the control objectives that operationalize policy intent. Relating the information-security policy to relevant control objectives gives civic owners and examiners a navigable chain from written policy to how compliance is designed and tested. Replacing control objectives with cloned copies of the full policy PDF on every entity fails by concept because PDFs on entities do not create structured policy-to-objective traceability or reusable control design. Relating the policy only to audit engagement records and skipping control objectives fails by concept because audits assess; they do not substitute for the content chain that drives ongoing control generation. Storing the policy URL in a UI message while leaving control objectives unlinked fails by concept because a URL tip is not a first-class relationship examiners can report against. Exam caveat: CIS-RC expects policy records to relate to control objectives as the bridge to operational controls. Operational check: open the information-security policy record, relate it to the relevant control objectives, and verify a related-list or traceability view shows those objectives under the policy.