
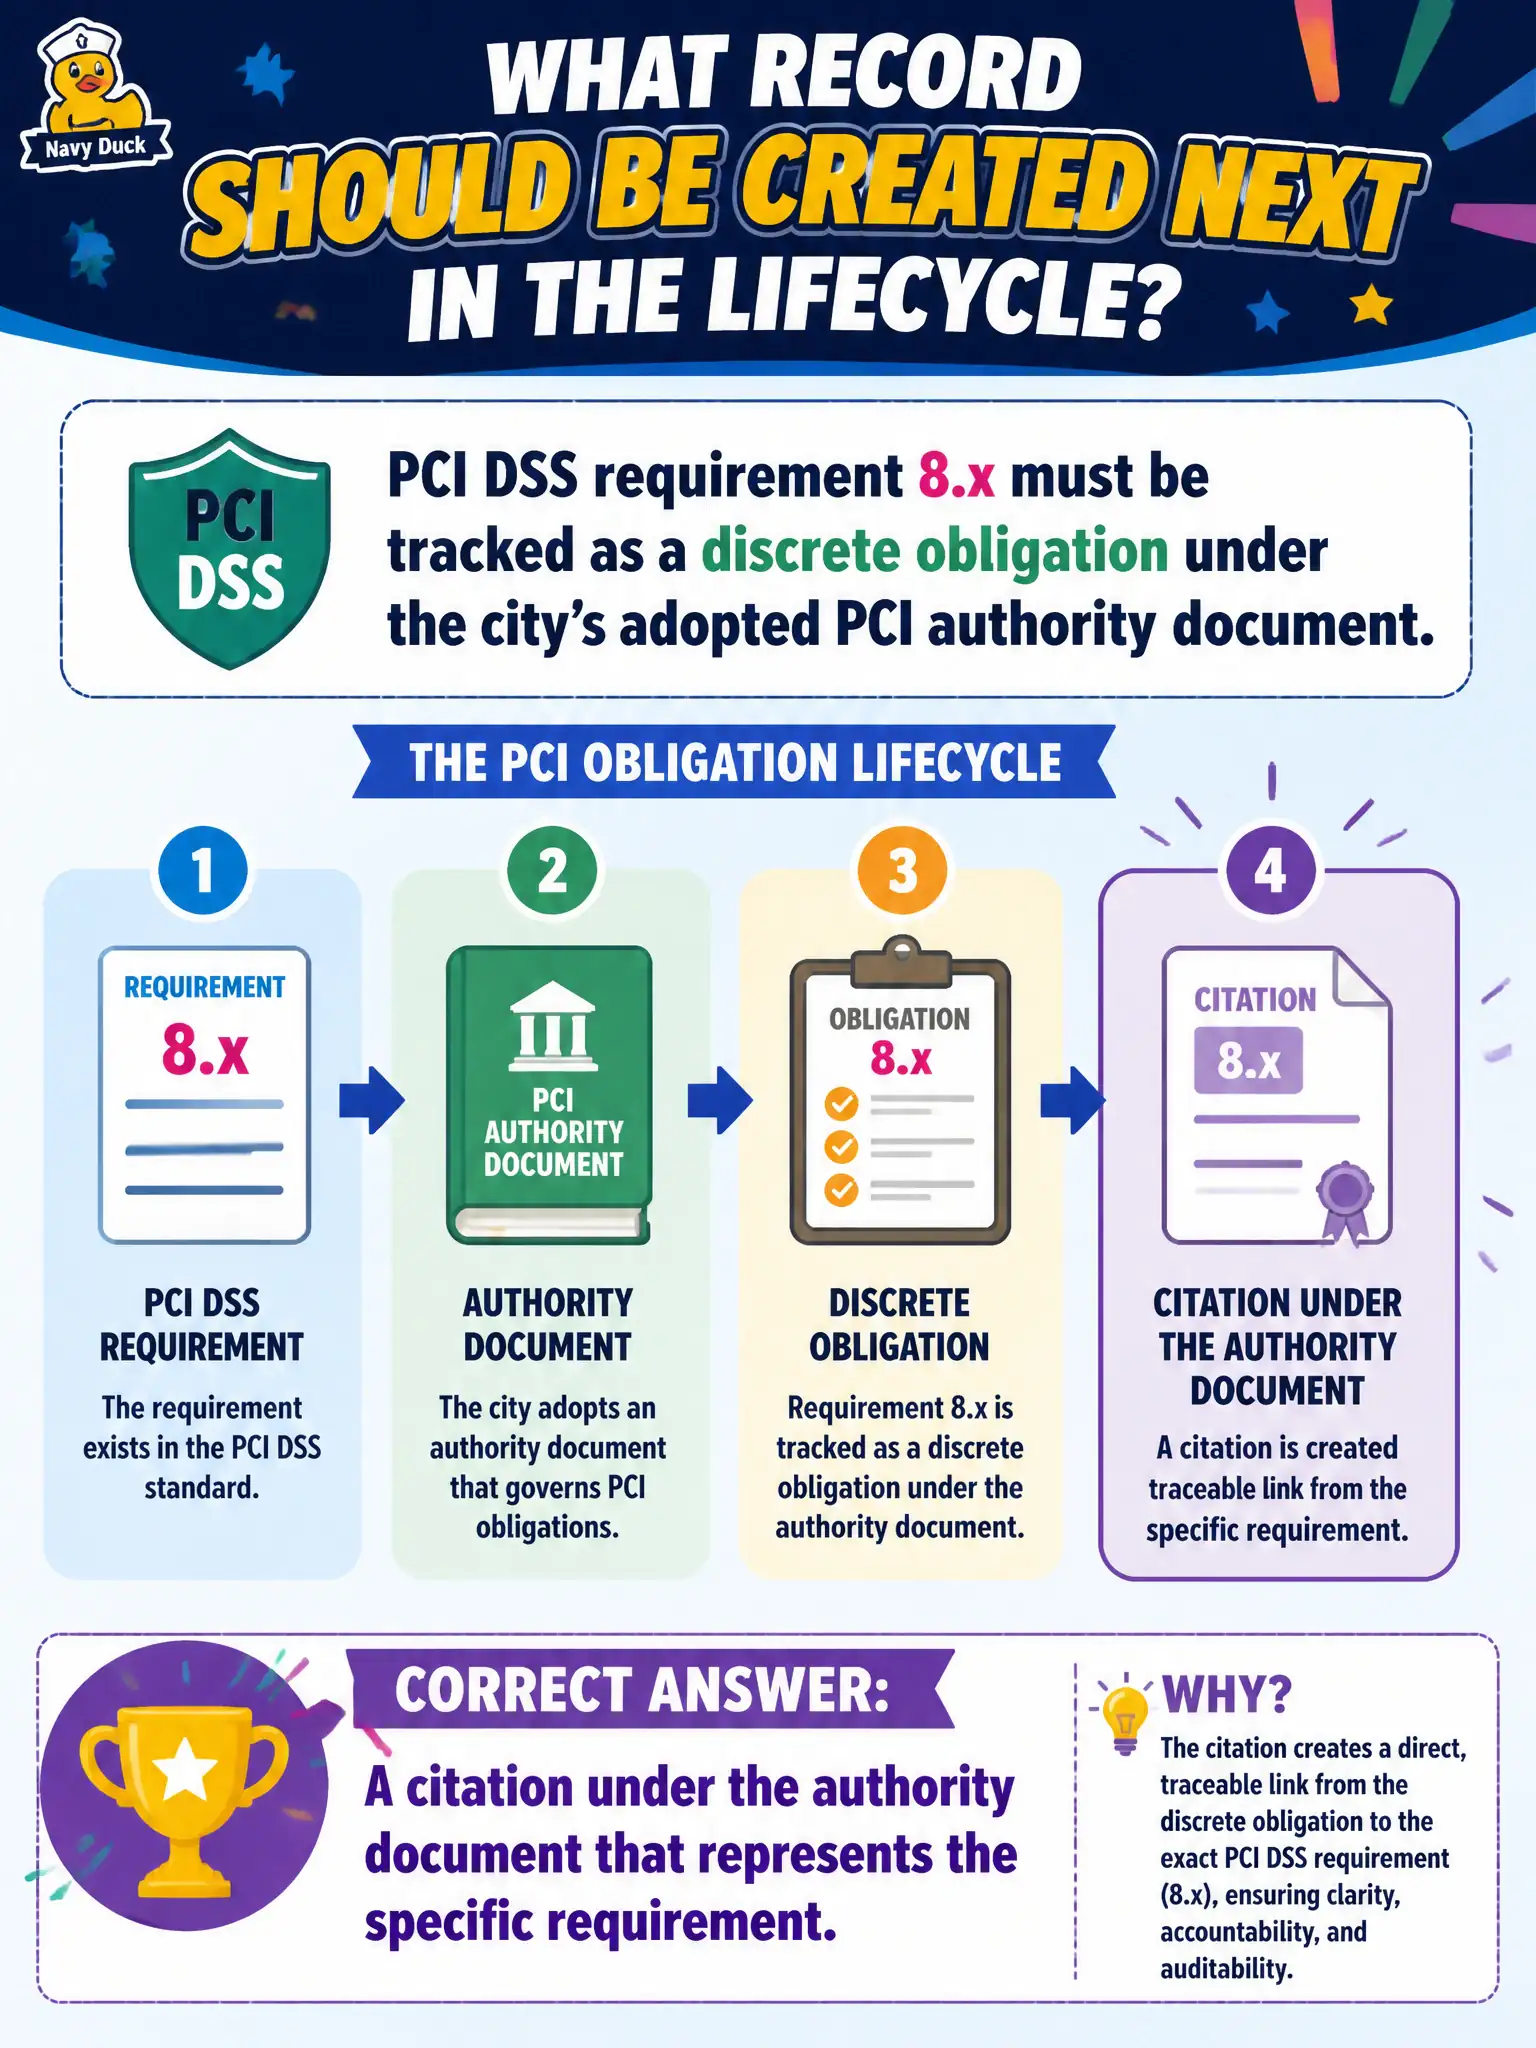
PCI DSS requirement 8.x must be tracked as a discrete obligation under the city’s adopted PCI authority document. Which record should be created next in the lifecycle?
Select an answer to reveal the explanation.
Short Explanation
Think of the authority document as the statute book and the citation as the exact section number you care about. For PCI 8.x, create that citation under the parent mandate. Then you can map objectives without losing which requirement you meant.
Full Explanation
Citations are the discrete obligation records under an authority document. When PCI DSS requirement 8.x must be tracked under the city's adopted PCI authority document, the next lifecycle record is a citation that represents that specific requirement. Creating a new CMDB CI class named after the PCI requirement number confuses inventory classification with regulatory obligation tracking and pollutes the CMDB. Opening a policy exception that permanently waives the requirement before it is even recorded inverts the process and hides the mandate from the library. Launching an audit engagement with no citation or control objective linkage does not establish the content-chain record needed for ongoing compliance operations. Exam caveat: citations enable mapping to control objectives—they are not themselves the generated controls owners test or attest. Operational check: add the 8.x citation under the PCI authority document, map it to the appropriate control objective, confirm lineage reporting from citation to control on a payment-related entity, and brief cardholder-data stakeholders on where the obligation lives in IRM. Verify examiners can trace the civic control back to the citation during readiness reviews and retain mapping screenshots in the evidence binder.