
A security architect proposes storing all control-test evidence only in email threads. What should the IRM implementer recommend instead?
Select an answer to reveal the explanation.
Short Explanation
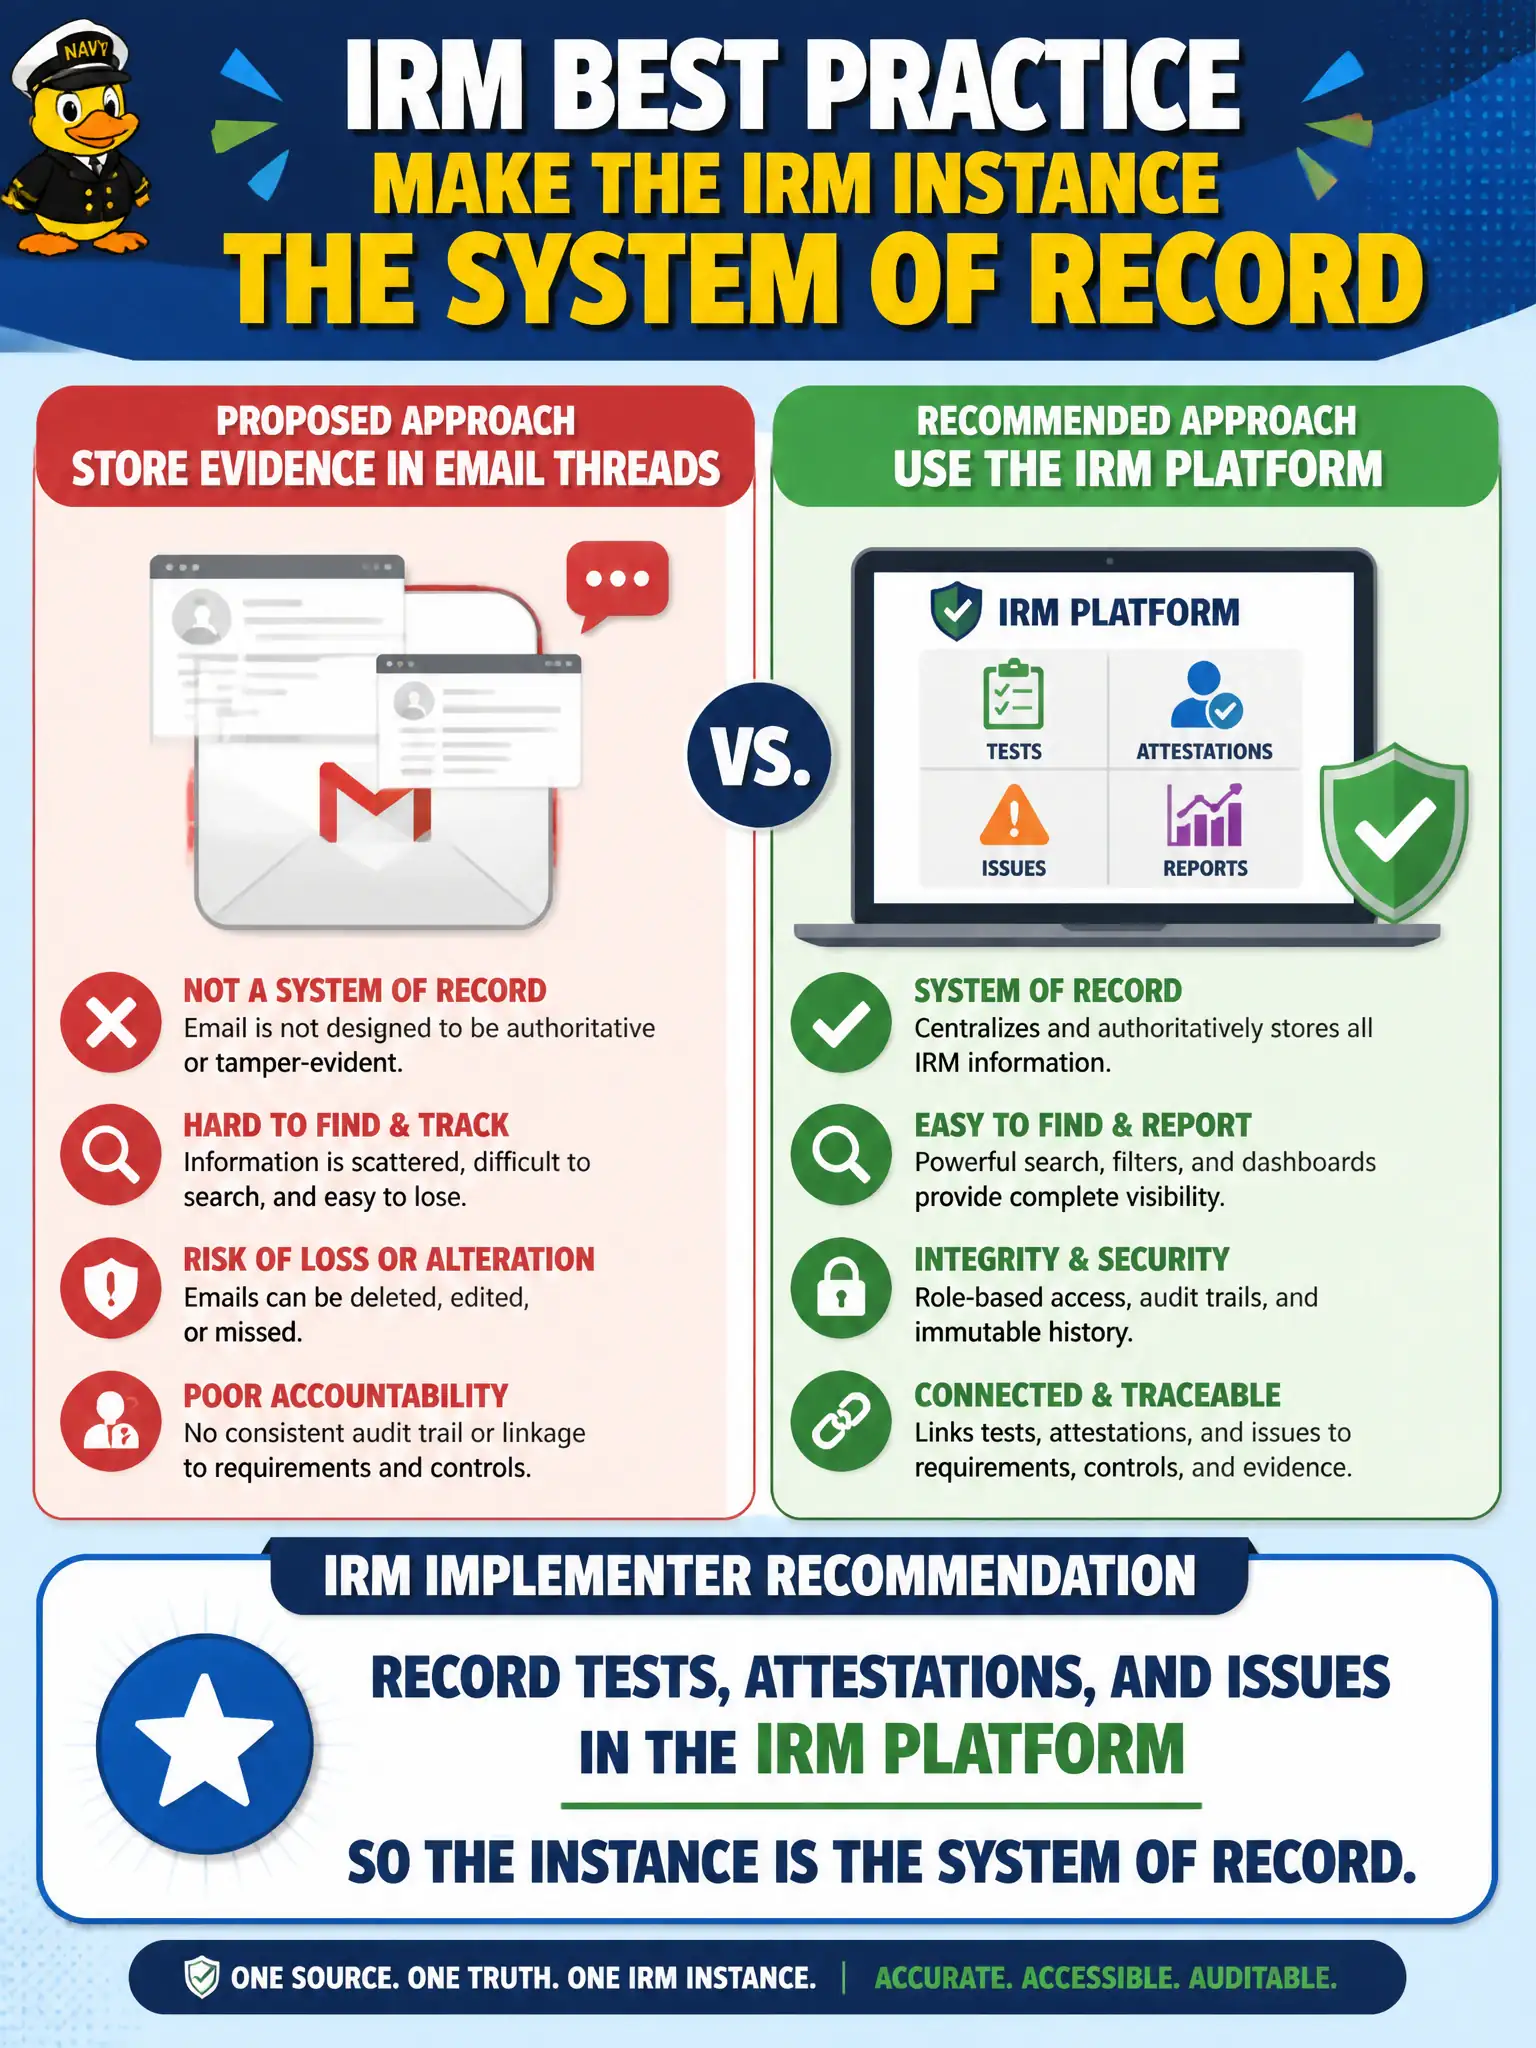
Email is a hallway full of sticky notes—easy to lose and hard to audit. IRM wants the test results, attestations, and issues sitting in the platform where owners, dates, and history stick. That is how a regulated org proves what was checked and when.
Full Explanation
Control tests, attestations, and issues should be recorded in the IRM platform so the instance is the system of record. A security architect proposing email threads as the only evidence store leaves regulated cities with fragmented, hard-to-defend proof that lacks durable ownership, workflow, and history tied to entities and controls. IRM is designed for those GRC artifacts so auditors and managers can retrieve what was checked, by whom, and when. Email may notify people, but it should not be the compliance ledger. Keeping email as the only system of record and pasting screenshots into SIR playbooks still leaves evidence outside Risk and Compliance structures. Moving evidence exclusively into personal OneDrive folders owned by each analyst creates private silos that vanish with staff turnover. Disabling attestations and relying on hallway conversations documented in ITSM incidents abandons structured control testing. Exam caveat: platform-of-record discipline for tests and attestations is a recurring implementation theme on CIS-RC. Operational check for the implementer: require one control test and one attestation to be completed in IRM for a pilot entity, prohibit email-only evidence for that pilot, and sample the records for owner, timestamp, and related control links before expanding the program.