
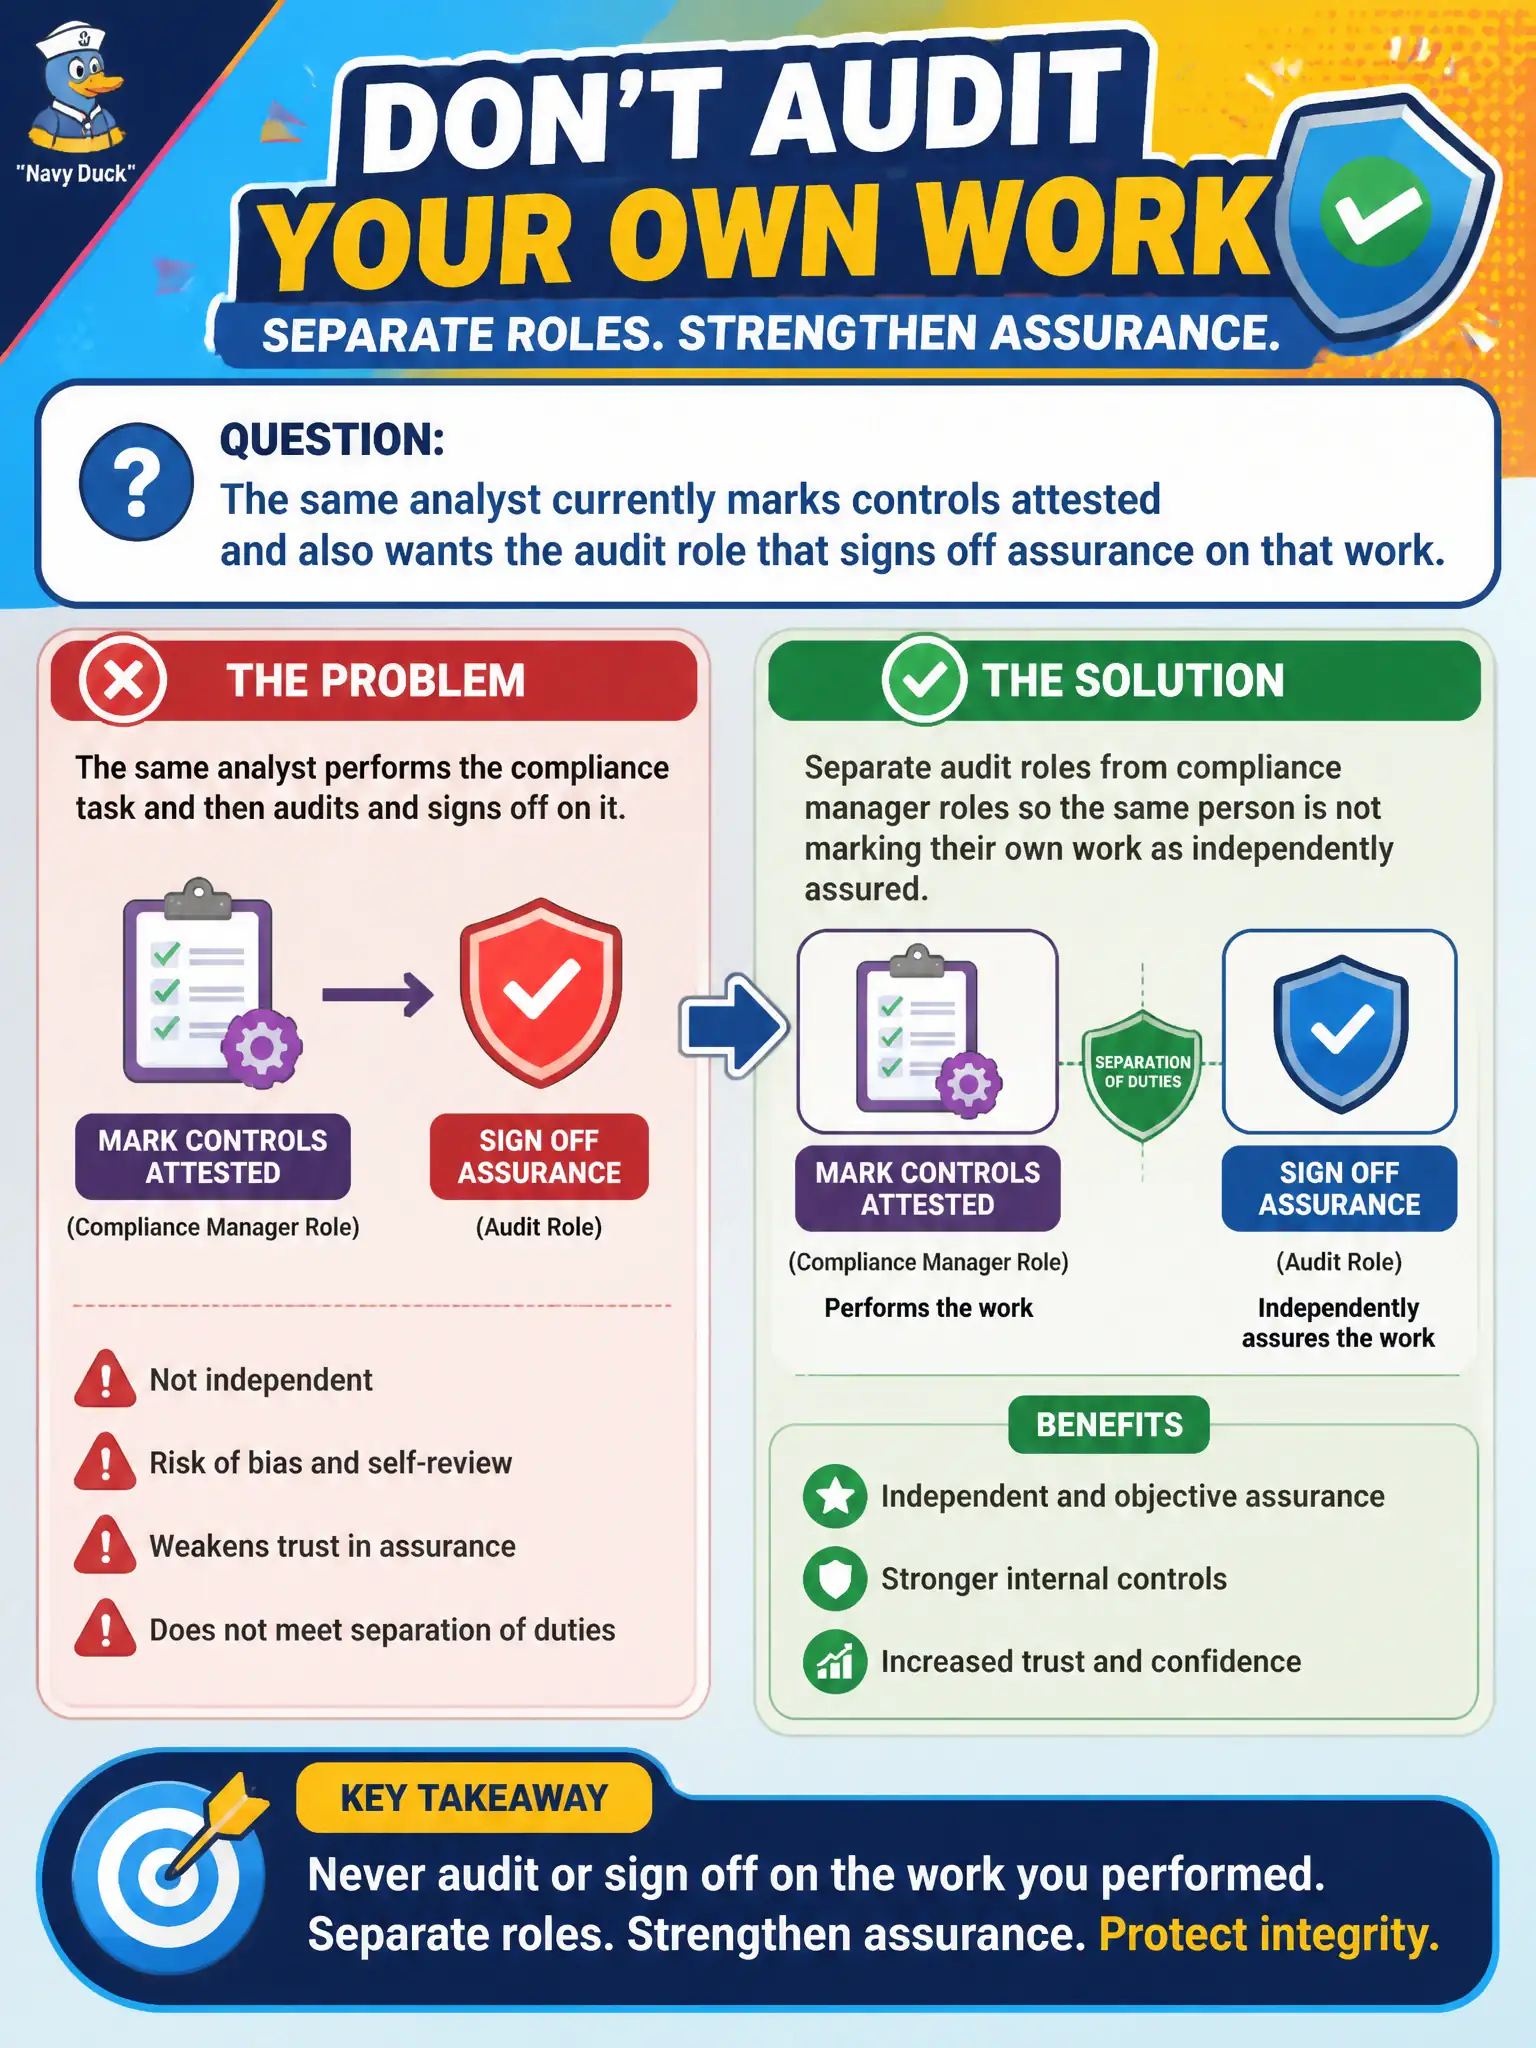
The same analyst currently marks controls attested and also wants the audit role that signs off assurance on that work. What should the implementer enforce?
Select an answer to reveal the explanation.
Short Explanation
You wouldn’t let the same person grade their own homework and call it an external review. Keep audit roles separate from compliance operator roles so assurance stays independent. One super-role is how segregation dies.
Full Explanation
When the same analyst marks controls attested and also wants the audit role that signs off assurance on that work, the implementer must separate audit roles from compliance manager roles so the person is not marking their own work as independently assured. Segregation of duties is how civic GRC prevents homework graded by the author from being labeled external review. Role design enforces the three lines even when staffing is thin.
Combining compliance manager and auditor into one super-role to reduce license cost intentionally destroys segregation. Requiring only ITSM fulfiller roles for both jobs misuses ITSM personas for GRC assurance duties. Disabling Audit Management and relying on policy acknowledgment alone retires independent assurance in favor of handbook clicks.
Exam caveat: keep audit roles separate from compliance operator/attestor roles; license convenience is not an accepted reason to merge them on CIS-RC.
Operational check: review role assignments for dual-hatted analysts; remove audit assurance rights on controls they attest; implement compensating review if staffing forces temporary dual duty; never deploy a combined compliance+auditor super-role as standard design.