
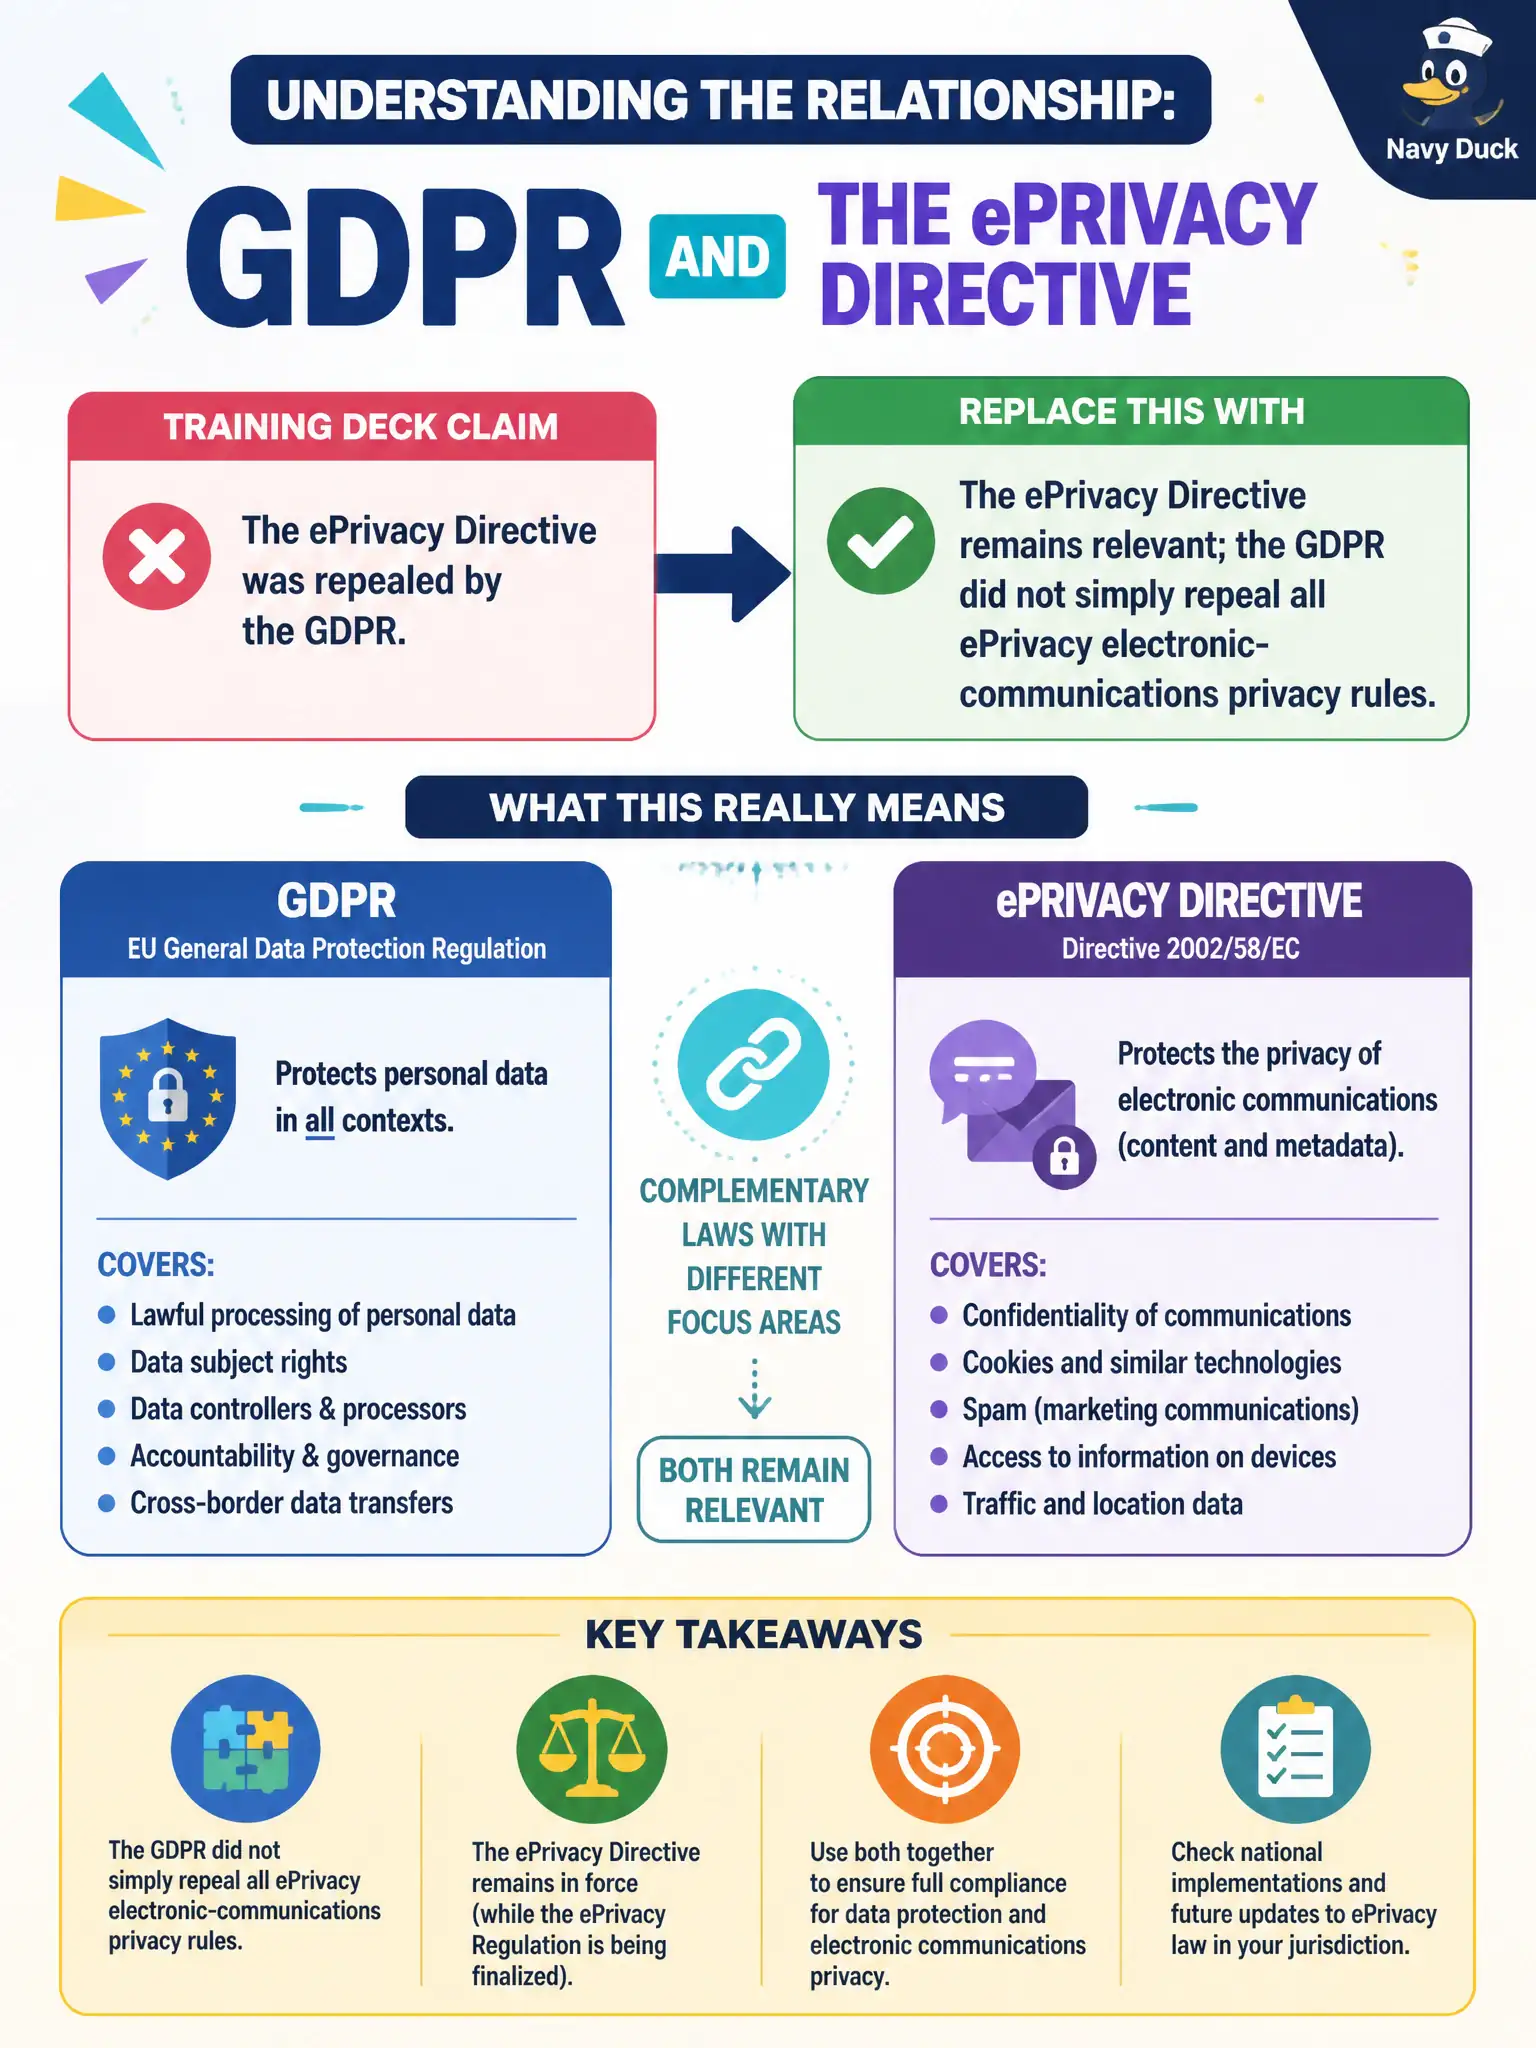
A training deck says the ePrivacy Directive was repealed by the GDPR. What should replace that claim?
Select an answer to reveal the explanation.
Short Explanation
Someone slid a fake “repealed” stamp on ePrivacy. Nope — those electronic-communications privacy rules still matter beside the GDPR. Update the deck before telecoms and marketing teams learn the wrong story.
Full Explanation
The ePrivacy Directive remains relevant; the GDPR did not simply repeal all ePrivacy electronic-communications privacy rules. Training decks that announce full repeal mis-teach Domain I related legislation and cause teams to miss confidentiality-of-communications and terminal-equipment issues. ePrivacy rules were not converted into US state privacy acts. Trainers did not invent ePrivacy after 2018. The GDPR did not absorb ePrivacy into a single article on postal marketing only. Practitioners must assess both frameworks where electronic communications, cookies, or similar overlays are in play, alongside general personal-data duties. Exam caveat: repeal-by-GDPR claims about ePrivacy are almost always wrong on CIPP/E items. Operational check: revise any municipal privacy training slide that says GDPR replaced ePrivacy; replace it with a coexistence diagram and a checklist item for cookie/terminal-equipment compliance owners. For municipal teams, keep a one-page decision note that states the governing instrument, why competing labels fail, and what evidence would change the conclusion. Document the decision trail so auditors can see how the civic team matched facts to the correct legal category rather than to a slogan.