
A complainant asks the EDPS to impose an administrative fine on a private German GmbH for GDPR infringements. Why is that request misdirected?
Select an answer to reveal the explanation.
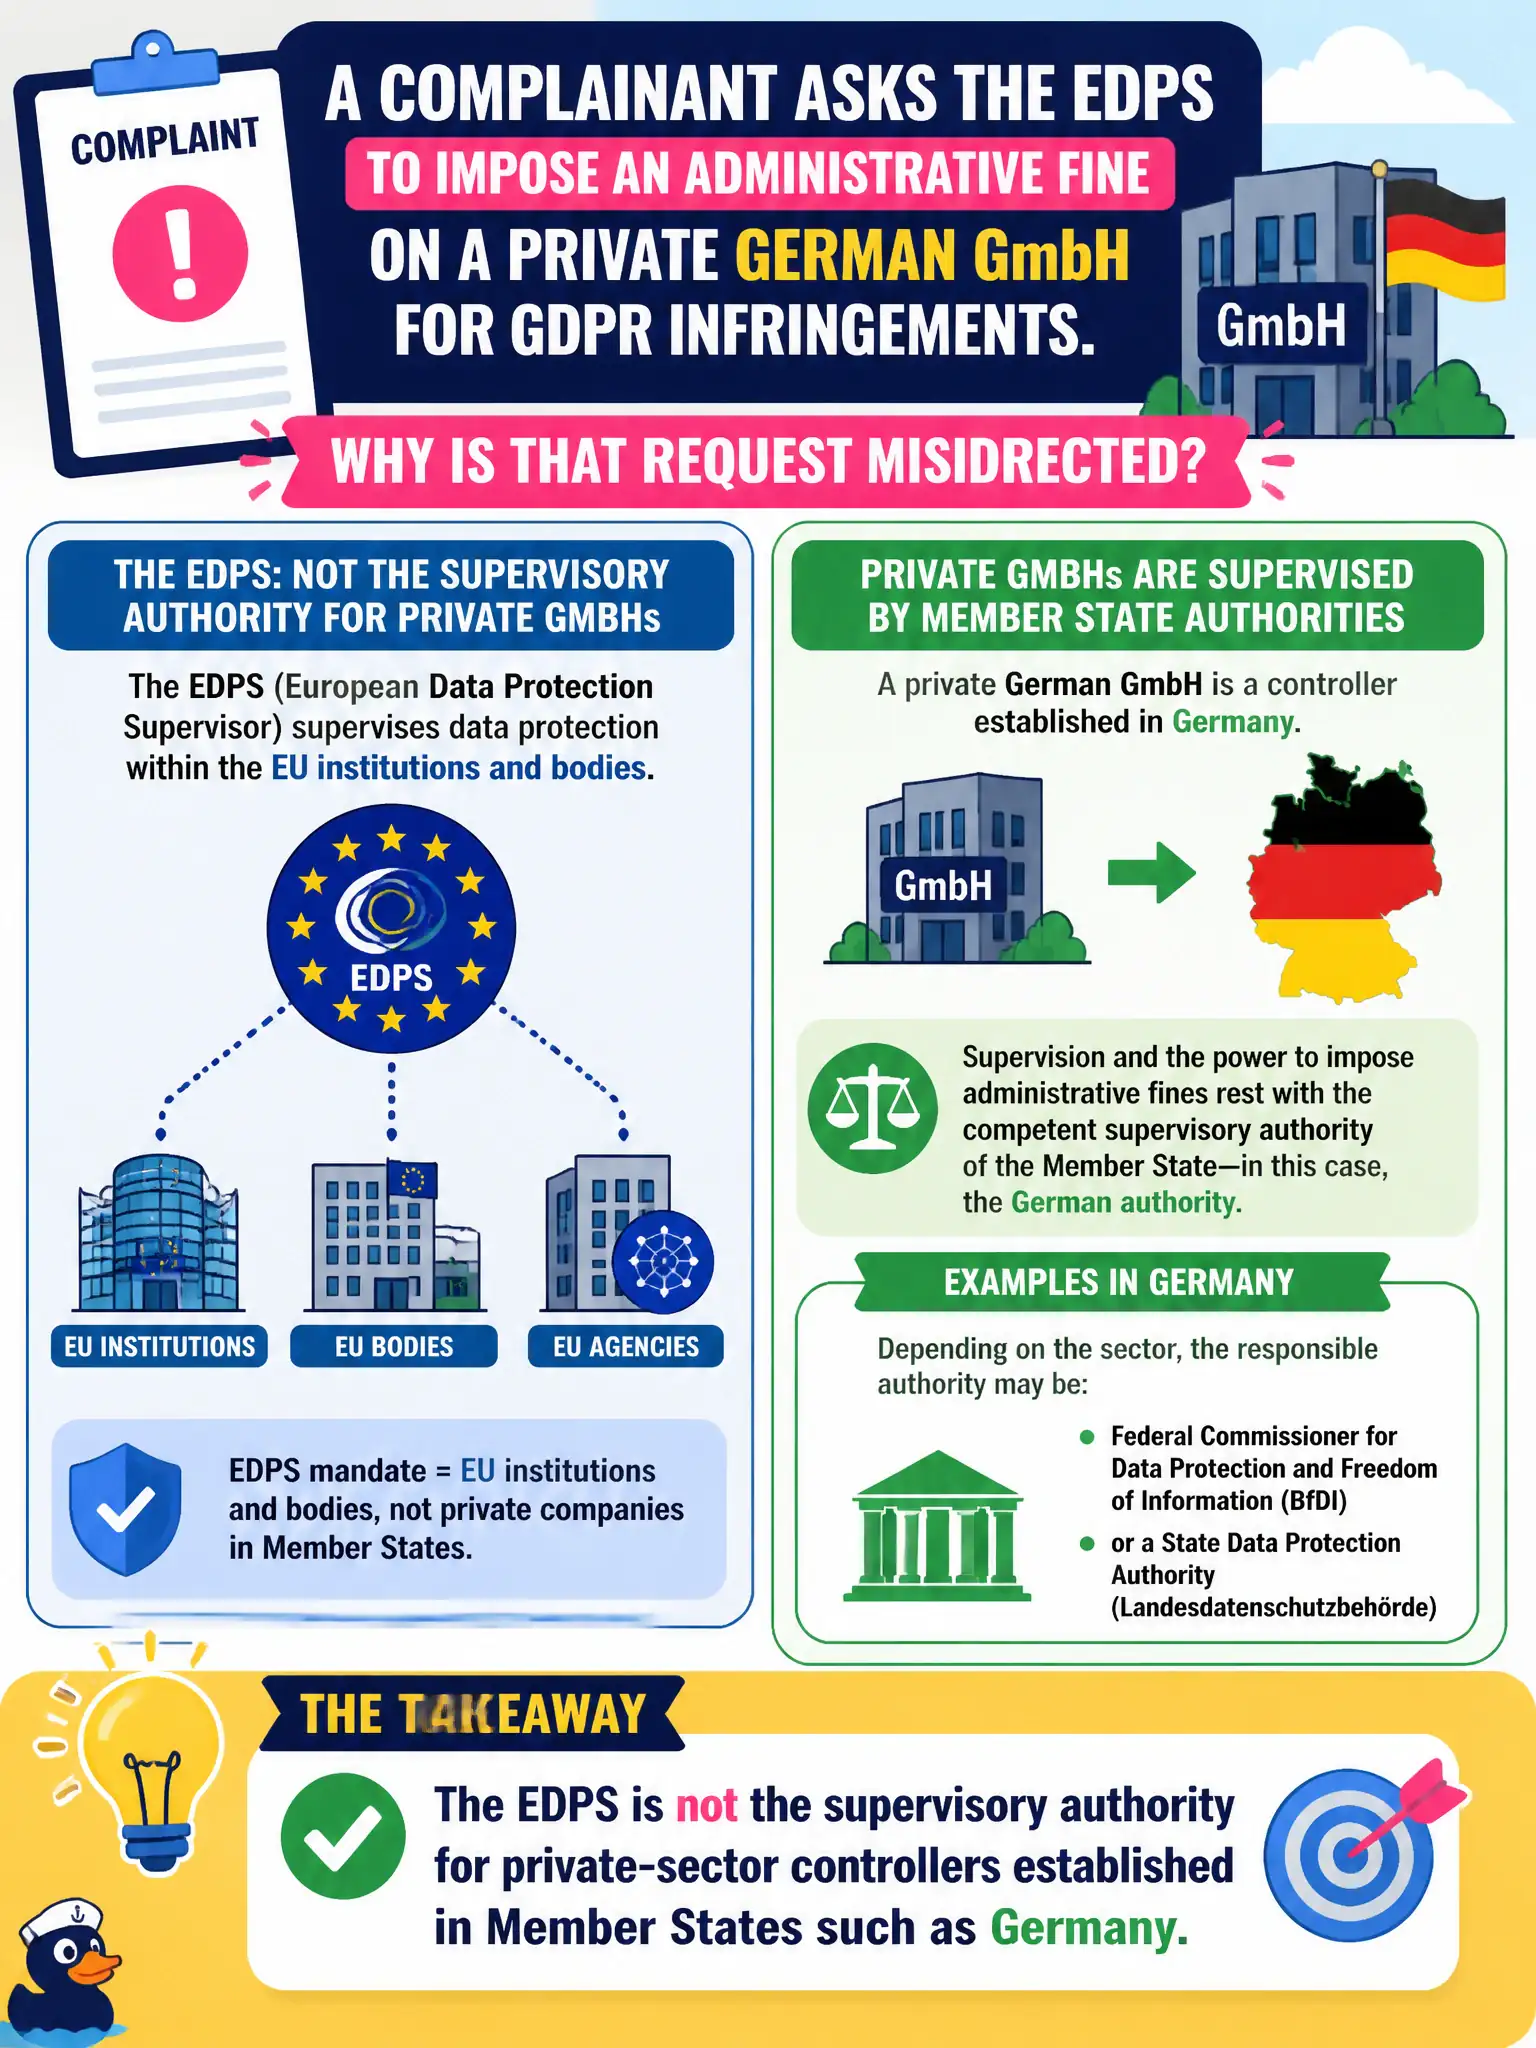
Short Explanation
Wrong inbox: the EDPS is the privacy watchdog for EU institutions, not for a private German company. That GmbH sits under Germany's supervisory authority (and GDPR fining rules)—not the EDPS desk.
Full Explanation
Asking the EDPS to impose an administrative fine on a private German GmbH is misdirected because the EDPS is not the supervisory authority for private-sector controllers established in Member States such as Germany. Civic complainants must reach the competent national SA (and the OSS lead where cross-border rules apply); the EDPS watches Union institutions and bodies, not ordinary private GmbHs. Claiming private companies can never receive administrative fines under any European law fails—Article 83 clearly contemplates fines on controllers and processors. Saying only US state attorneys general may fine EU companies processing EU data fails by exporting enforcement to the wrong continent and the wrong institutions. Asserting German GmbHs are exempt from the GDPR if they use English privacy notices fails: the language of a notice does not create an exemption from material or territorial scope. Exam caveat: institutional competence is separate from fining tiers—once the correct national SA acts, Article 83 factors and caps still apply to the undertaking. Operational check: route private-sector complaints to the competent Member State SA; reserve EDPS channels for Union-institution processing; train public-facing intake so fine requests are not sent to the wrong supervisor.