
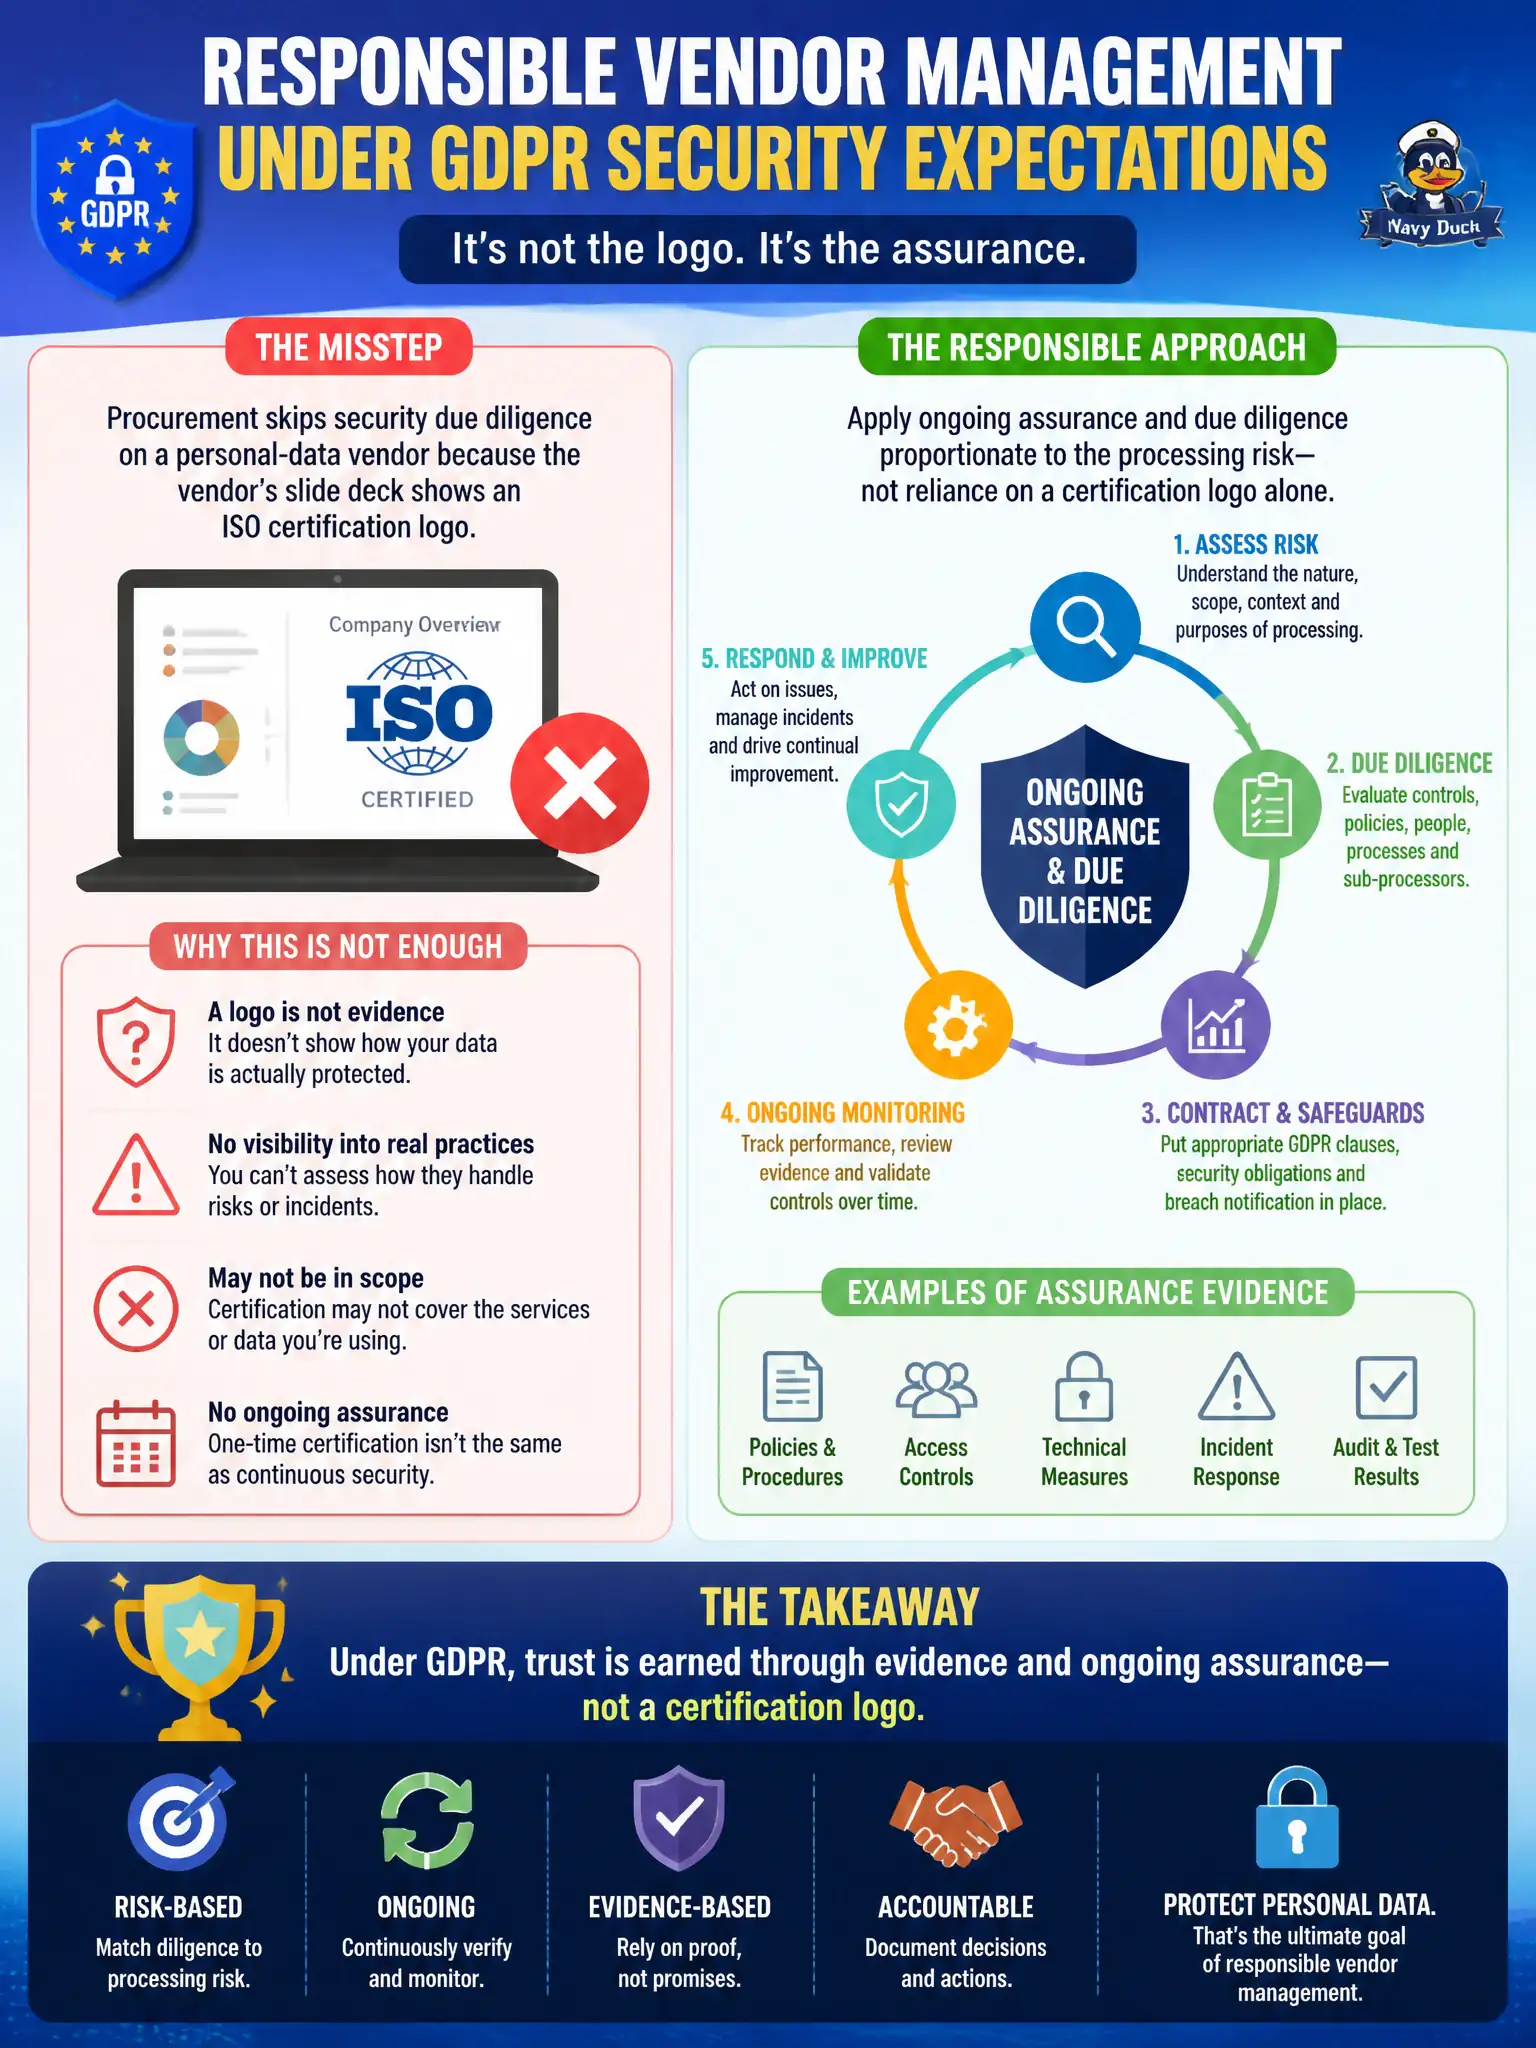
Procurement skips security due diligence on a personal-data vendor because the vendor’s slide deck shows an ISO certification logo. What does responsible vendor management under GDPR security expectations require?
Select an answer to reveal the explanation.
Short Explanation
A logo on a slide is not a force field. You still need proportionate checks—contracts, access, and follow-up—matched to how risky the processing is. Certification can help; it cannot replace responsible vendor management.
Full Explanation
Responsible vendor management under GDPR security expectations requires ongoing assurance and due diligence proportionate to processing risk, not reliance on a certification logo alone. Procurement that skips security review because an ISO mark appears on a slide deck fails Articles 28/32 themes of sufficient guarantees and appropriate measures. Accepting any ISO logo as a permanent waiver is wrong. Skipping DPAs and access reviews whenever marketing mentions certification is wrong. Treating vendor security as finished on signature day with no further monitoring is wrong. Exam caveat: certifications evidence, they do not replace risk-proportionate diligence. Operational check: require security questionnaires, Article 28 terms, and periodic assurance reviews scaled to the sensitivity of municipal personal data—even when the vendor displays ISO branding. For municipal teams, keep a one-page decision note that states the governing instrument, why competing labels fail, and what evidence would change the conclusion. Document the decision trail so auditors can see how the civic team matched facts to the correct legal category rather than to a slogan. Revisit the conclusion when facts, recipients, or processing purposes change, and record who approved the updated analysis.