
A new OWASP managed-rule pack is about to go live on the lock-booking site’s WAF. How should the security engineer introduce the policy mode?
Select an answer to reveal the explanation.
Short Explanation
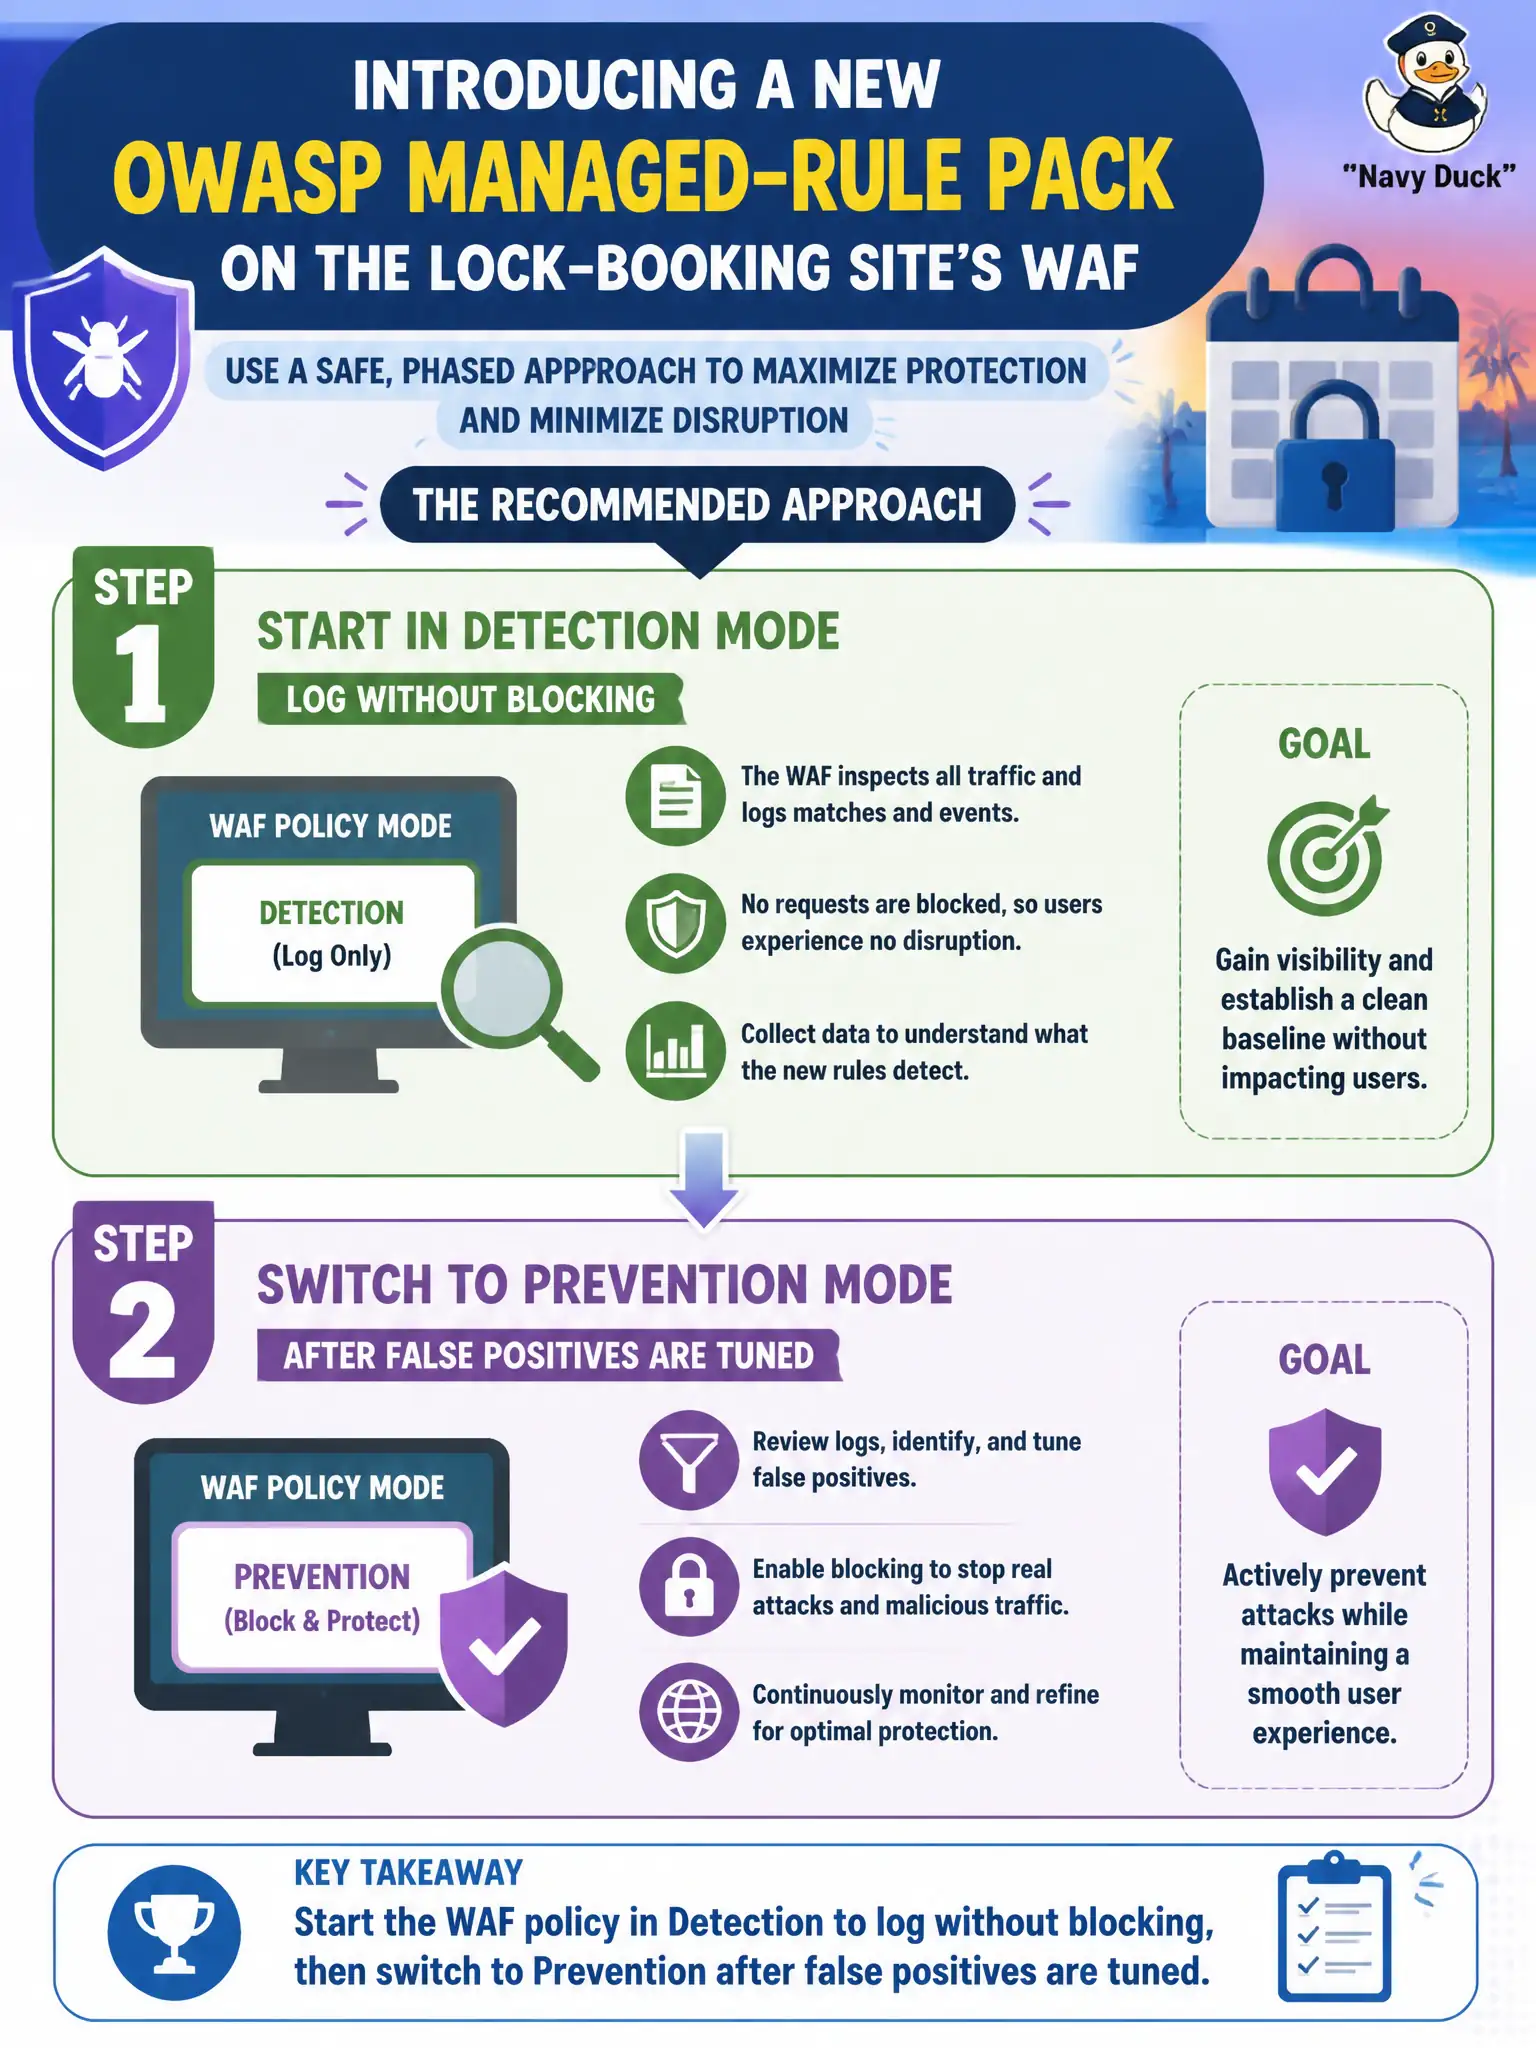
New managed rules? Start in Detection so you can see the false alarms, tune exclusions, then flip to Prevention. Going Prevention cold on day one is how you lock out real users.
Full Explanation
A new OWASP managed-rule pack on the lock-booking site’s WAF should start in Detection mode so the security engineer can log matches without blocking, tune exclusions for false positives, then switch to Prevention. That sequenced introduction protects booking availability for canal customers while still moving toward enforced blocking of attack traffic.
Enabling Prevention from day one with no exclusions or observation period fails by concept: untuned managed rules commonly block legitimate form posts and cause outages. Setting Azure Firewall threat intelligence to Alert only and calling that the WAF mode fails by concept: firewall threat intelligence is a different product control from WAF Detection versus Prevention. Disabling Microsoft Defender for Cloud Secure Score fails by concept: Secure Score is Domain 4 posture scoring and does not set WAF policy mode on Application Gateway or Front Door.
Exam caveat: Detection → tune → Prevention is the expected rollout; do not confuse Firewall threat-intelligence modes with WAF policy modes. Operational check: set the WAF policy to Detection, observe logs for the new OWASP pack on the lock-booking site, add justified exclusions, switch to Prevention, and verify legitimate bookings succeed while attack probes still block.