
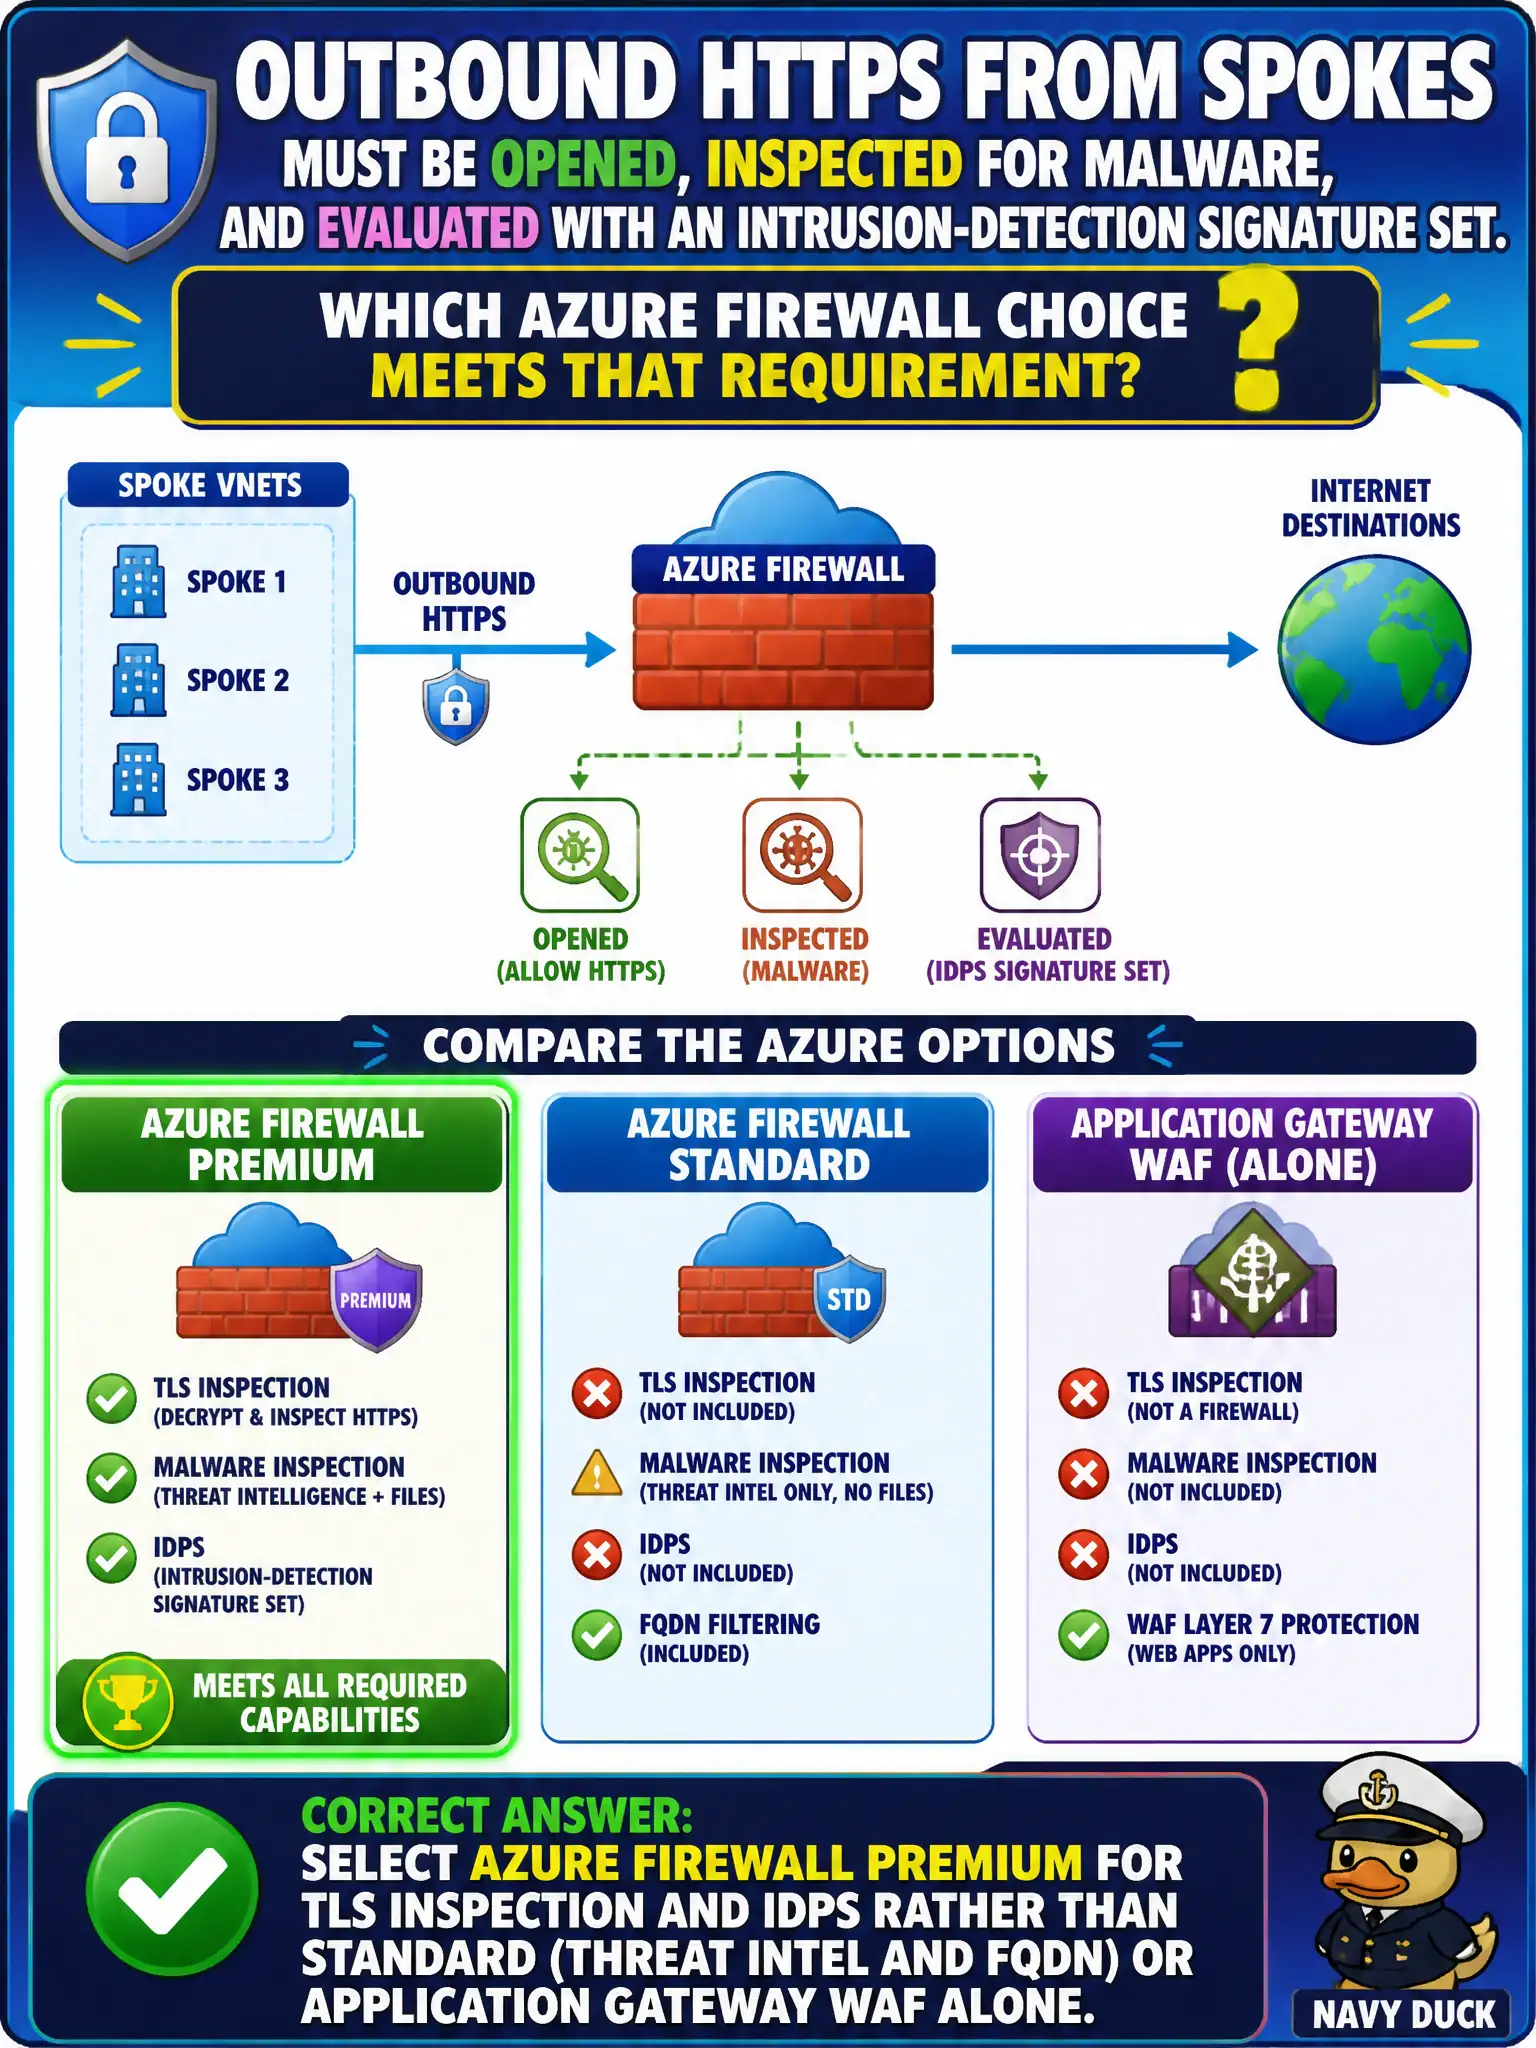
Outbound HTTPS from spokes must be opened, inspected for malware, and evaluated with an intrusion-detection signature set. Which Azure Firewall choice meets that requirement?
Select an answer to reveal the explanation.
Short Explanation
TLS inspection plus IDPS is Premium territory. Standard stops at threat intel and FQDN; WAF guards HTTP(S) to a web app—not every spoke’s outbound HTTPS.
Full Explanation
Outbound HTTPS from spokes that must be opened, inspected for malware, and evaluated with an intrusion-detection signature set requires Azure Firewall Premium. Premium provides TLS inspection and IDPS, which Standard’s threat intelligence and FQDN filtering do not fully replace when encrypted egress must be decrypted and signature-matched for canal workloads.
Selecting Azure Firewall Standard only fails by concept: Standard does not include TLS inspection and IDPS. Selecting Application Gateway WAF only fails by concept: WAF protects HTTP(S) applications behind a reverse proxy; it is not the centralized spoke-egress TLS inspection and IDPS control for arbitrary FQDN outbound. Selecting Azure Firewall Basic and enabling IDPS without upgrading fails by concept: Basic does not deliver Premium TLS inspection/IDPS capabilities.
Exam caveat: Premium = TLS inspection + IDPS; do not equate Standard threat intel/FQDN with full encrypted-egress inspection. Operational check: deploy or upgrade to Azure Firewall Premium, enable TLS inspection with the required intermediate certificate strategy, turn on IDPS in the appropriate mode, force spoke HTTPS through the firewall, and confirm inspection/IDPS telemetry for test traffic.